Impersonation
Real examples of Impersonation scams reported by the public. Learn what they look like so you can spot and avoid them.
 Click the image to view full size
96
Likely scamScam likelihood 96/100
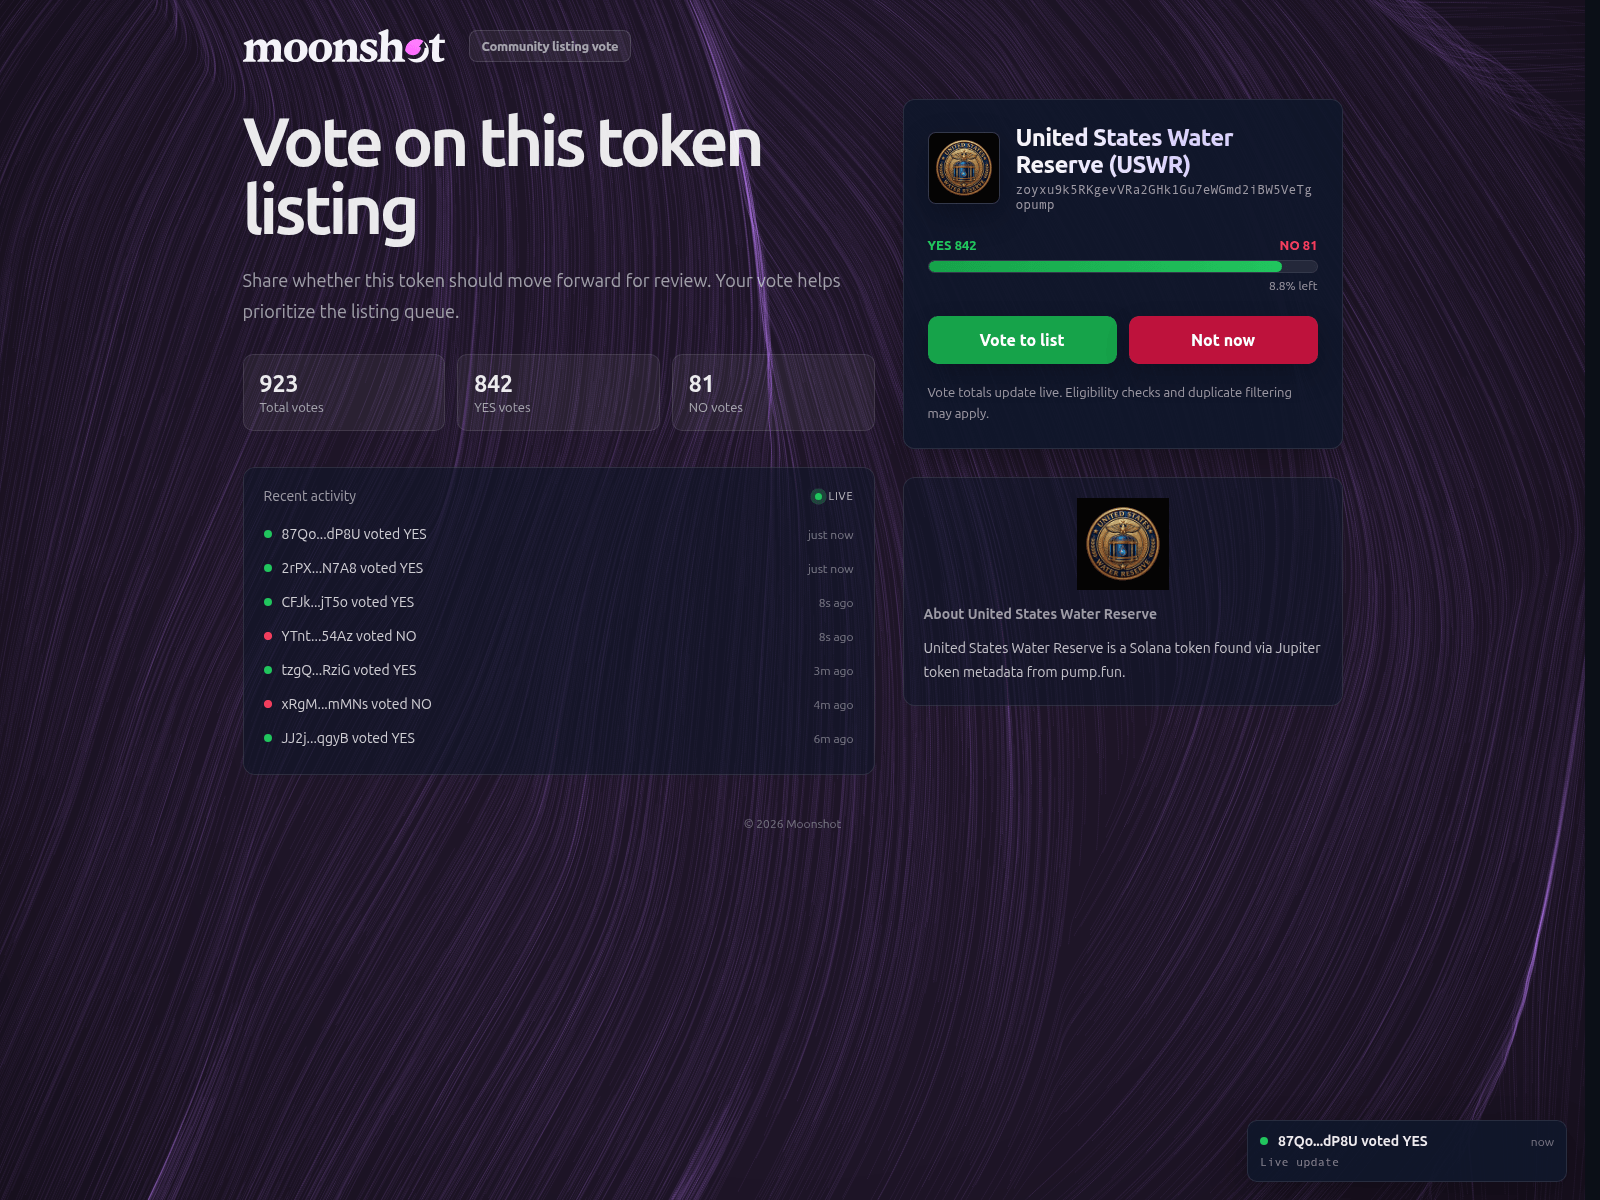
The page uses Moonshot branding and a cloned community listing vote flow, but the supplied domain vote-id-4xiwdi6og.portallogonapp.courses is unrelated to Moonshot. The token vote button, live activity, and government-style seal form a strong impersonation lure.
ImpersonationAnalyzed by ChatGPT 5.6-sol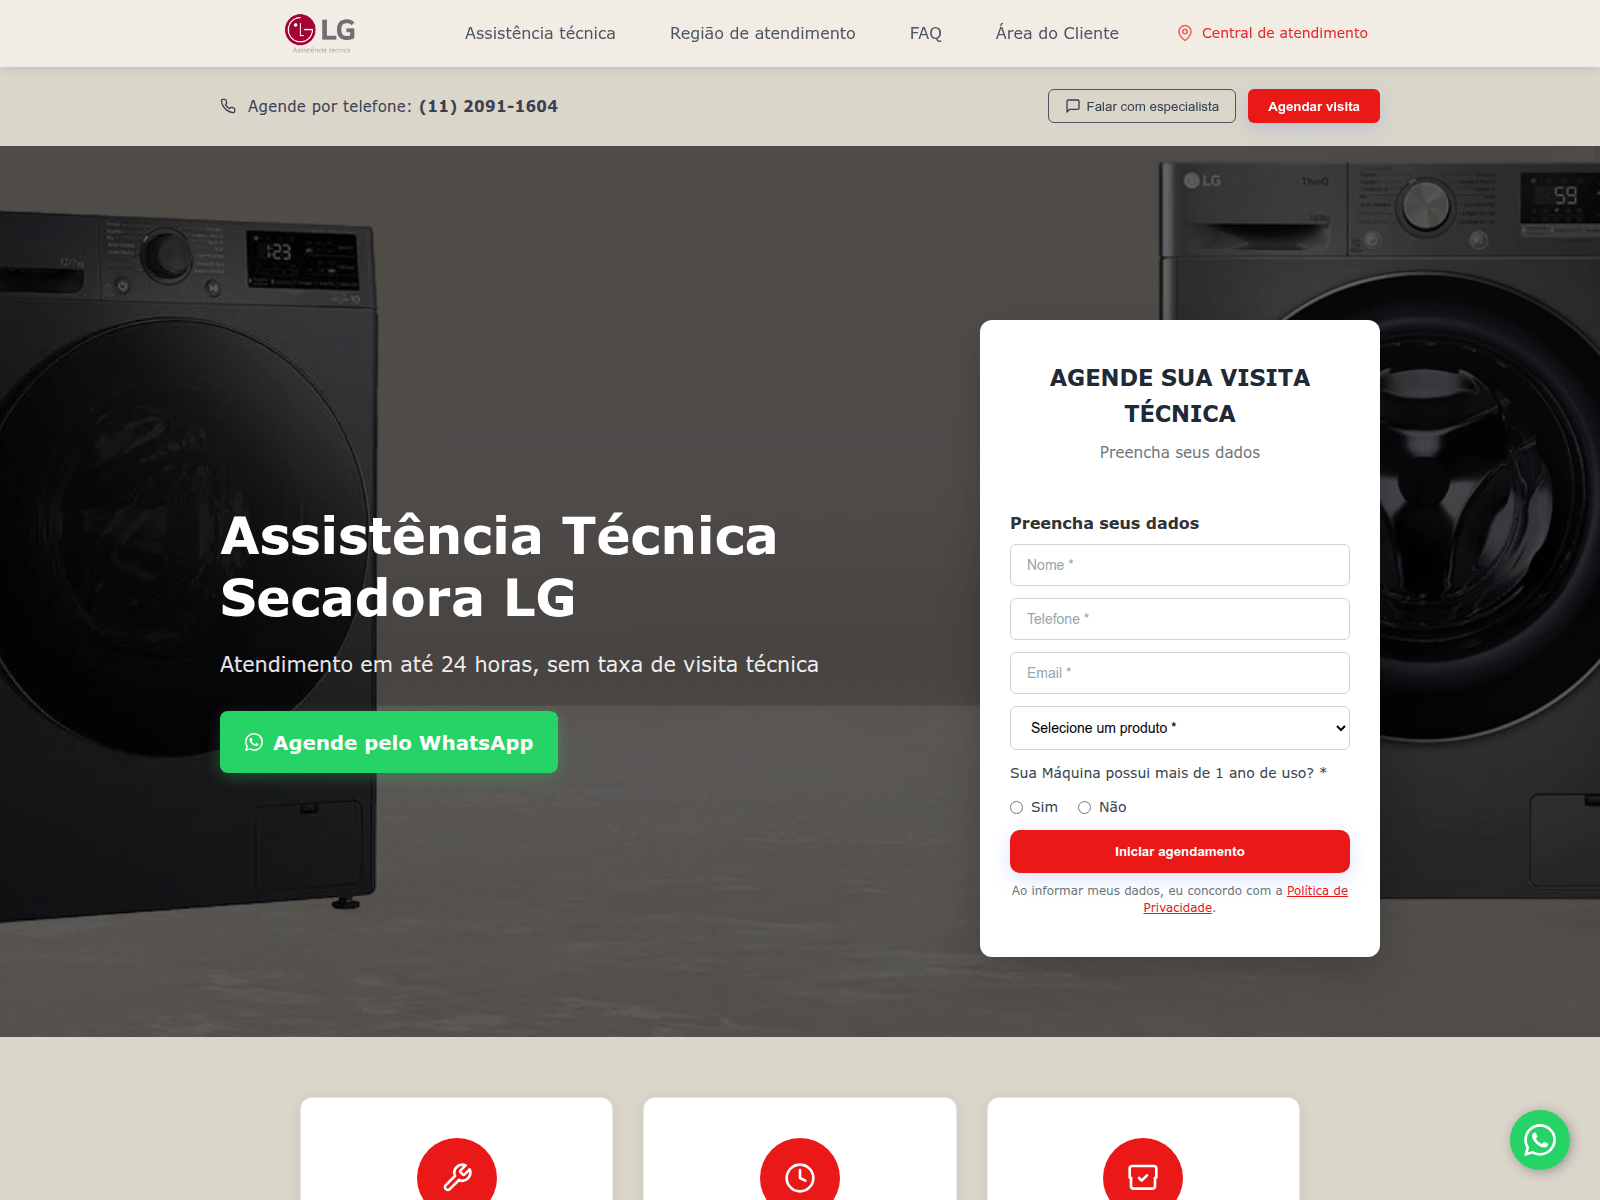 Click the image to view full size
96
Likely scamScam likelihood 96/100
The page uses LG branding and appliance imagery to present itself as LG technical support, while the supplied domain is not lg.com. It solicits names, phone numbers, emails, and WhatsApp contact to schedule service, indicating brand impersonation and data harvesting.
ImpersonationAnalyzed by ChatGPT 5.6-sol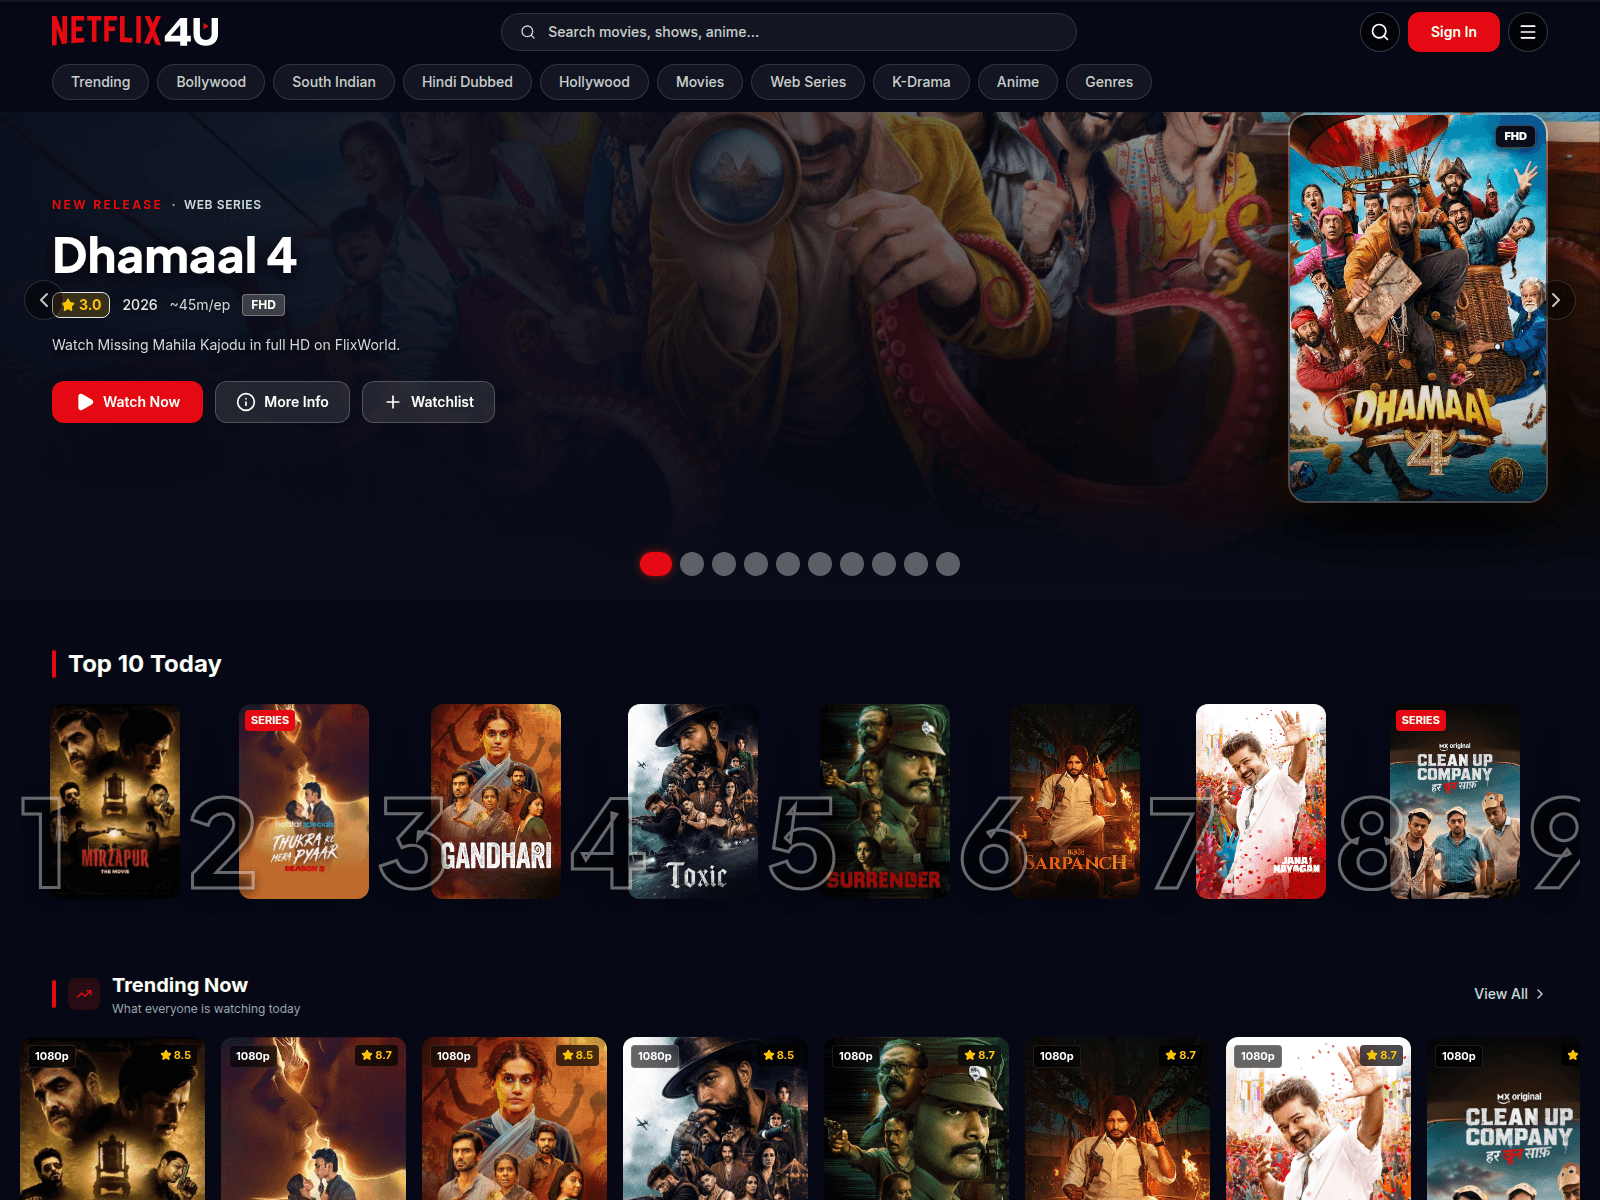 Click the image to view full size
94
Likely scamScam likelihood 94/100
The NETFLIX4U name, red Netflix-style logo, dark catalog interface, and Sign In button strongly imitate Netflix, while the supplied domain netflix4u.in is unrelated to official netflix.com. This is a clear brand-impersonation lure with potential credential-harvesting risk.
ImpersonationAnalyzed by ChatGPT 5.6-sol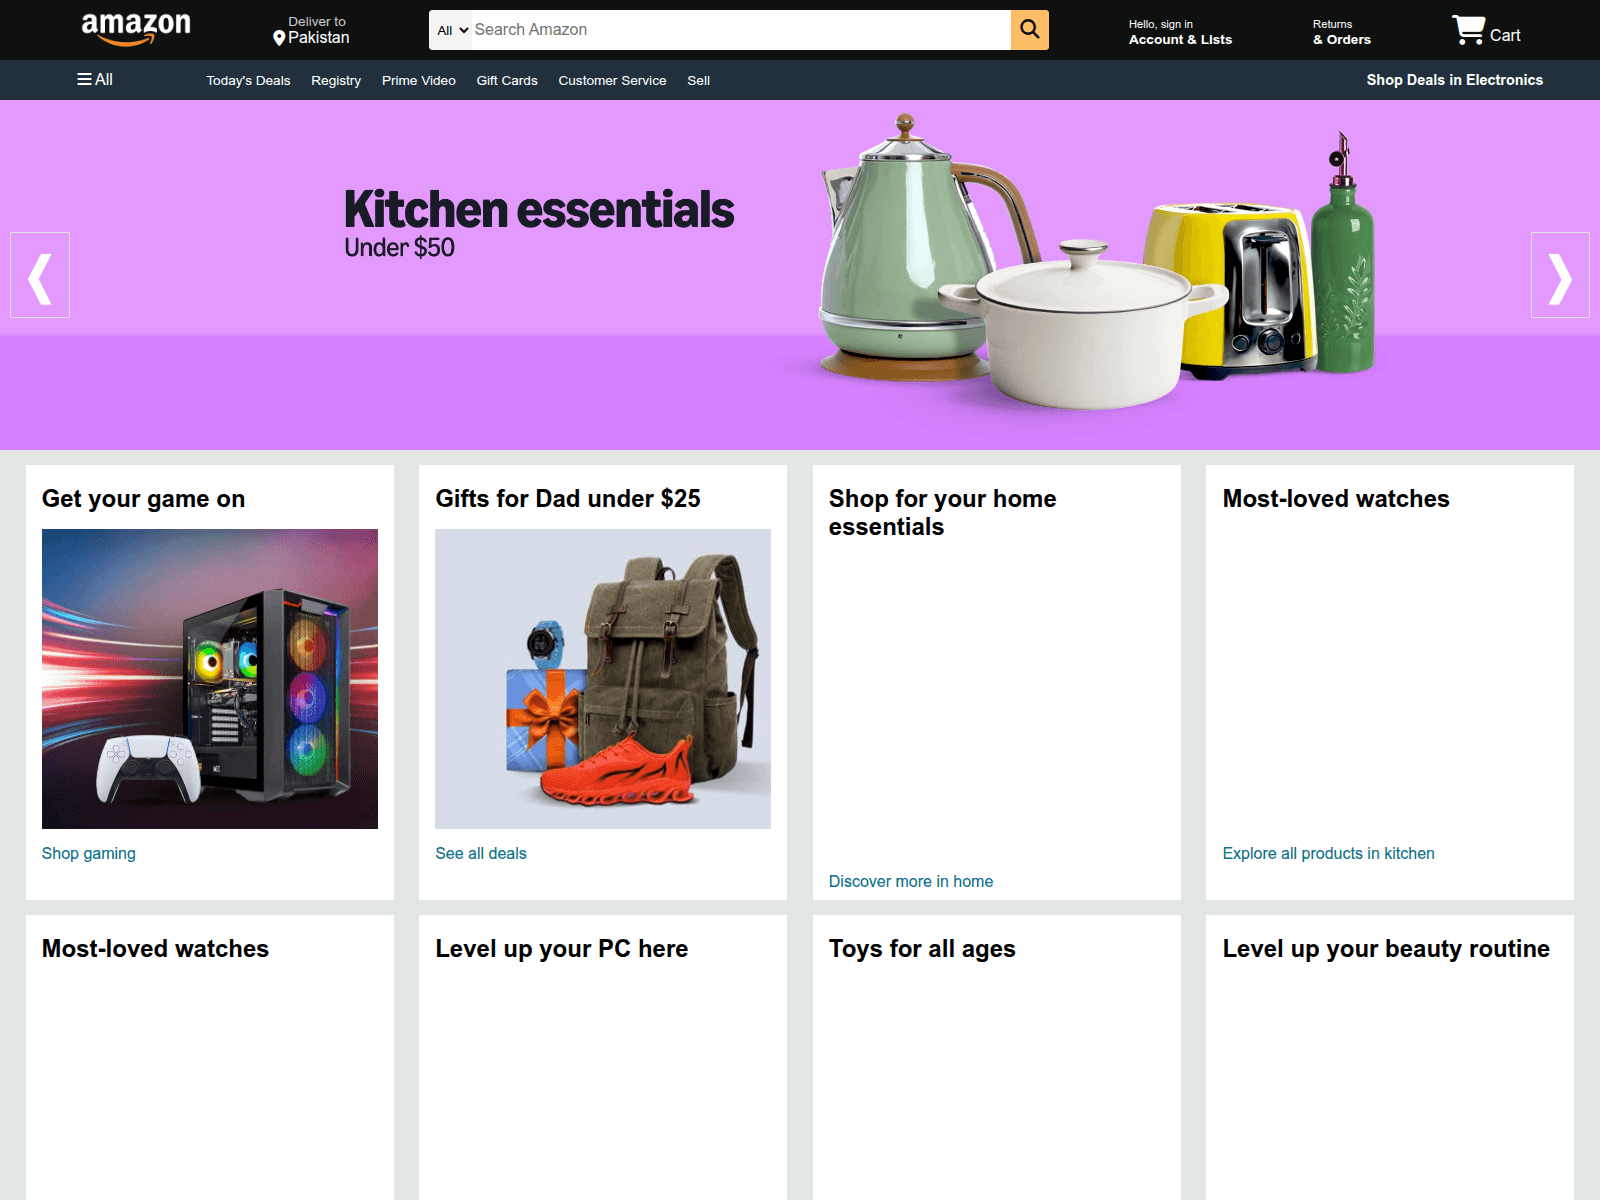 Click the image to view full size
96
Likely scamScam likelihood 96/100
The page copies Amazon's logo, search bar, account, orders, cart, navigation, and storefront design while metadata identifies the unrelated amazon-landing-page-umber.vercel.app domain. This brand-domain mismatch strongly indicates counterfeit Amazon impersonation.
ImpersonationAnalyzed by ChatGPT 5.6-sol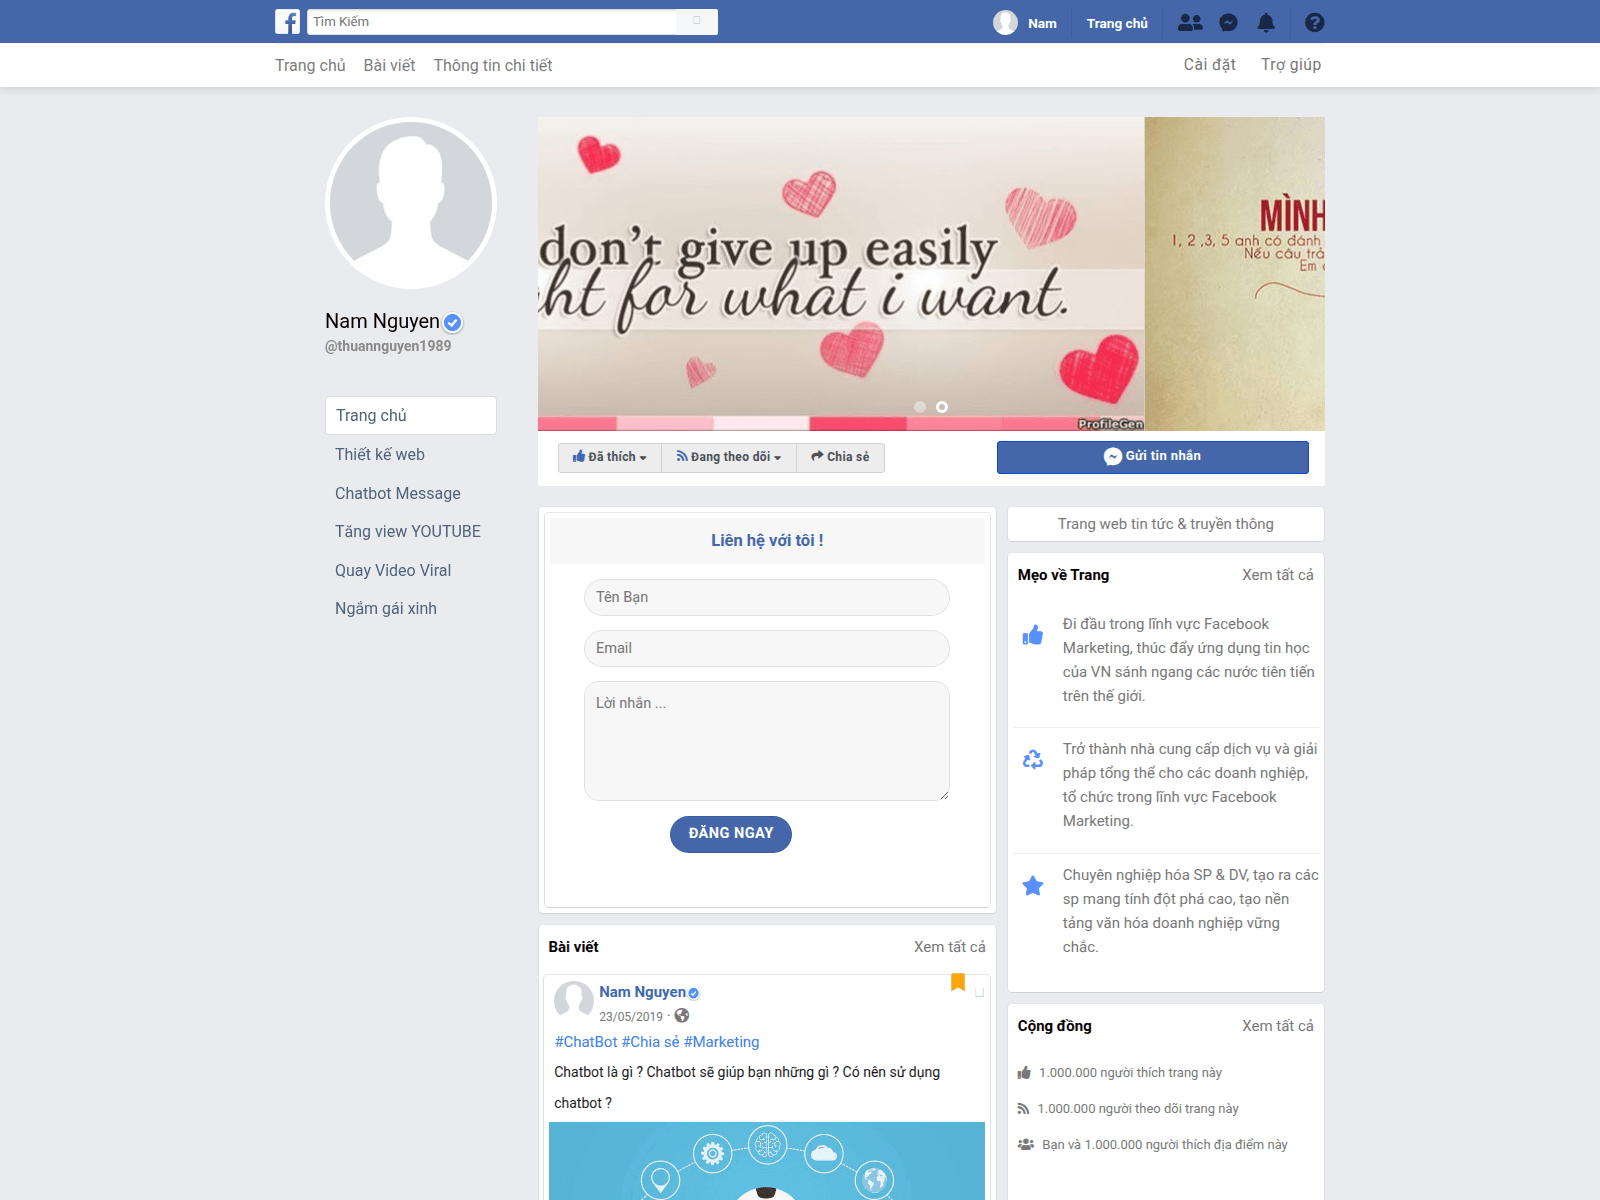 Click the image to view full size
96
Likely scamScam likelihood 96/100
The page copies Facebook's logo, navigation, profile layout, Messenger styling, and verified badge while metadata identifies the unrelated domain facebook.webstore.vn. This clear brand-domain mismatch and contact form indicate interface impersonation and potential data harvesting.
ImpersonationAnalyzed by ChatGPT 5.6-sol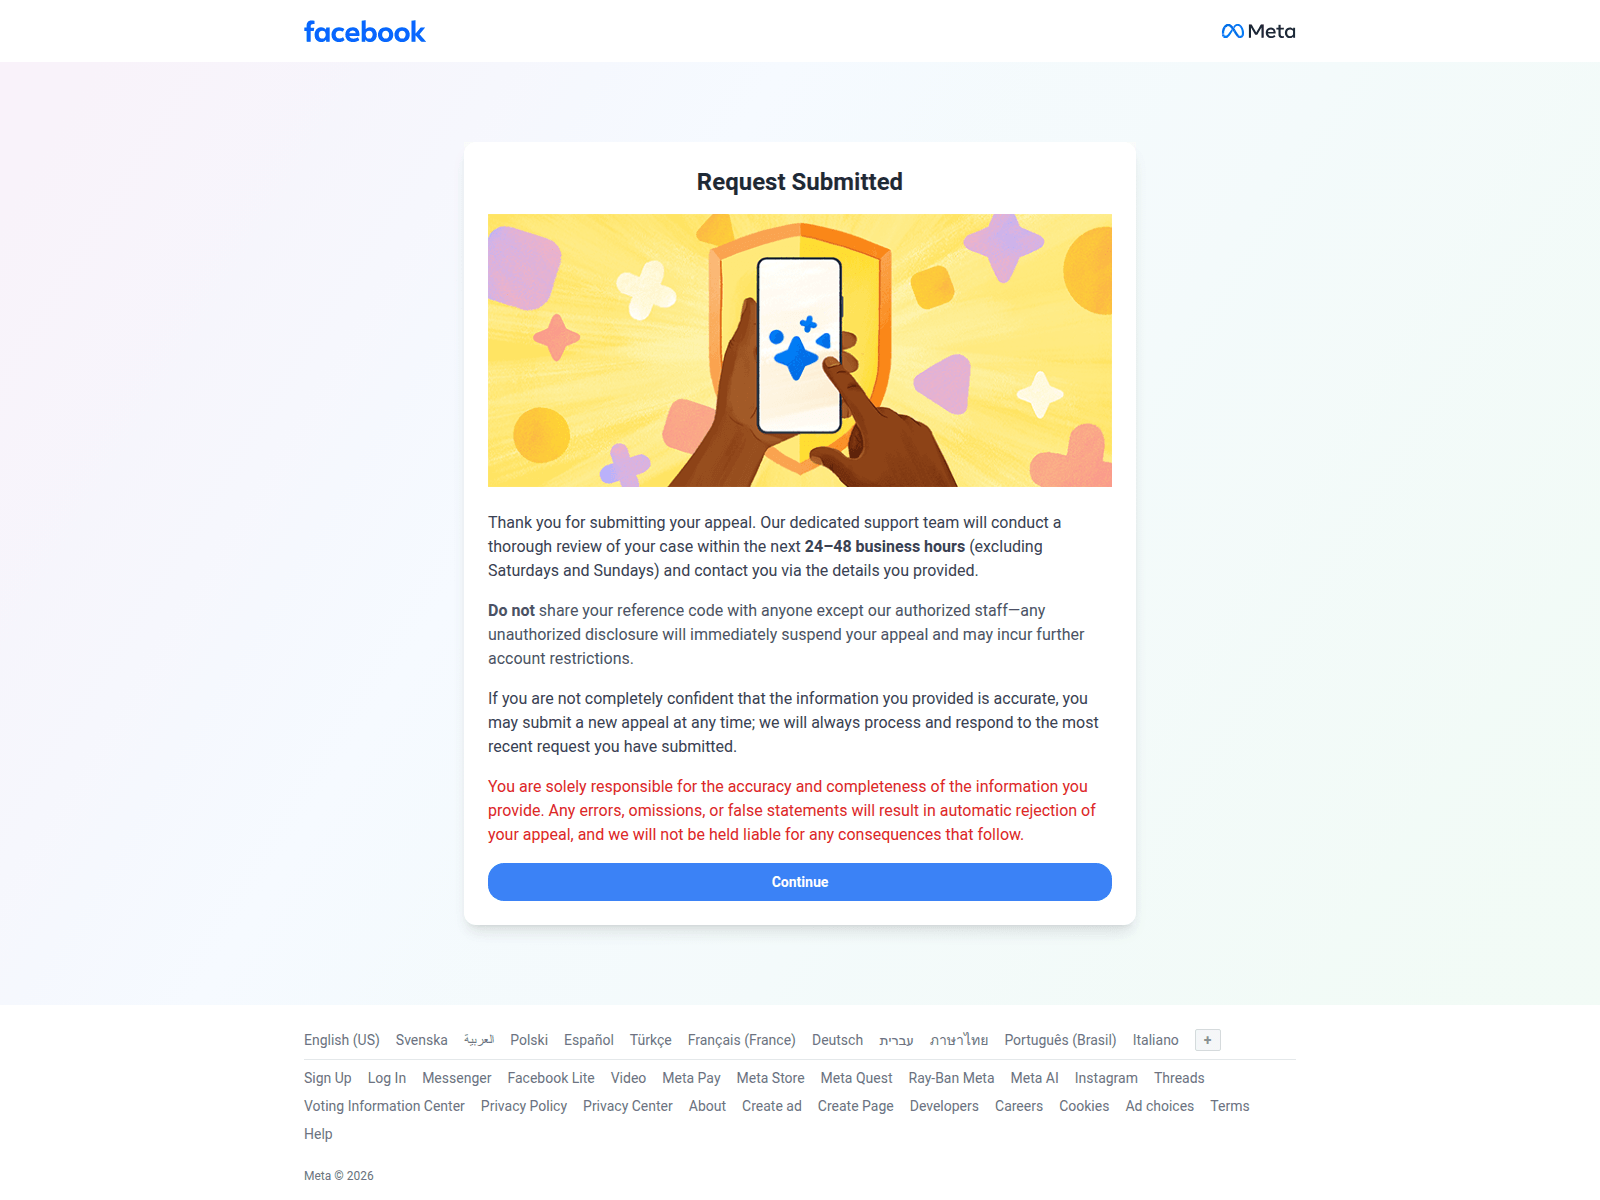 Click the image to view full size
98
Likely scamScam likelihood 98/100
The page impersonates Facebook and Meta with official logos and an appeal confirmation, while hosted on an unrelated pages.dev domain. The reference-code secrecy warning, account-restriction pressure, and Continue button strongly indicate account-appeal phishing.
ImpersonationAnalyzed by ChatGPT 5.6-sol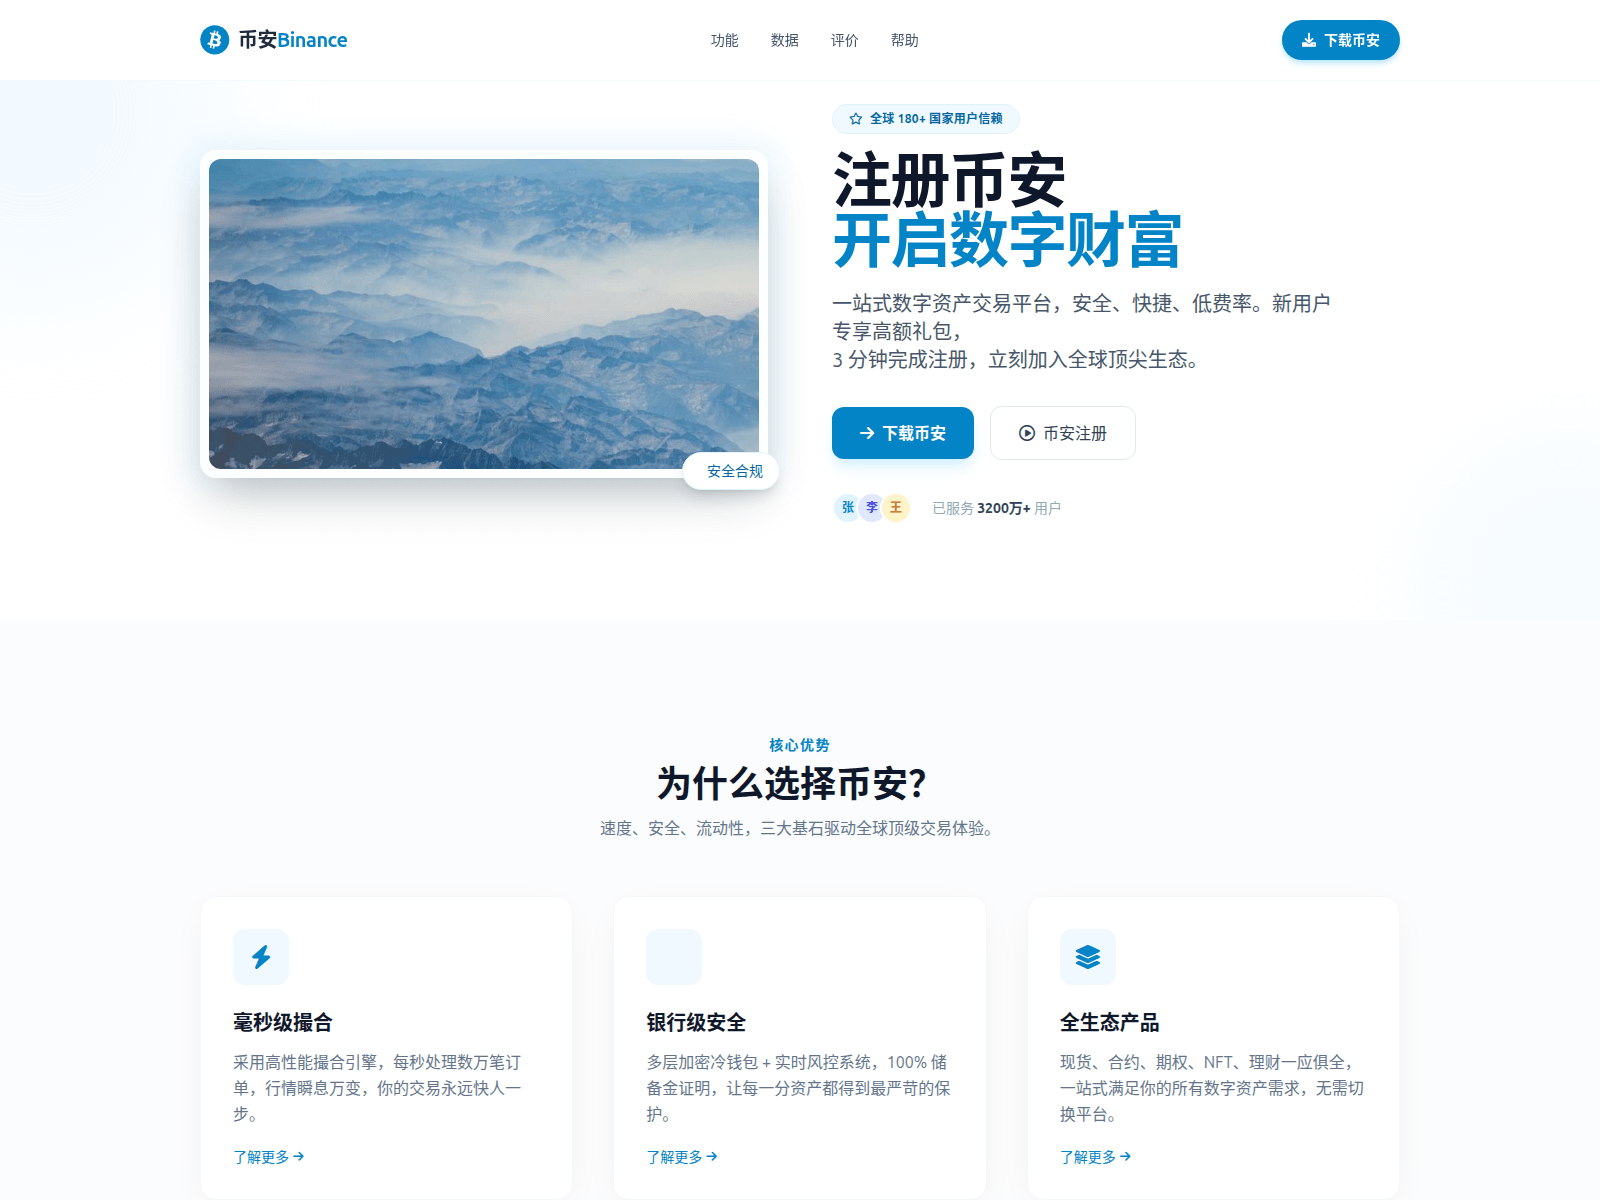 Click the image to view full size
98
Likely scamScam likelihood 98/100
The page uses Binance branding and promotes registration, app downloads, newcomer gifts, and digital-asset trading. Metadata identifies the domain as pug.bbinance.com.cn, not official binance.com, creating a clear crypto impersonation and phishing funnel.
ImpersonationAnalyzed by ChatGPT 5.6-sol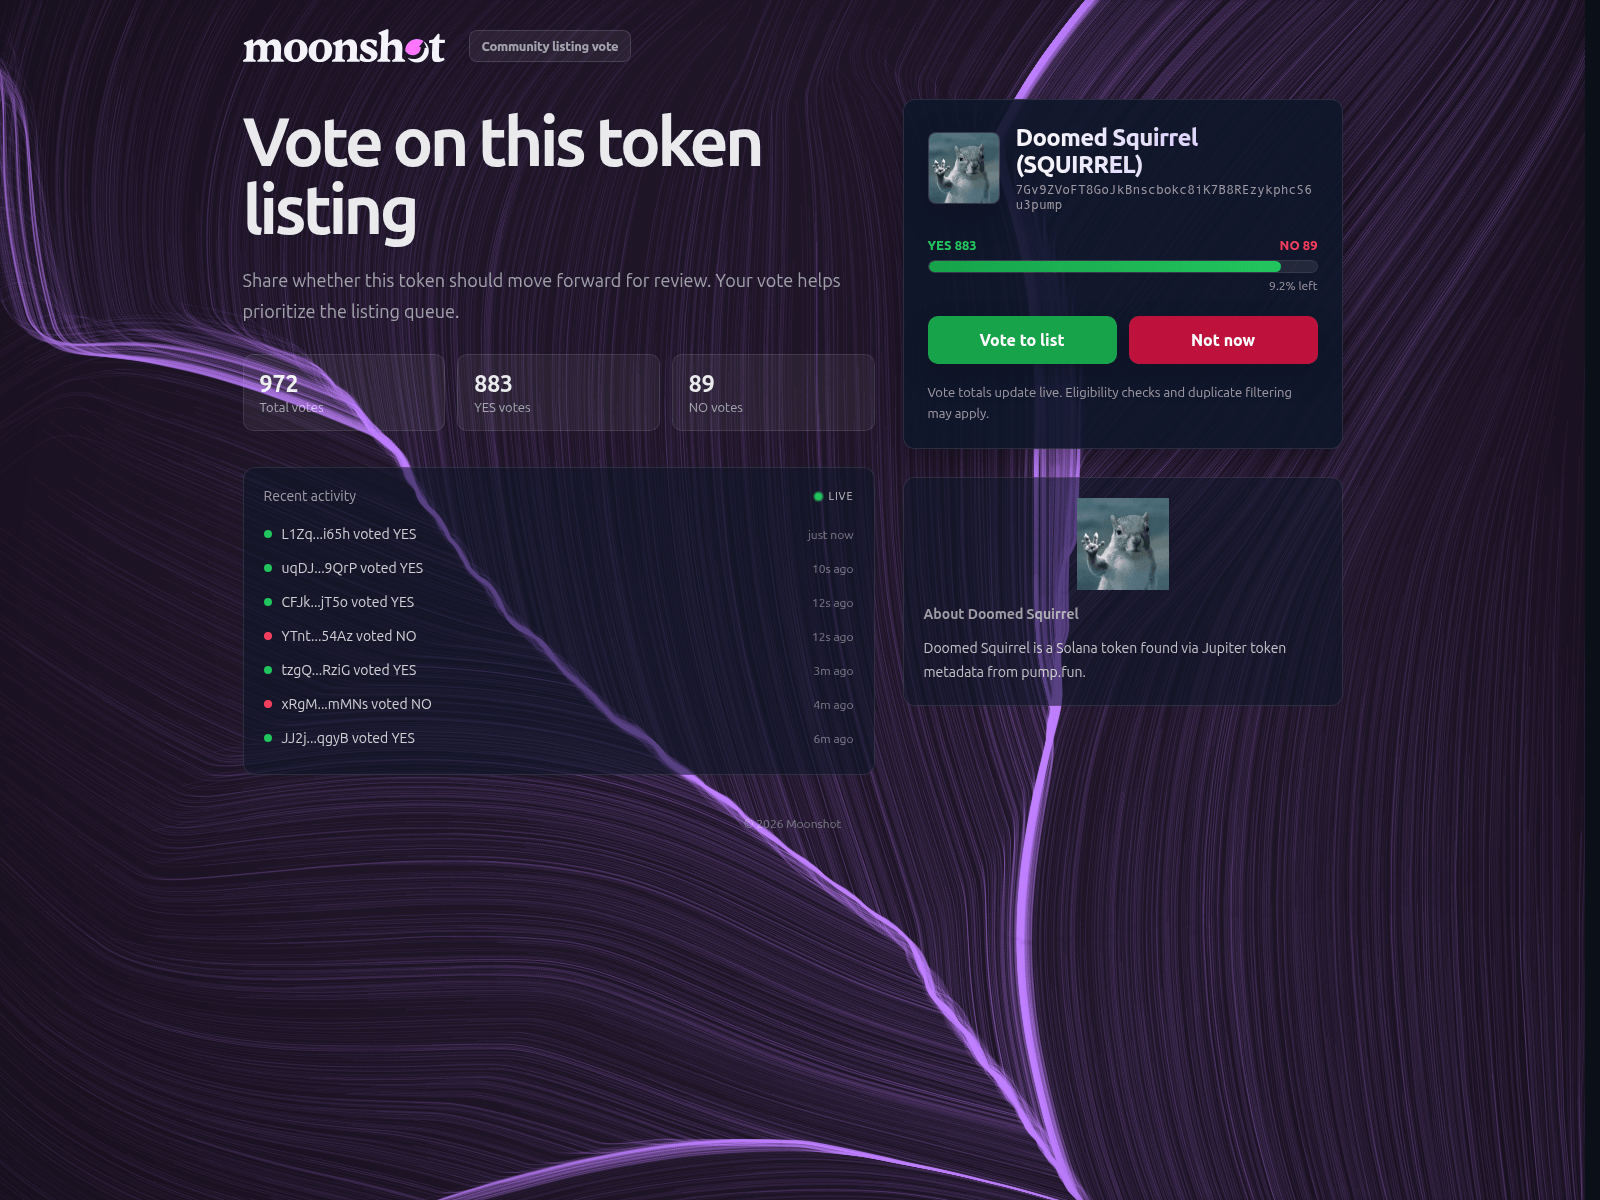 Click the image to view full size
97
Likely scamScam likelihood 97/100
The page uses Moonshot branding and a community token-voting flow, but the supplied domain vote-id-gfkkcrku.portallogonapp.surf is unrelated to Moonshot. This clear brand-domain mismatch indicates an impersonation lure likely targeting crypto users.
ImpersonationAnalyzed by ChatGPT 5.6-sol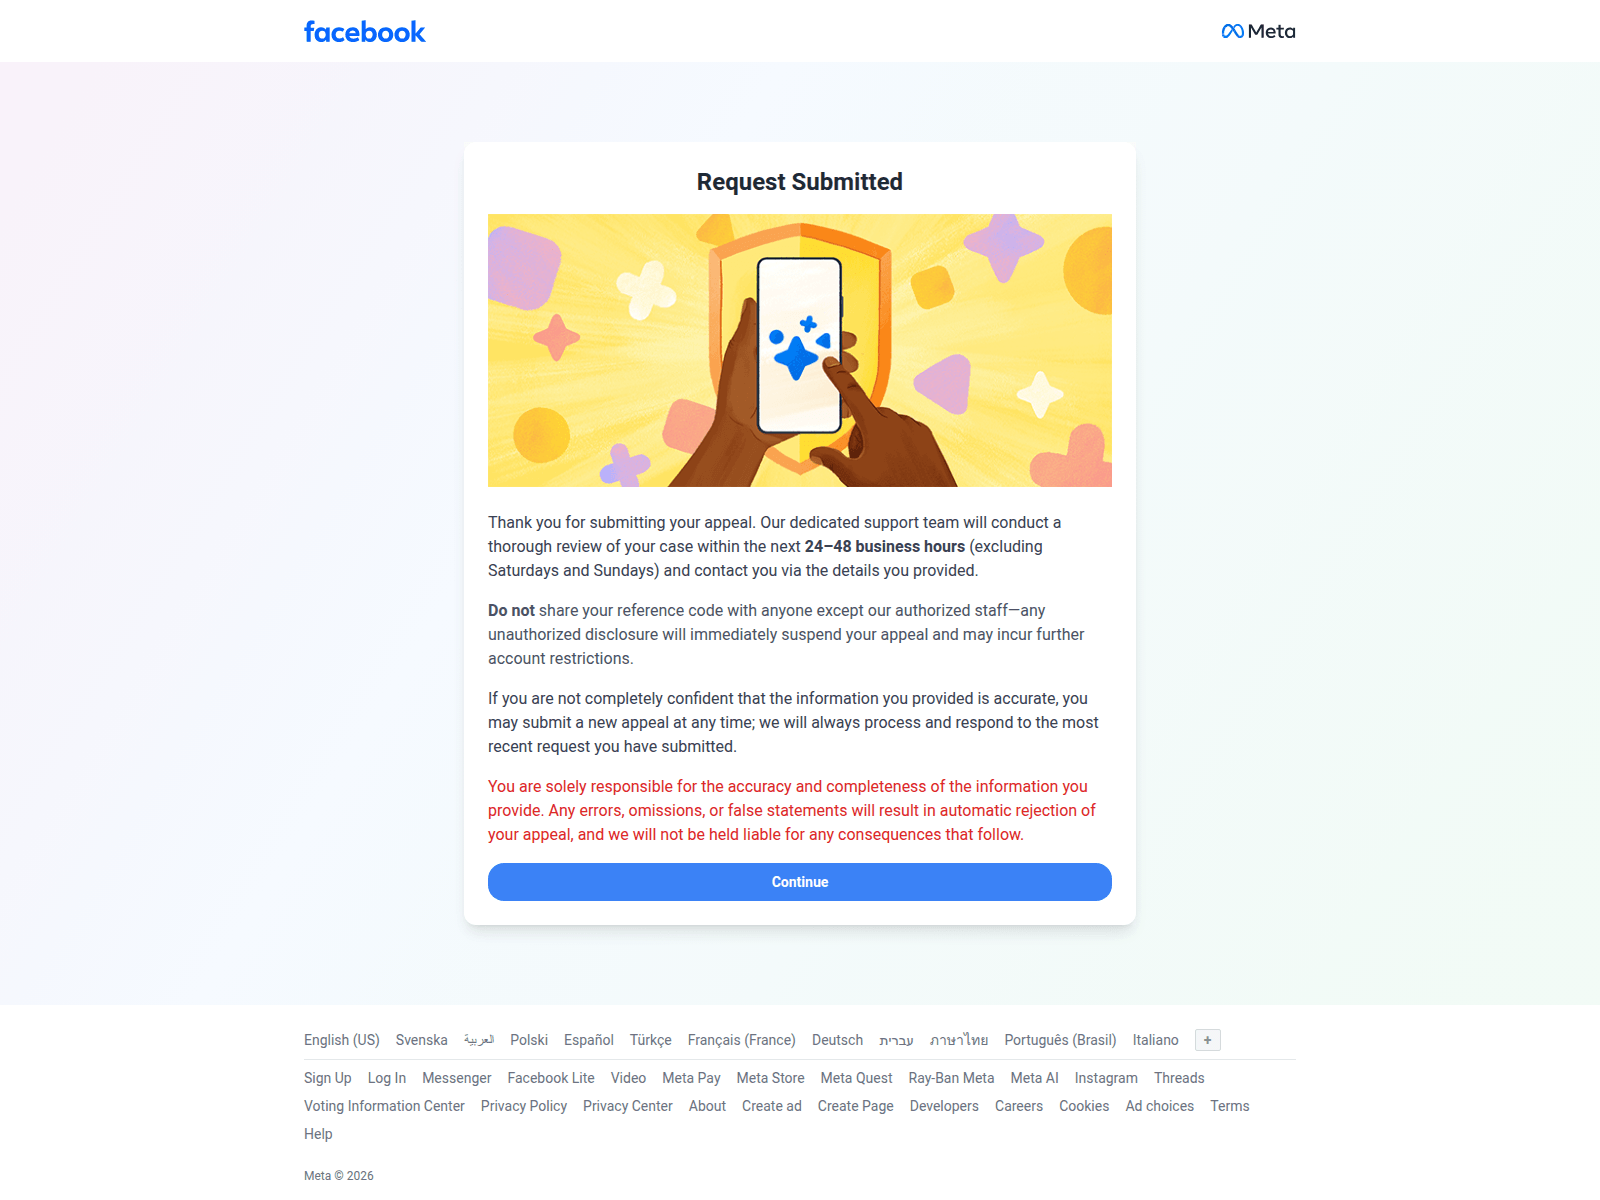 Click the image to view full size
98
Likely scamScam likelihood 98/100
The page impersonates Facebook and Meta with their logos and an account-appeal workflow, but the supplied pages.dev domain is unrelated to facebook.com. The secrecy warning, threat of restrictions, and Continue button strongly indicate phishing.
ImpersonationAnalyzed by ChatGPT 5.6-sol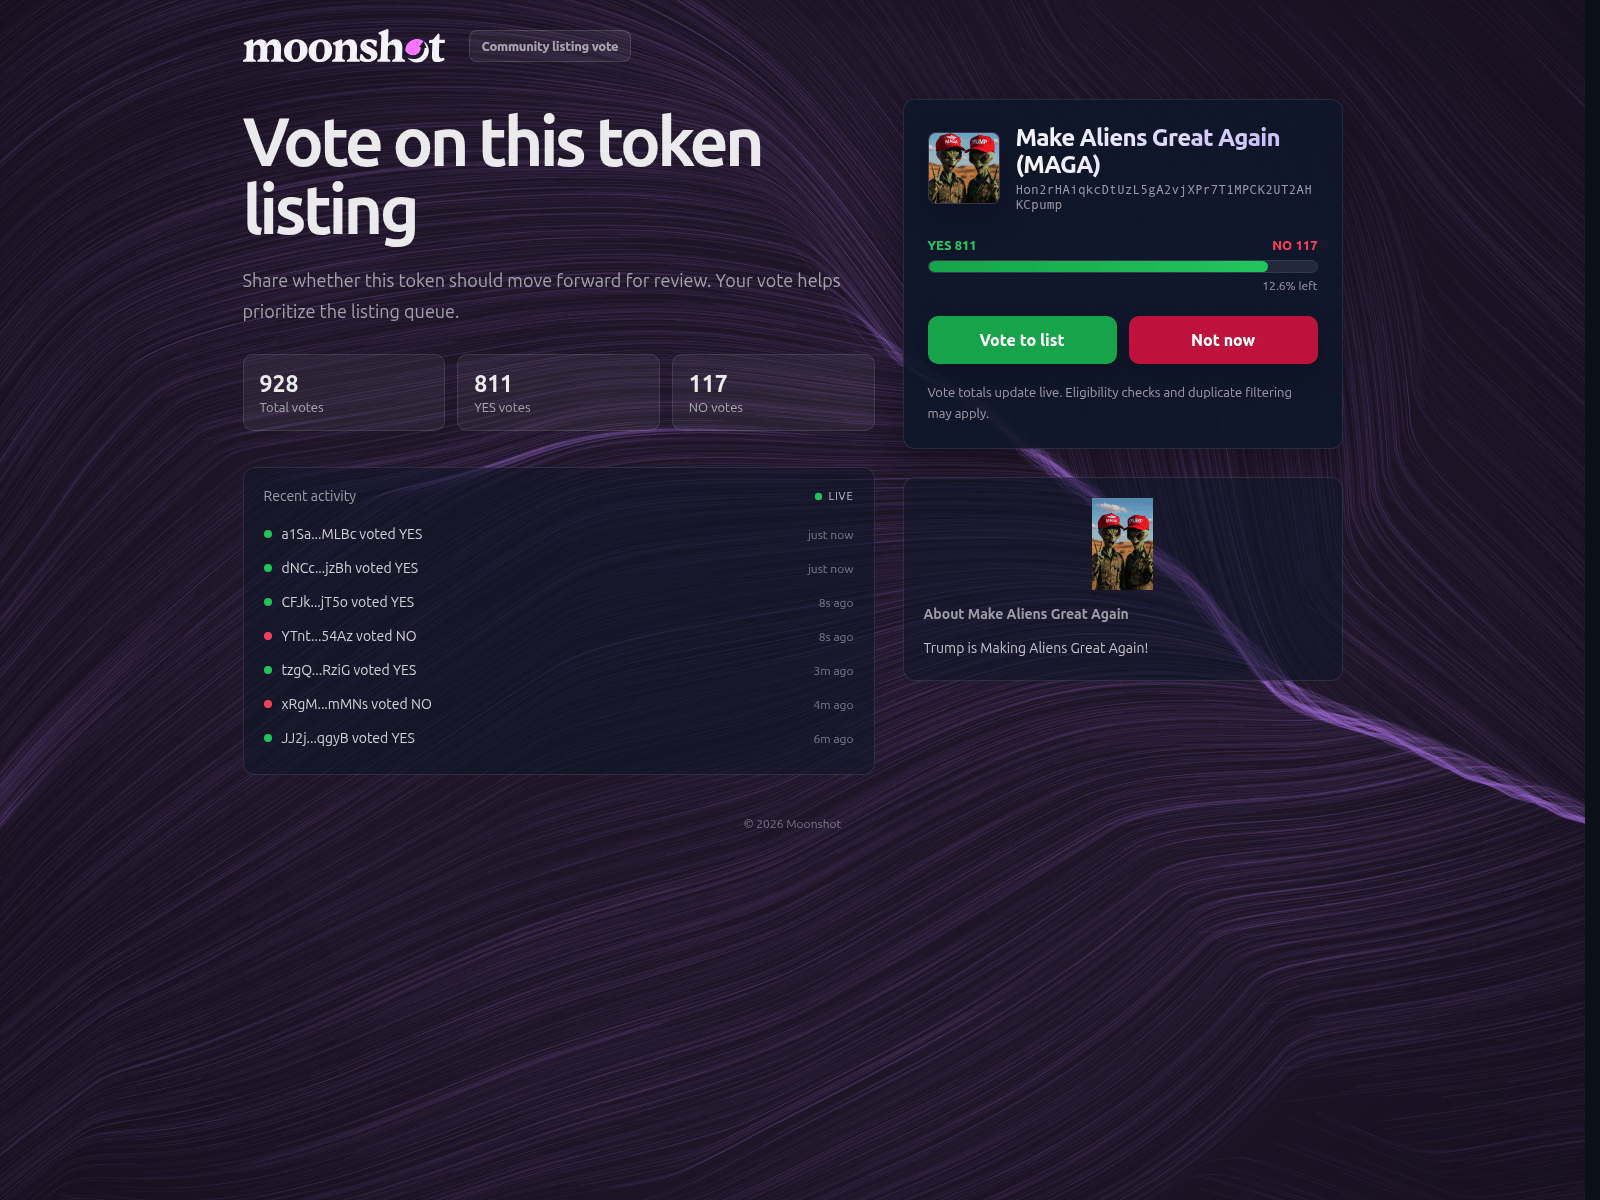 Click the image to view full size
96
Likely scamScam likelihood 96/100
The page uses Moonshot branding and a token-listing vote lure, but metadata identifies the unrelated lookalike domain vote-id-u0ipot.portallogonapp.lol. This brand-domain mismatch strongly indicates impersonation designed to bait crypto interactions.
ImpersonationAnalyzed by ChatGPT 5.6-sol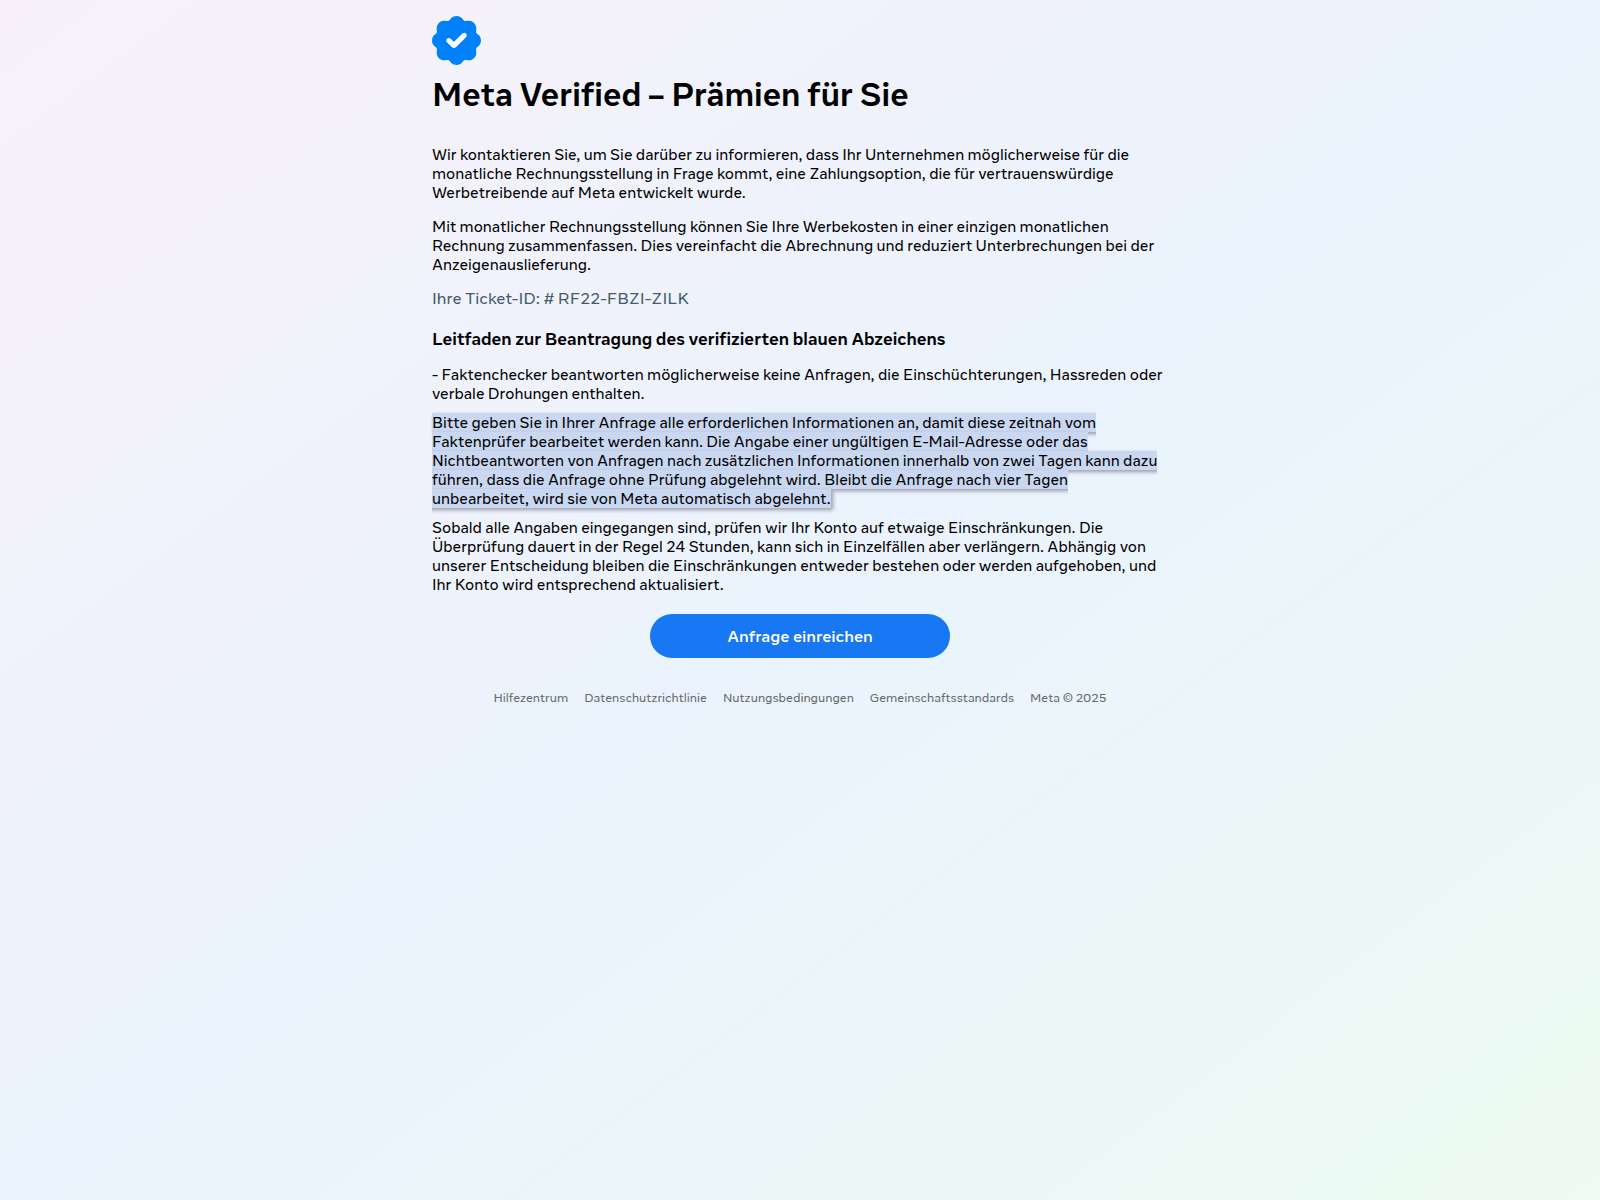 Click the image to view full size
98
Likely scamScam likelihood 98/100
The page impersonates Meta using its name, verified badge, ticket ID, and Meta-styled footer. It pressures users to submit information within two days via 'Anfrage einreichen', while metadata identifies the unrelated vercel.app domain rather than meta.com or facebook.com.
ImpersonationAnalyzed by ChatGPT 5.6-sol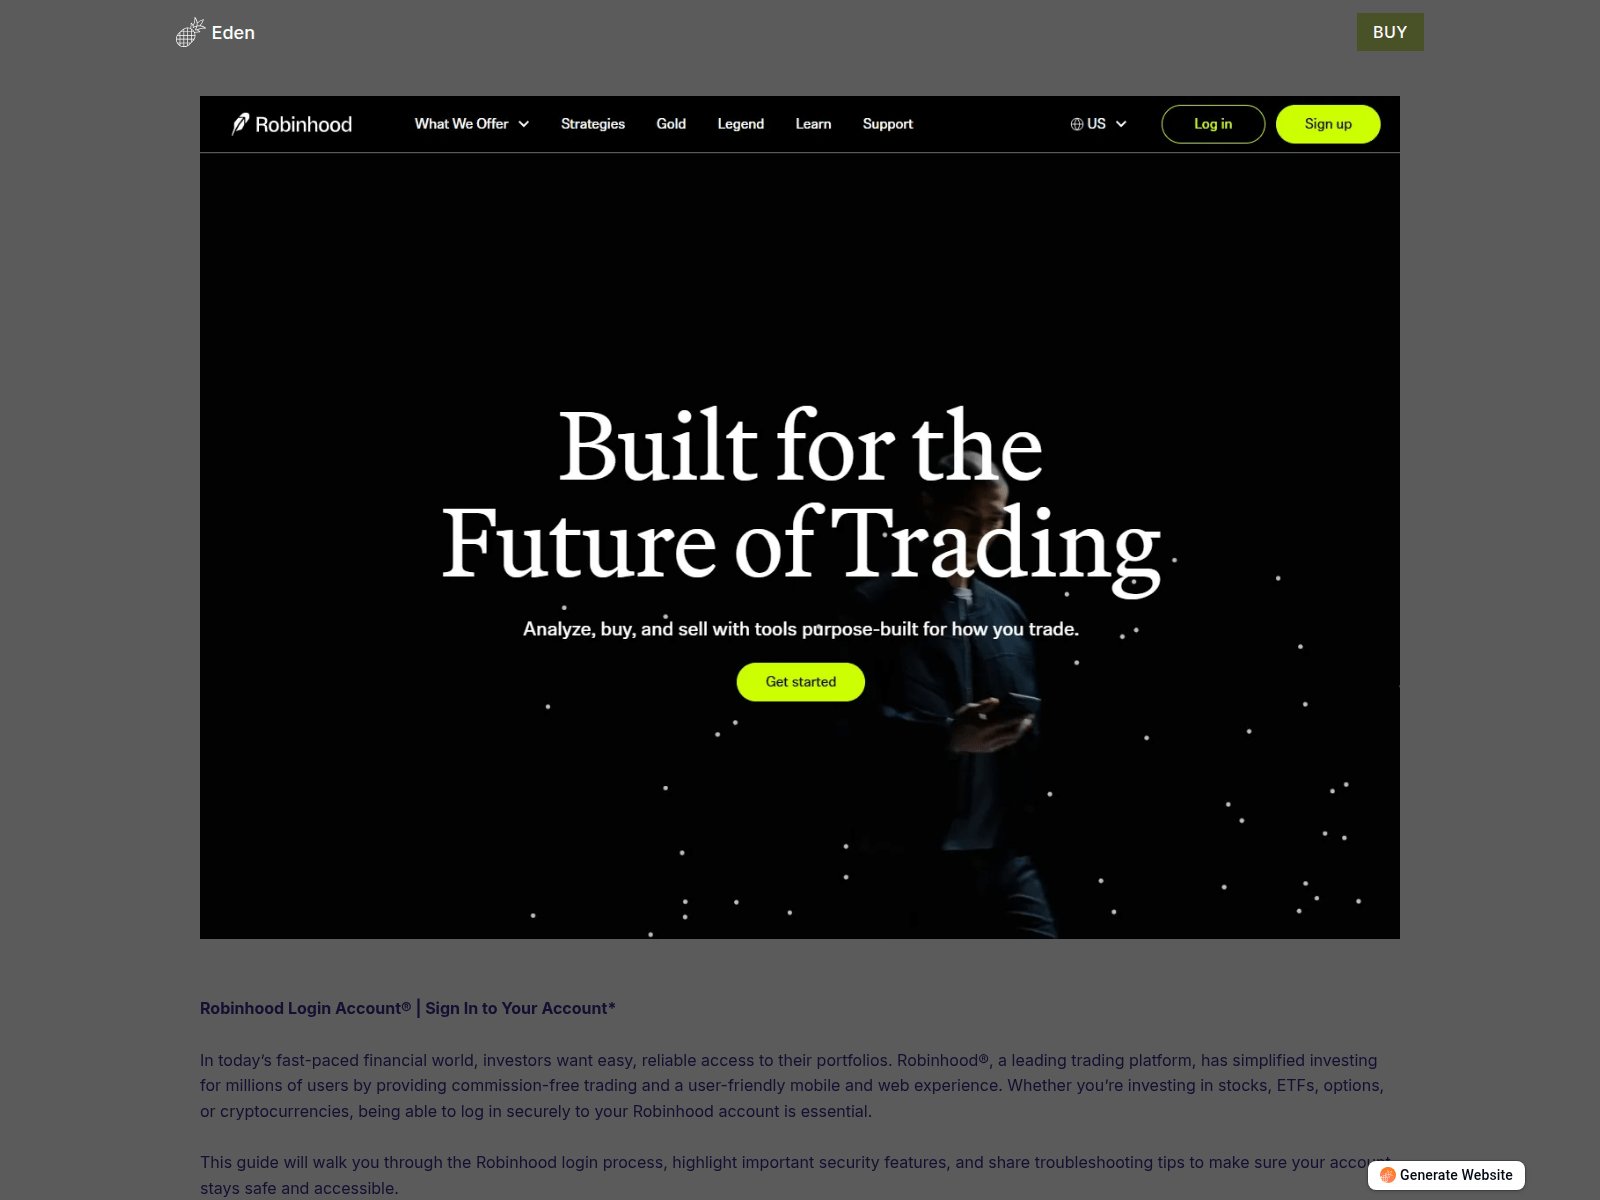 Click the image to view full size
94
Likely scamScam likelihood 94/100
The page reproduces Robinhood branding and presents Log in, Sign up, and Get started actions inside an unrelated Eden site. The supplied hfm.bbinance.com.cn domain matches neither Robinhood nor Binance, strongly indicating financial-brand impersonation and credential phishing.
ImpersonationAnalyzed by ChatGPT 5.6-sol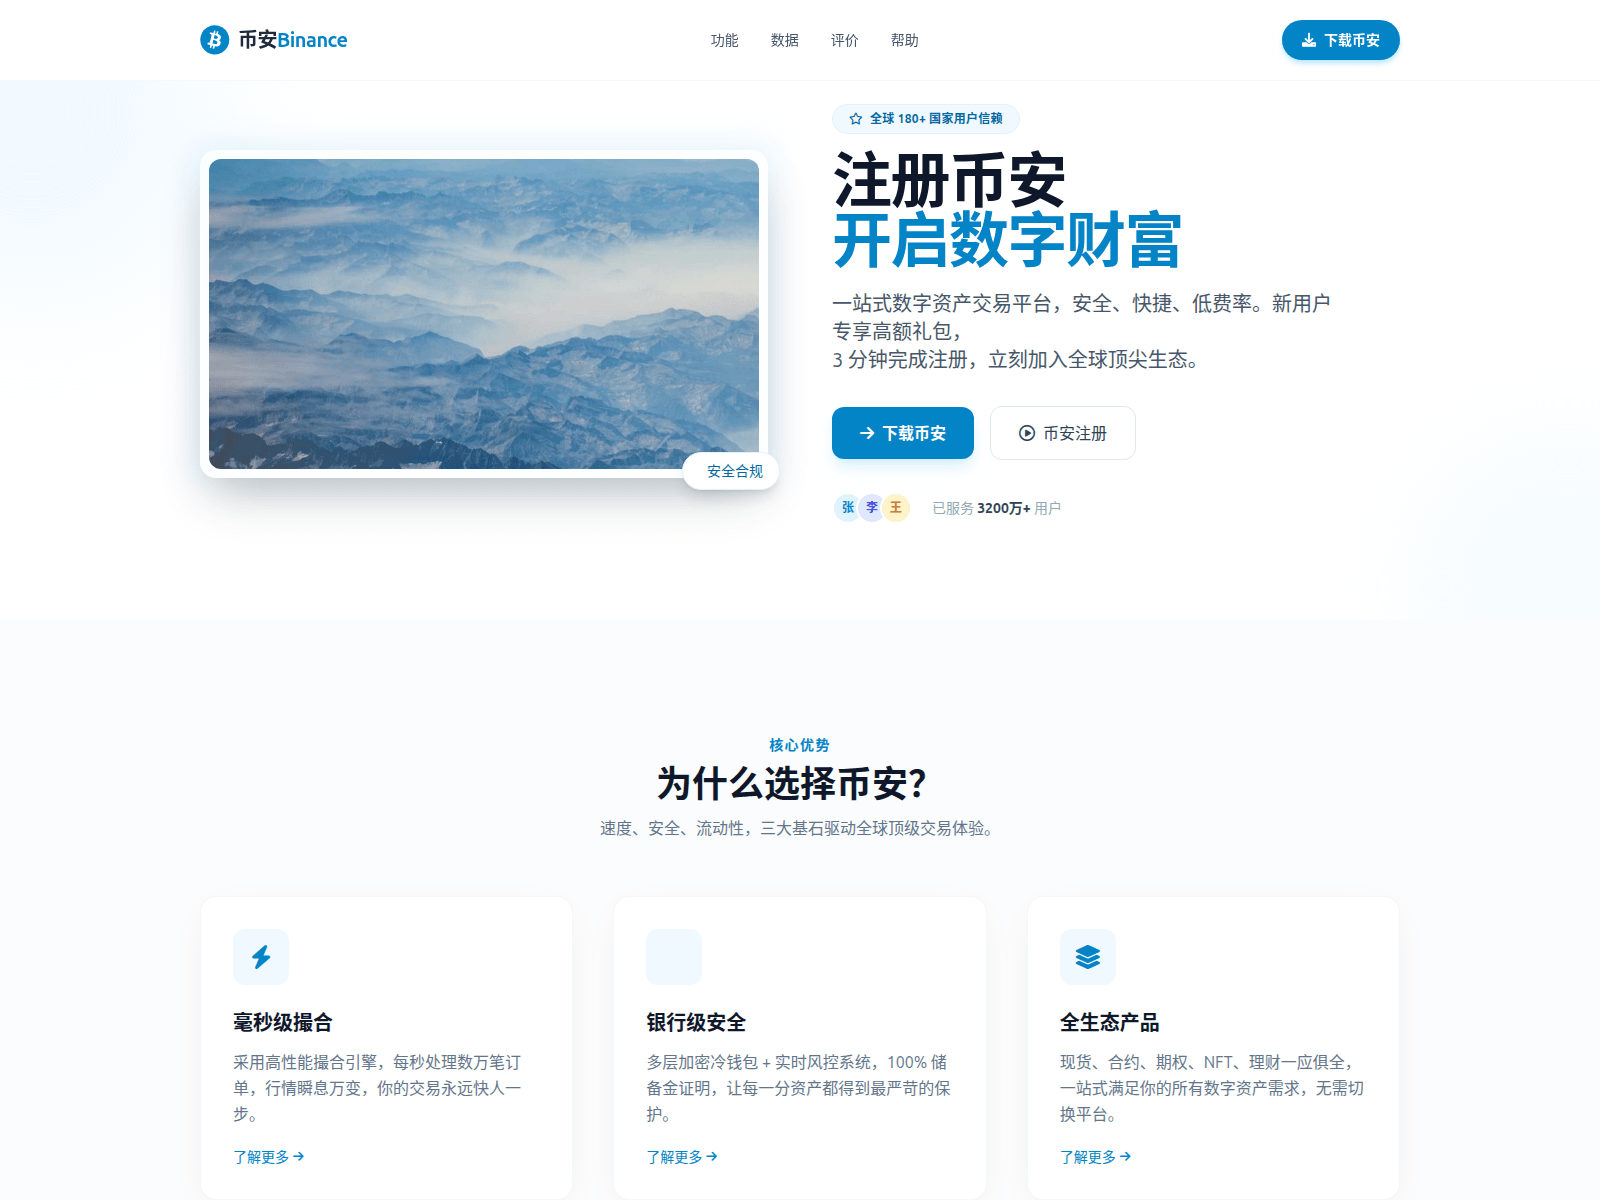 Click the image to view full size
97
Likely scamScam likelihood 97/100
The page uses Binance branding and claims global trust, bank-grade security, signup gifts, and 32 million users while pushing registration and app downloads. Metadata identifies the unrelated domain ezl.cbinance.com.cn rather than official binance.com, indicating crypto impersonation.
ImpersonationAnalyzed by ChatGPT 5.6-sol Click the image to view full size
98
Likely scamScam likelihood 98/100
The page uses Meta Verified branding and a rewards lure with a submit button, but metadata identifies the unrelated vercel.app domain rather than meta.com. This brand-domain mismatch strongly indicates Meta impersonation and credential phishing.
ImpersonationAnalyzed by ChatGPT 5.6-sol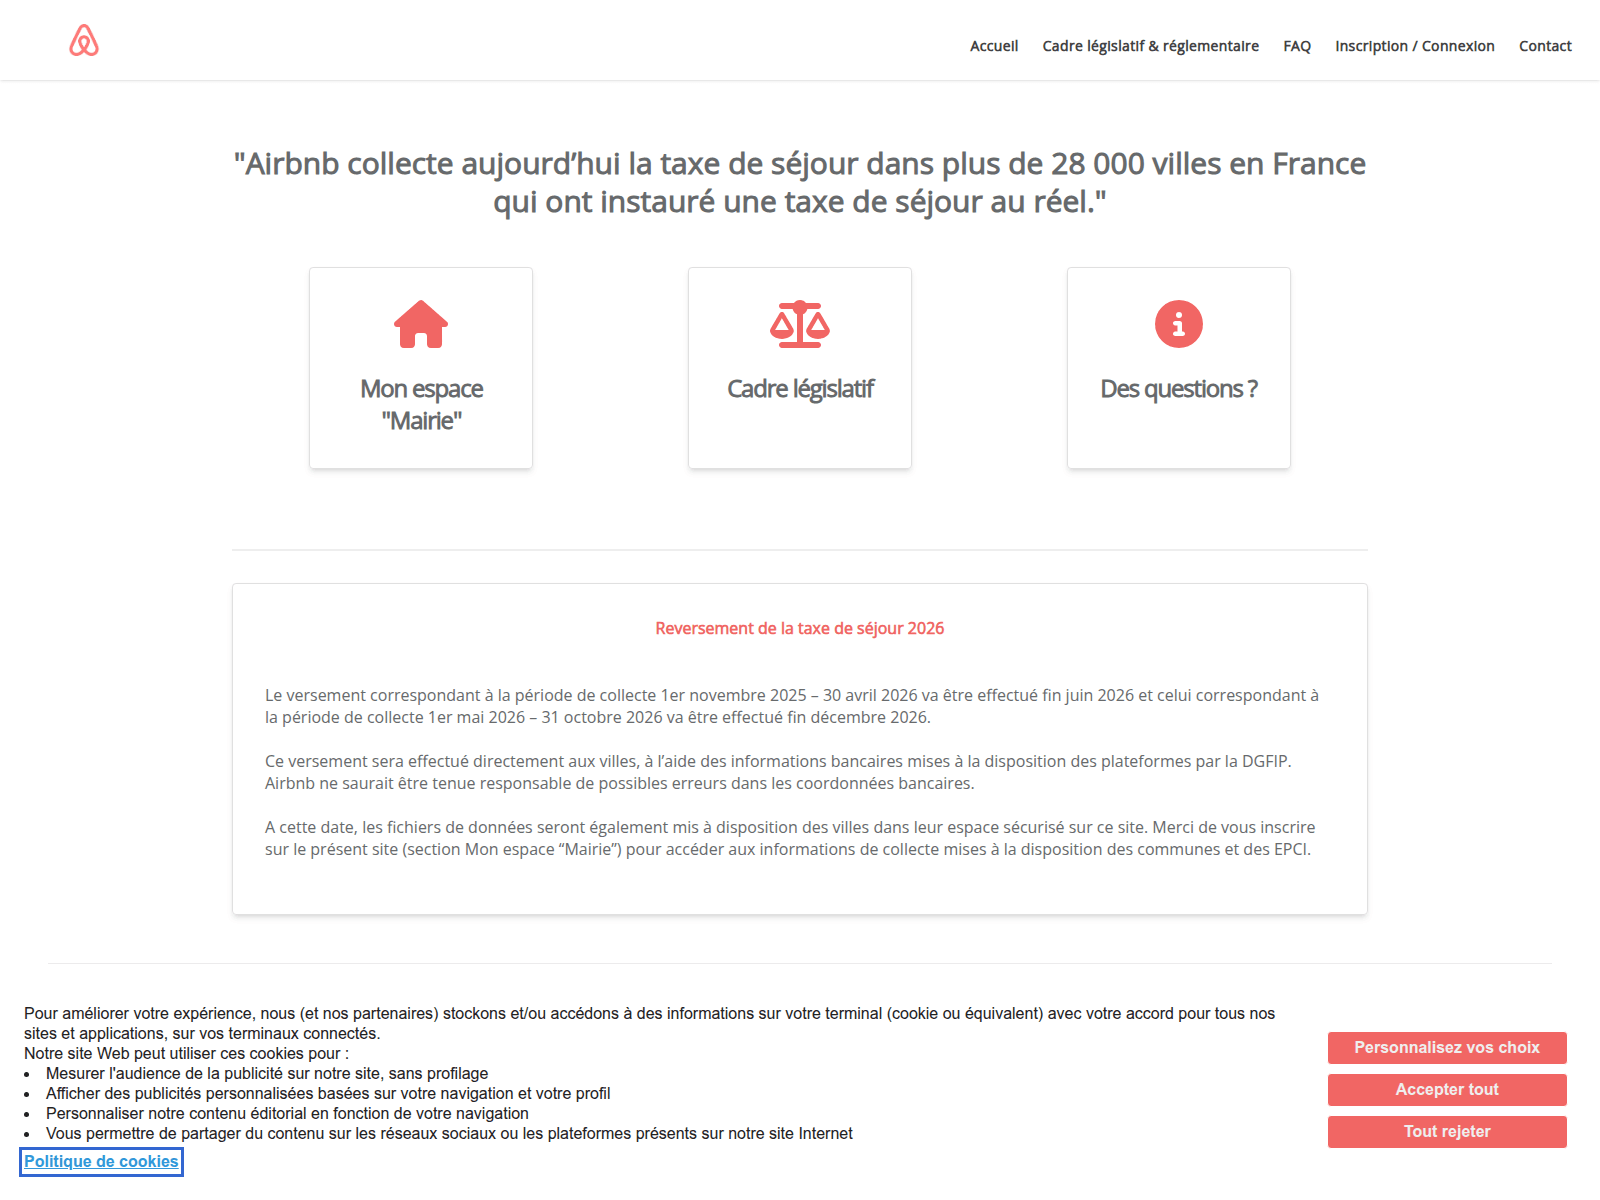 Click the image to view full size
98
Likely scamScam likelihood 98/100
The page uses Airbnb's logo and claims to manage municipal tourist-tax payments while directing officials to registration/login. The domain taxedesejour-airbnb.fr is not Airbnb's official domain, creating a clear brand-impersonation and data-harvesting risk.
ImpersonationAnalyzed by ChatGPT 5.6-sol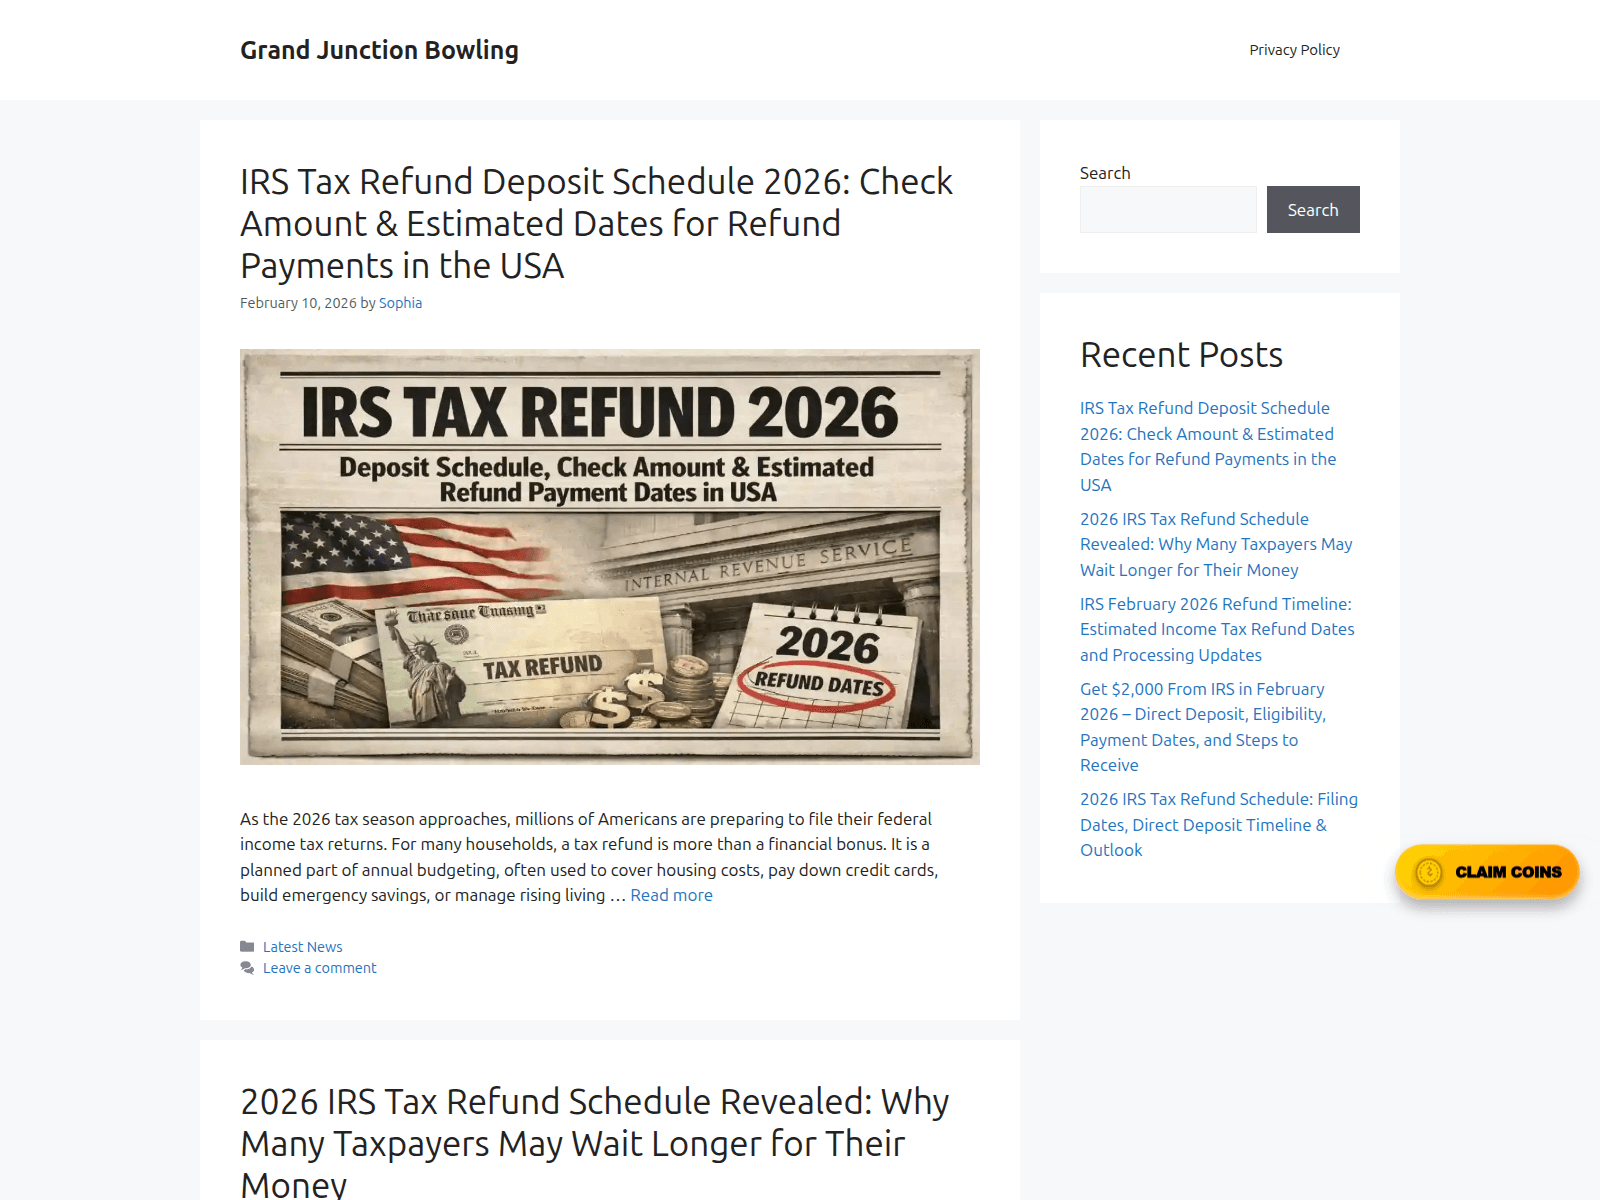 Click the image to view full size
90
Likely scamScam likelihood 90/100
Grand Junction Bowling hosts IRS tax-refund payment claims despite being unrelated to irs.gov. IRS imagery, promises such as 'Get $2,000 From IRS', and an unexplained 'CLAIM COINS' button create a deceptive financial lure with likely phishing or ad-funnel risk.
ImpersonationAnalyzed by ChatGPT 5.6-sol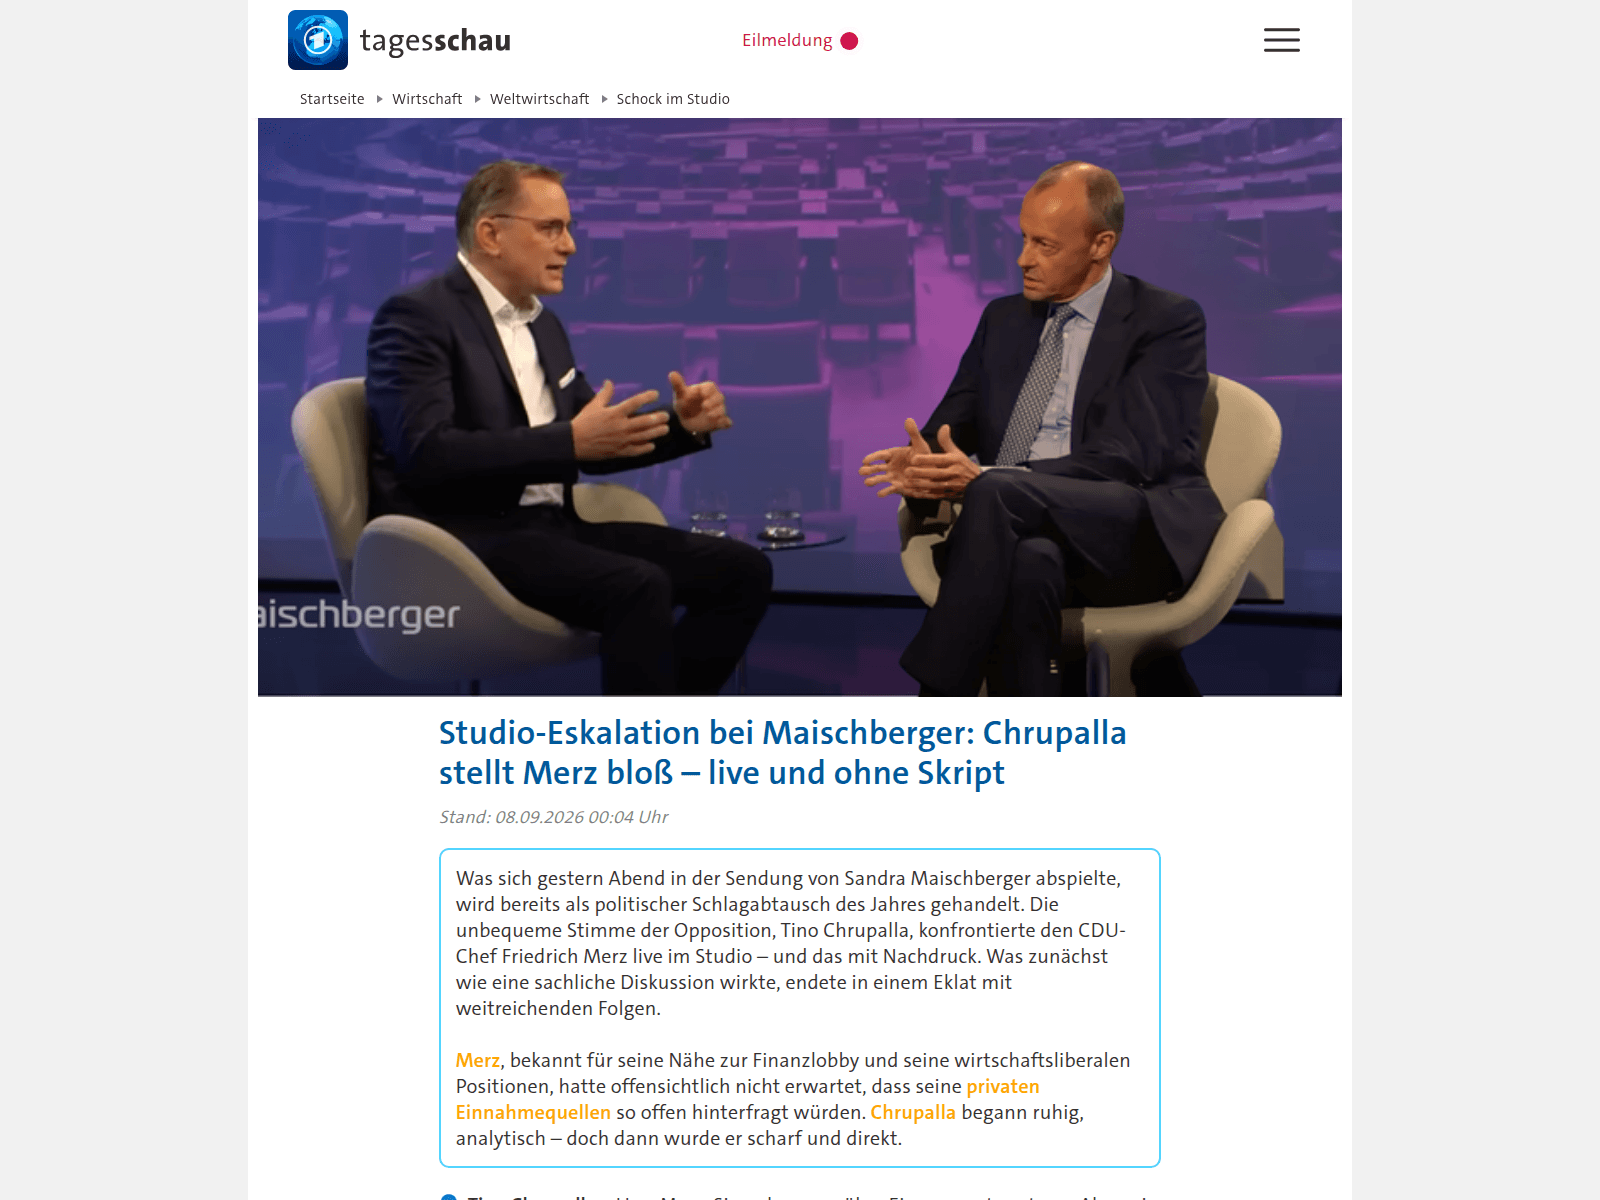 Click the image to view full size
96
Likely scamScam likelihood 96/100
The page copies tagesschau branding and layout, but metadata identifies the unrelated domain perspektive-heute.click rather than tagesschau.de. This explicit domain-brand mismatch, paired with a sensational political article, strongly indicates fabricated-news impersonation.
ImpersonationAnalyzed by ChatGPT 5.6-sol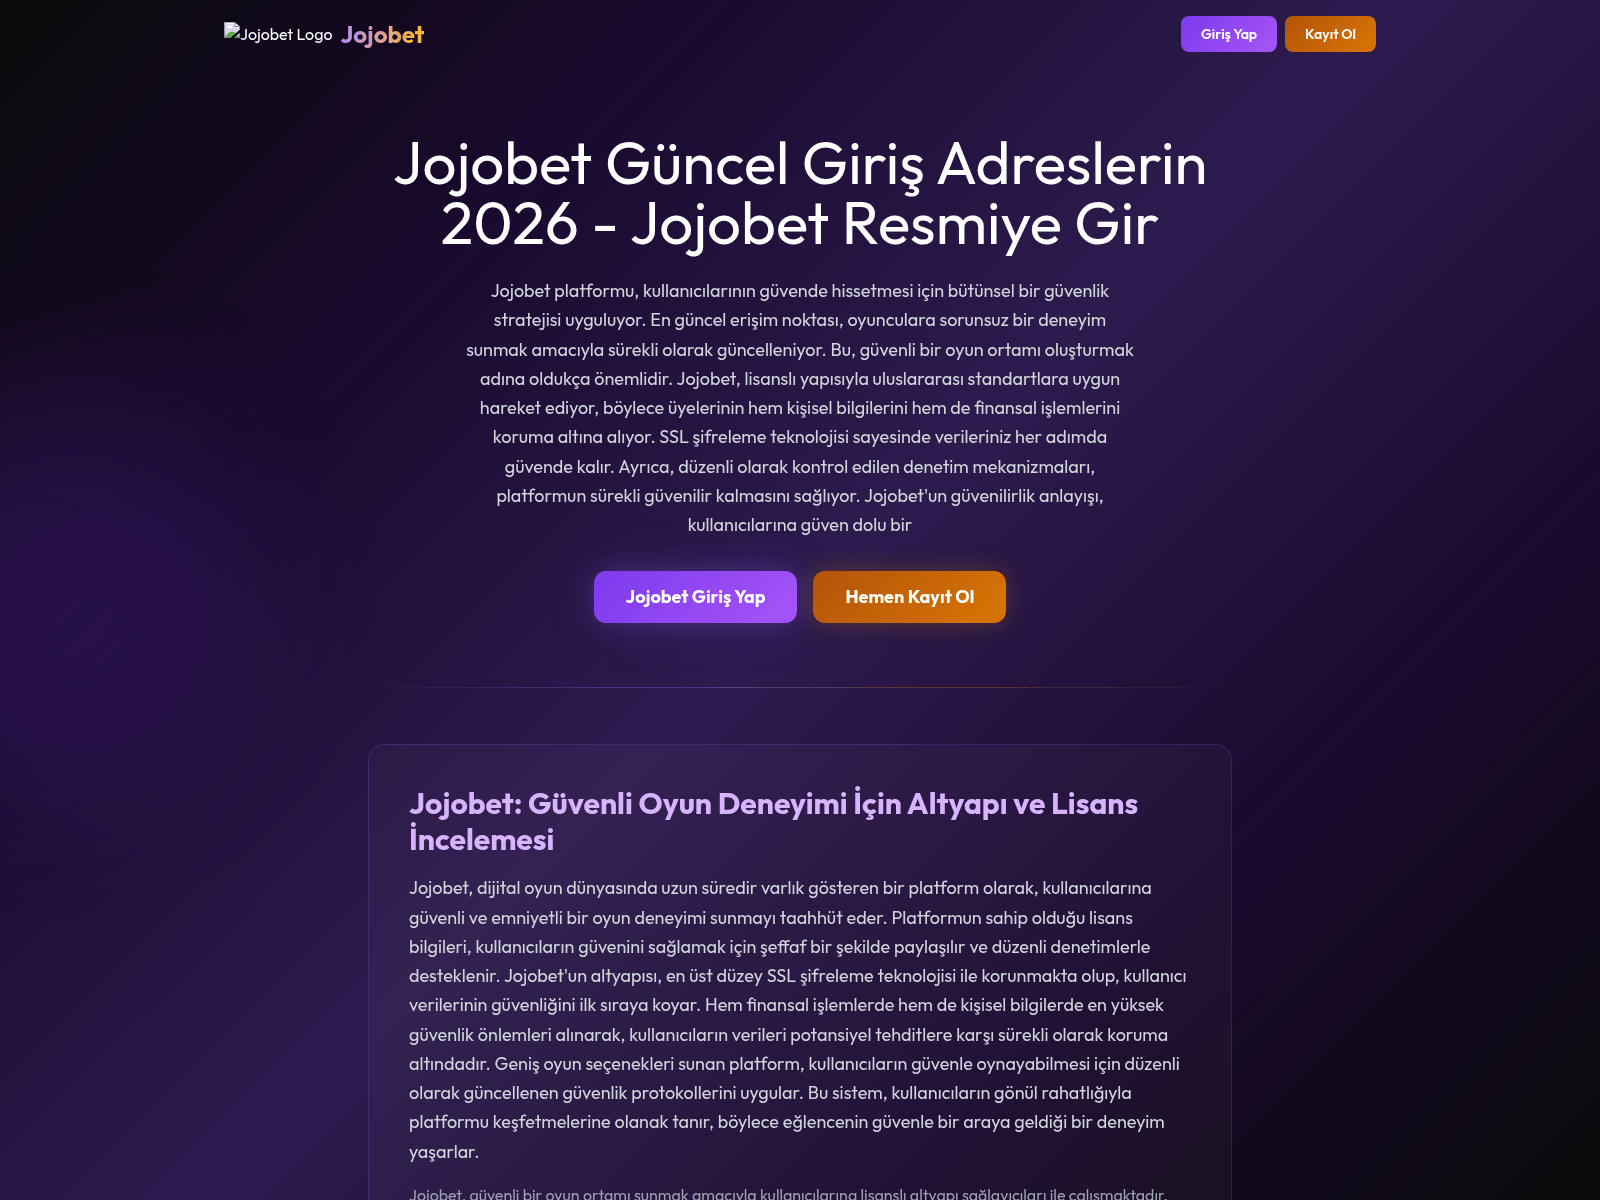 Click the image to view full size
98
Likely scamScam likelihood 98/100
The page presents itself as Jojobet's official 2026 login destination and offers prominent login and signup buttons, but the supplied domain tr.jojobet-giris-adressites.icu is unrelated to the official brand domain, strongly indicating impersonation and credential phishing.
ImpersonationAnalyzed by ChatGPT 5.6-sol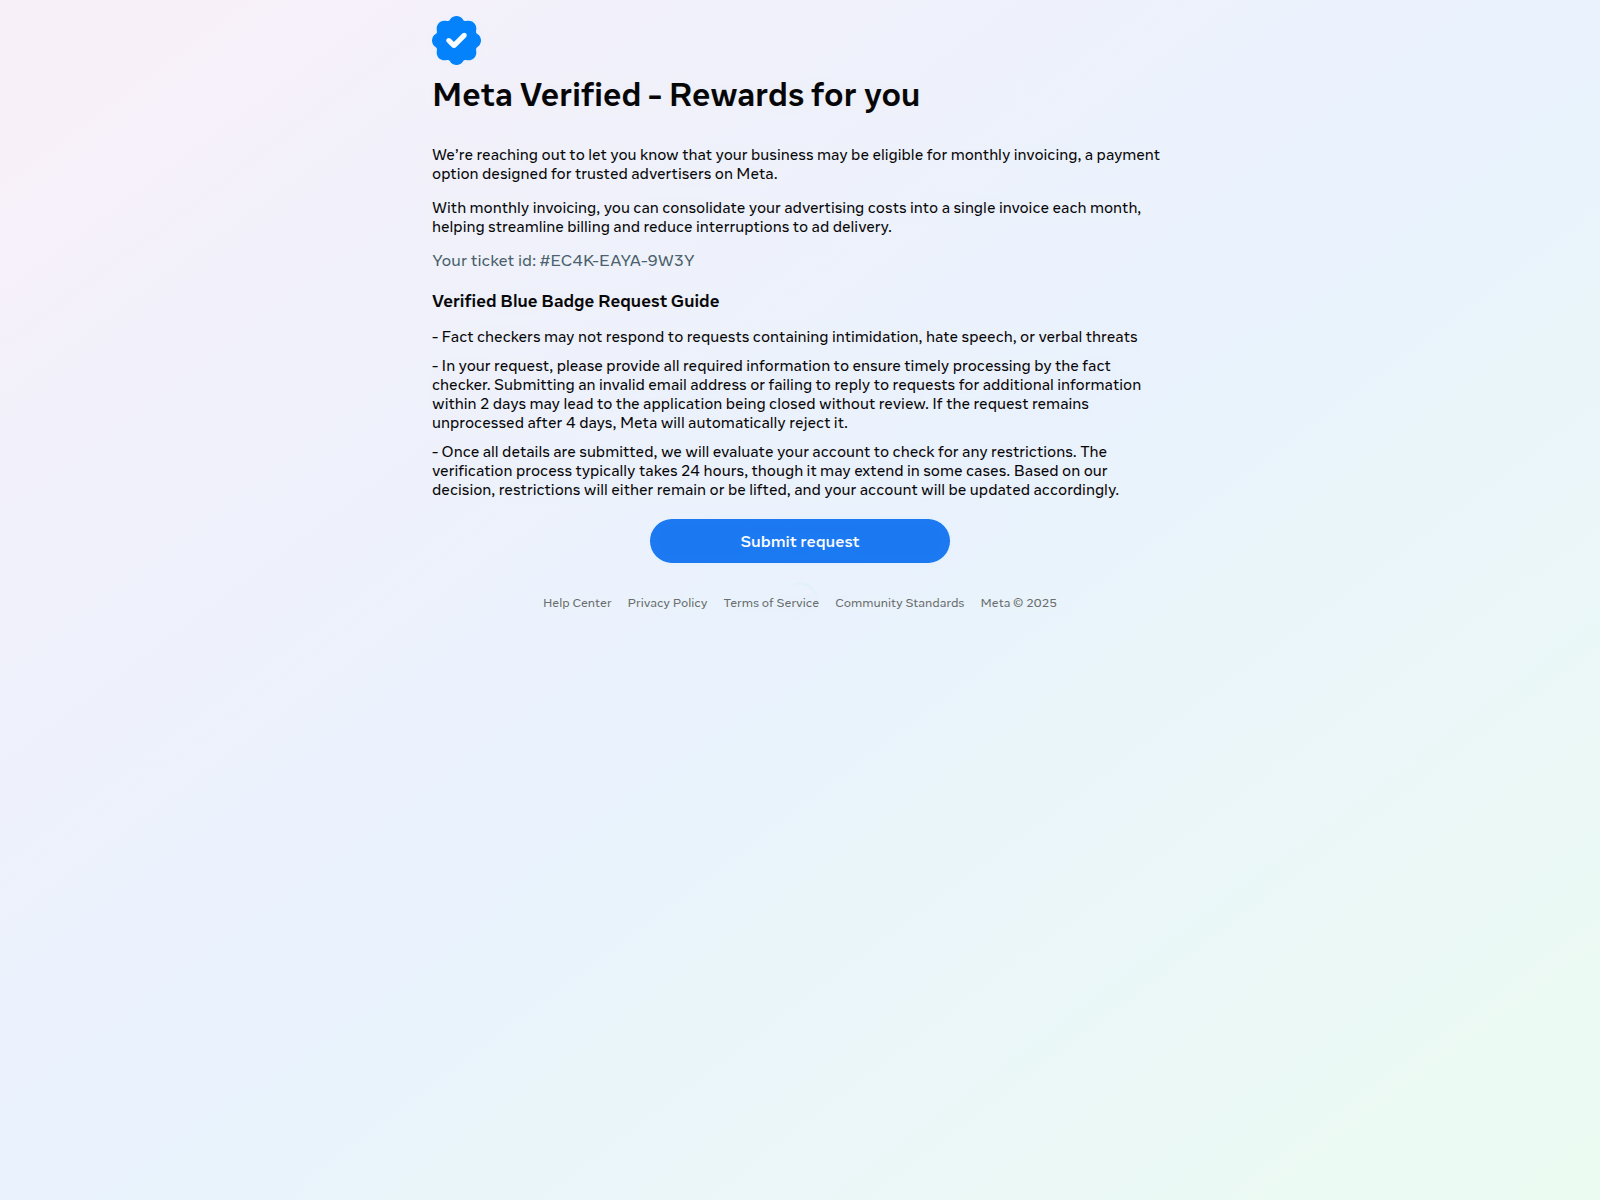 Click the image to view full size
99
Likely scamScam likelihood 99/100
Meta-branded verification and advertiser billing offer urges users to 'Submit request' and provides a ticket ID. The supplied domain, verification-blueticks-fb33.vercel.app, is unrelated to official meta.com infrastructure, indicating Meta impersonation and credential phishing.
ImpersonationAnalyzed by ChatGPT 5.6-sol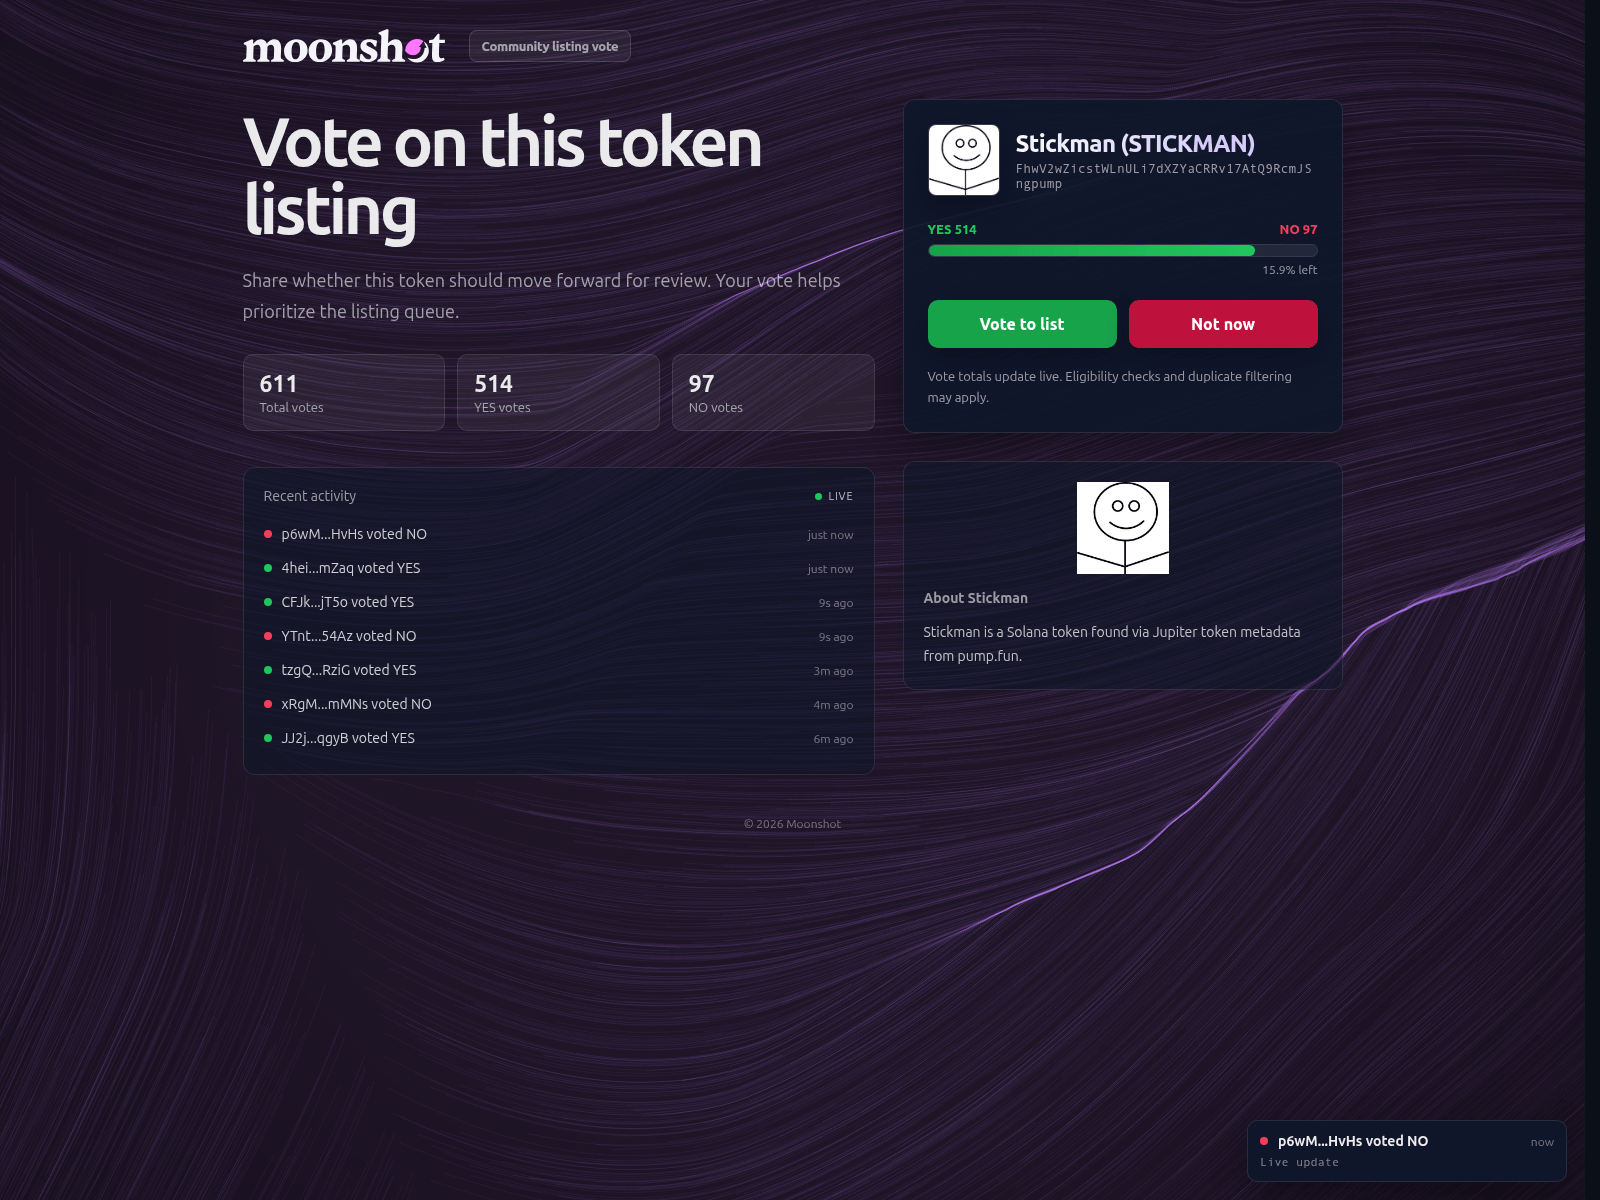 Click the image to view full size
98
Likely scamScam likelihood 98/100
The page uses Moonshot branding and a token-listing vote interface, but the supplied vote-id-0zhwitp.portallogonapp.beer domain does not match official moonshot.cc. This clear brand-domain mismatch strongly indicates a crypto wallet-phishing clone.
ImpersonationAnalyzed by ChatGPT 5.6-sol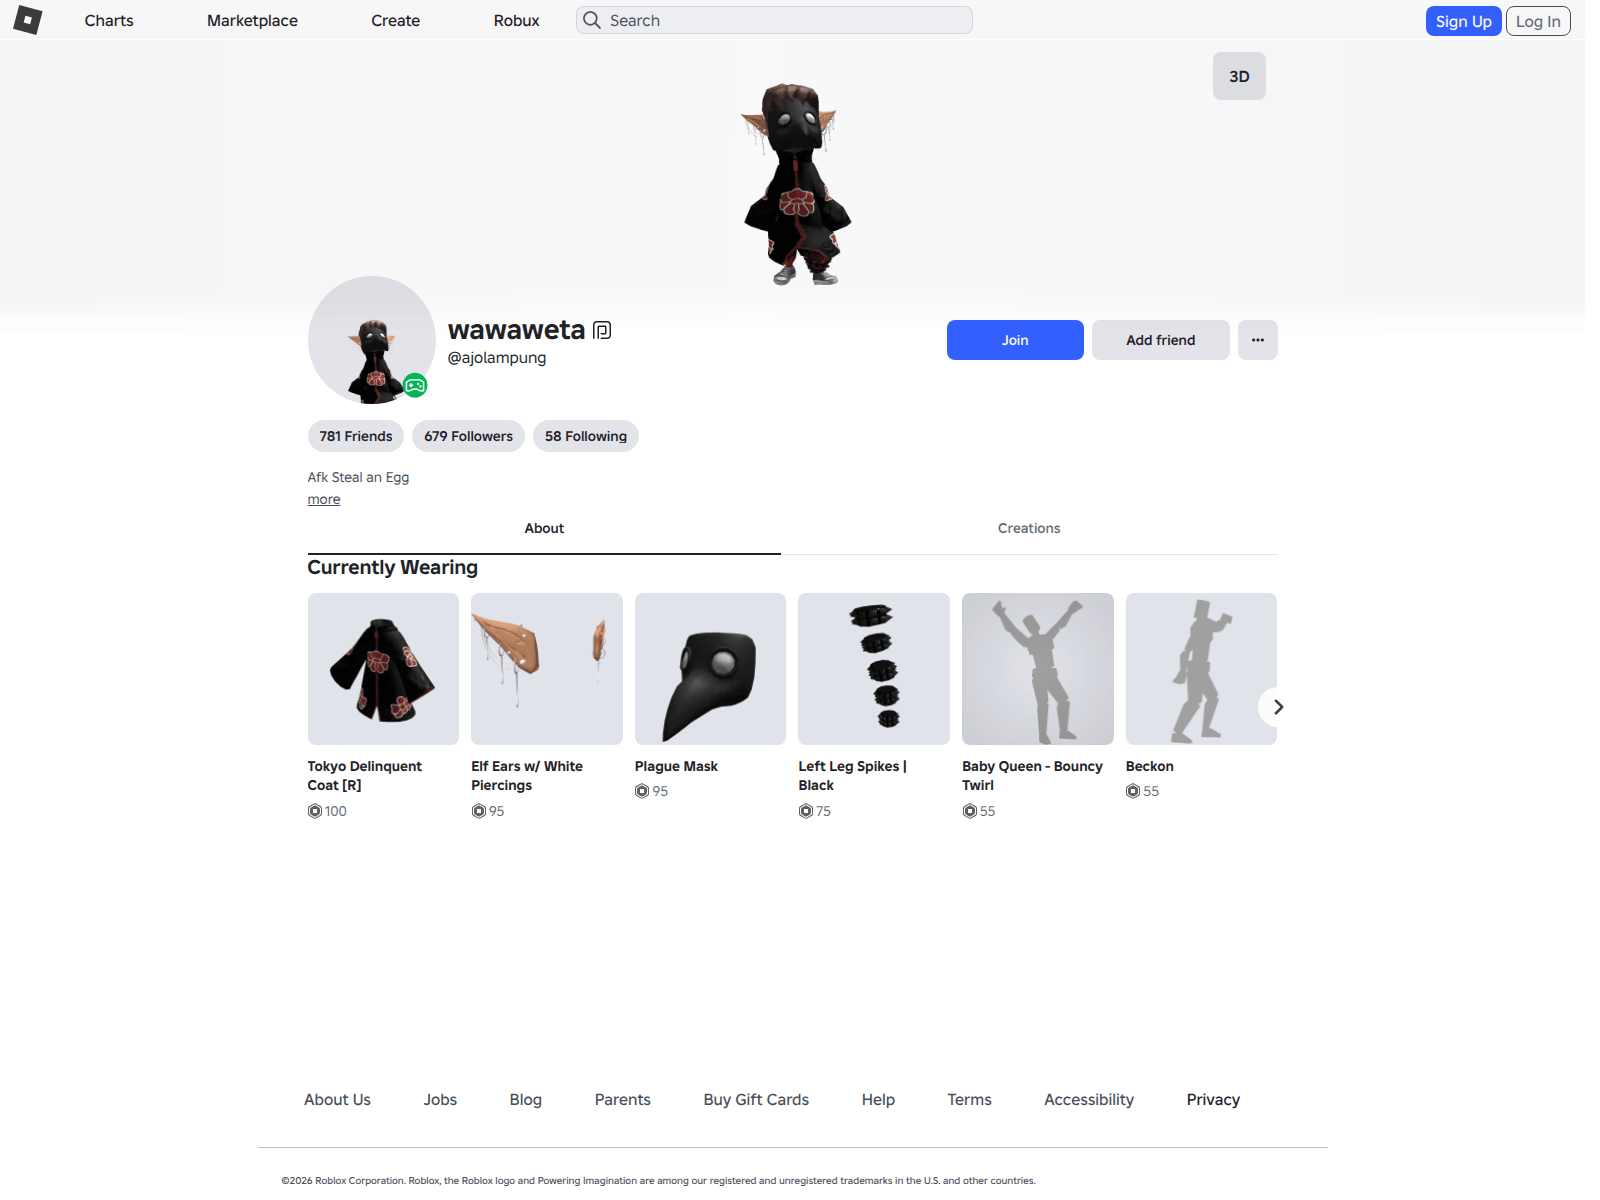 Click the image to view full size
99
Likely scamScam likelihood 99/100
The pixel-perfect Roblox profile page includes Roblox branding and Log In controls, but metadata identifies the host as roblox.com.ml rather than official roblox.com. This lookalike-domain mismatch strongly indicates credential phishing and brand impersonation.
ImpersonationAnalyzed by ChatGPT 5.6-sol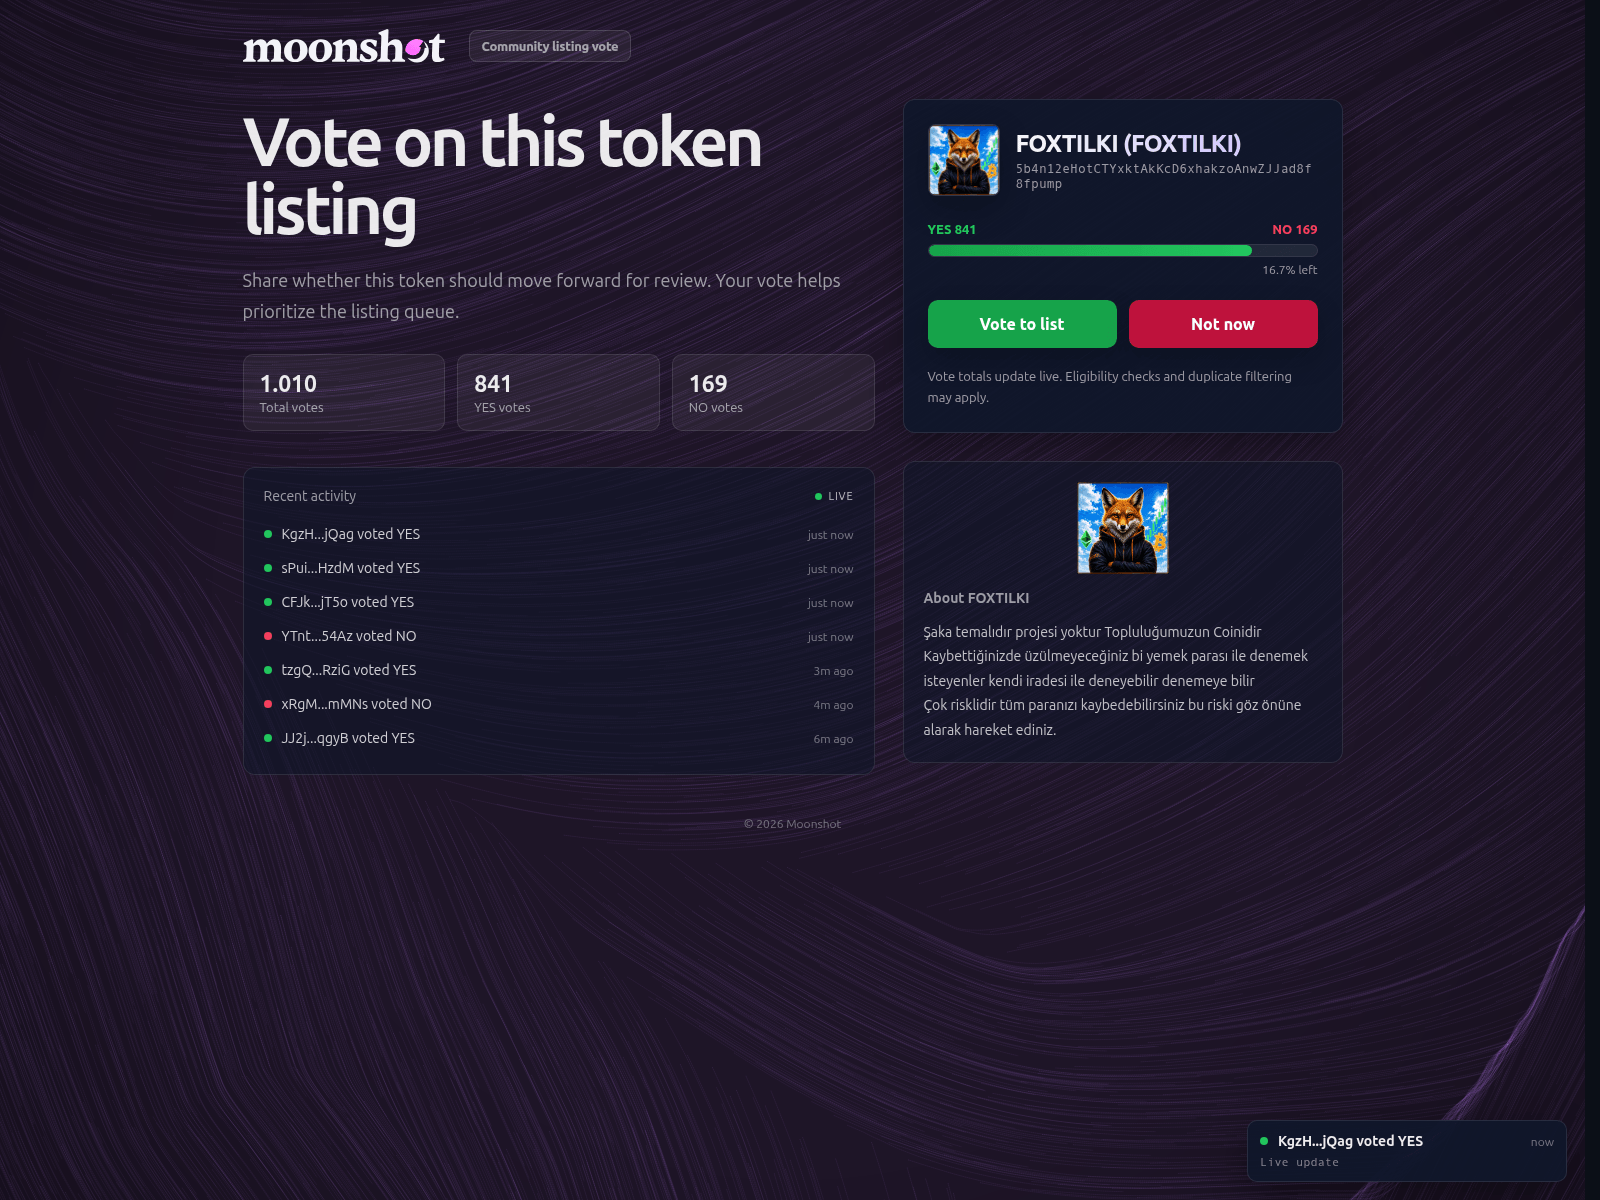 Click the image to view full size
98
Likely scamScam likelihood 98/100
The page copies Moonshot branding and presents a crypto token listing vote, while the supplied domain vote-id-tofvbpr.portallogonapp.cam does not match official moonshot.cc. This brand-domain mismatch and wallet-linked voting lure strongly indicate phishing.
ImpersonationAnalyzed by ChatGPT 5.6-sol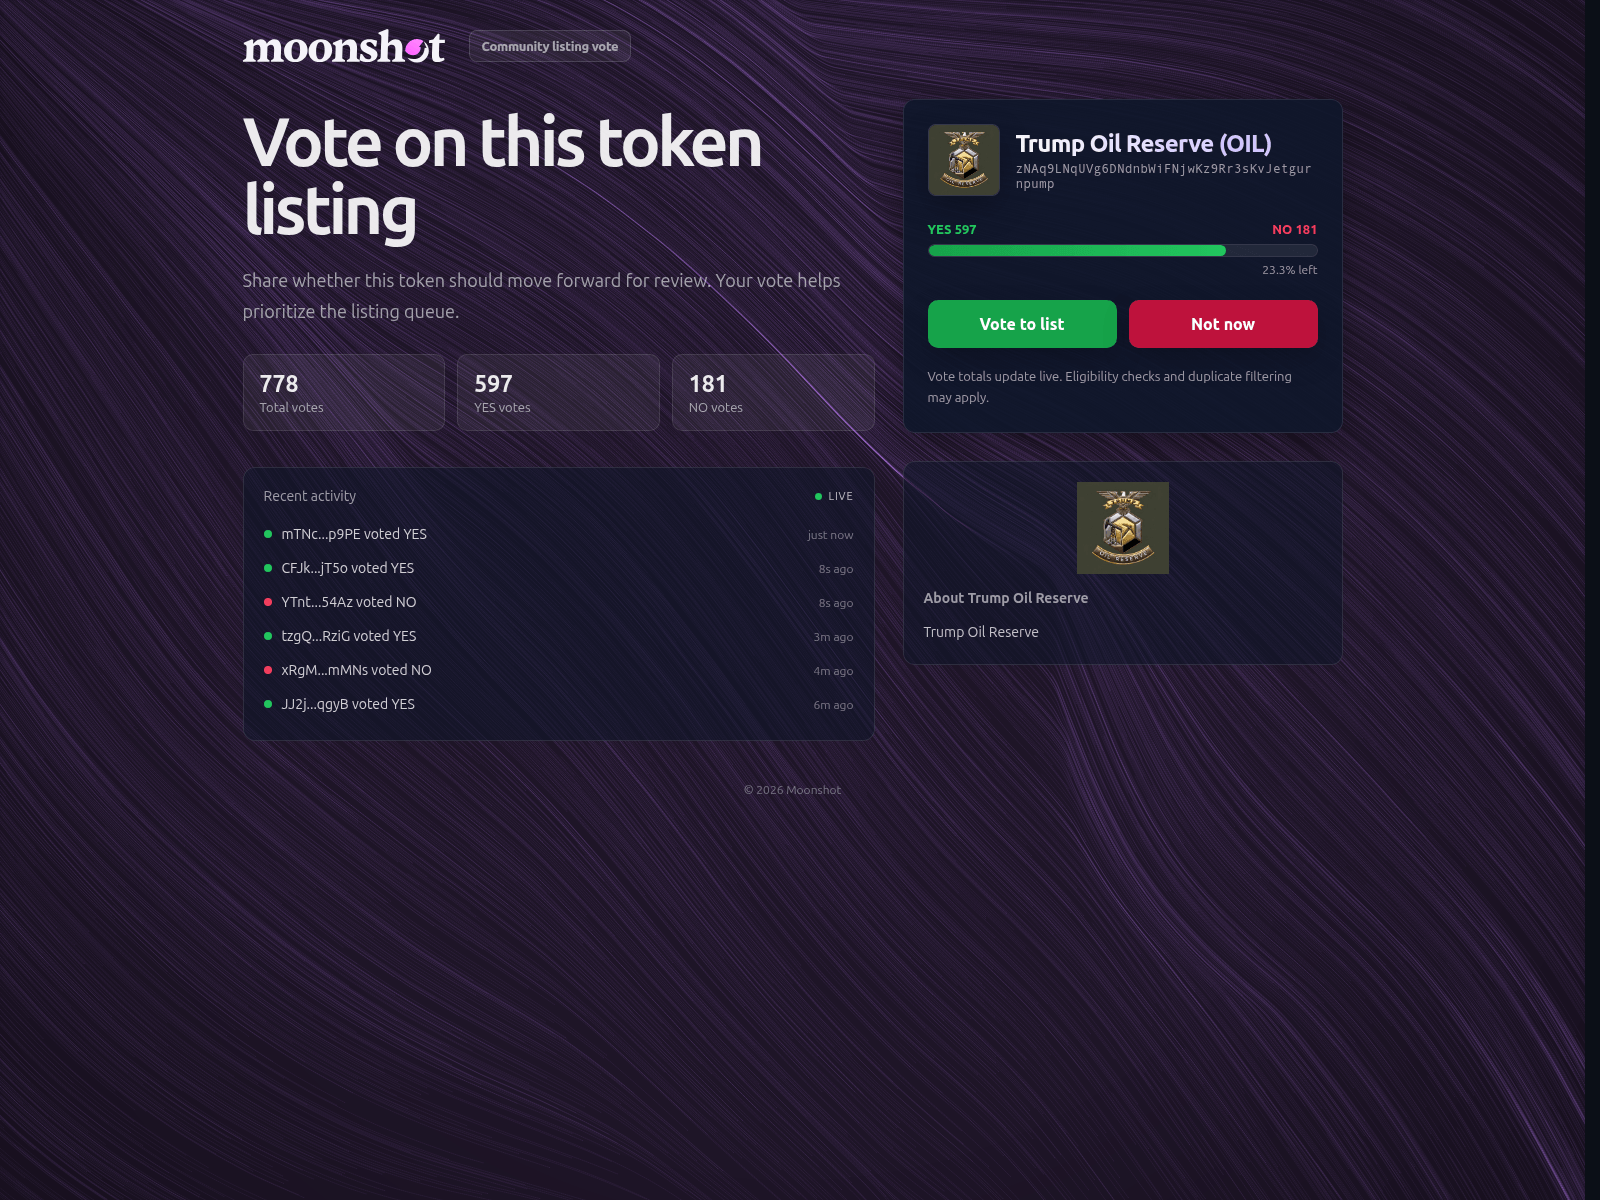 Click the image to view full size
98
Likely scamScam likelihood 98/100
The page uses Moonshot branding and a token-listing vote interface, but the supplied domain vote-id-5tevs6xpu.portallogonapp.surf does not match official moonshot.cc. This clear brand-domain mismatch strongly indicates a crypto wallet-phishing clone.
ImpersonationAnalyzed by ChatGPT 5.6-sol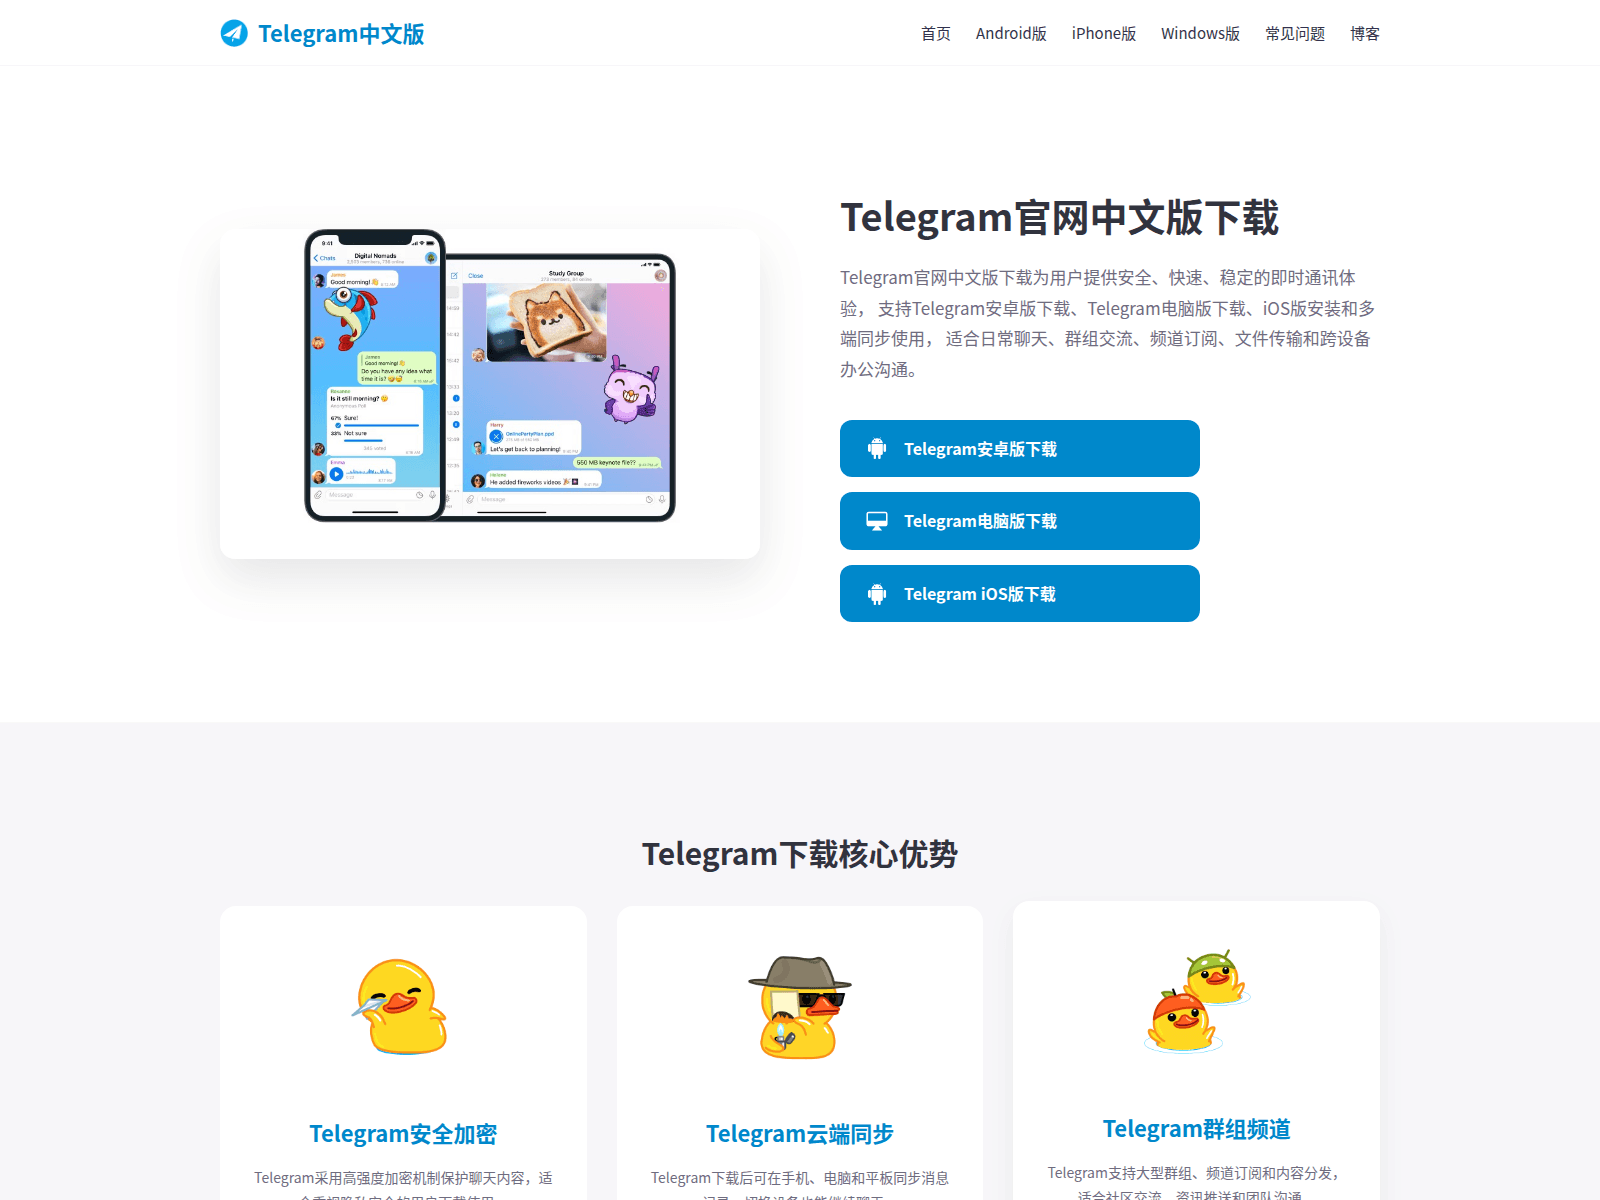 Click the image to view full size
96
Likely scamScam likelihood 96/100
The page uses Telegram's logo and claims 'Telegram官网中文版下载' while offering Android, PC, and iOS installs. The supplied domain telegrampczh.com does not match official telegram.org, indicating brand impersonation and a high-risk third-party download funnel.
ImpersonationAnalyzed by ChatGPT 5.6-sol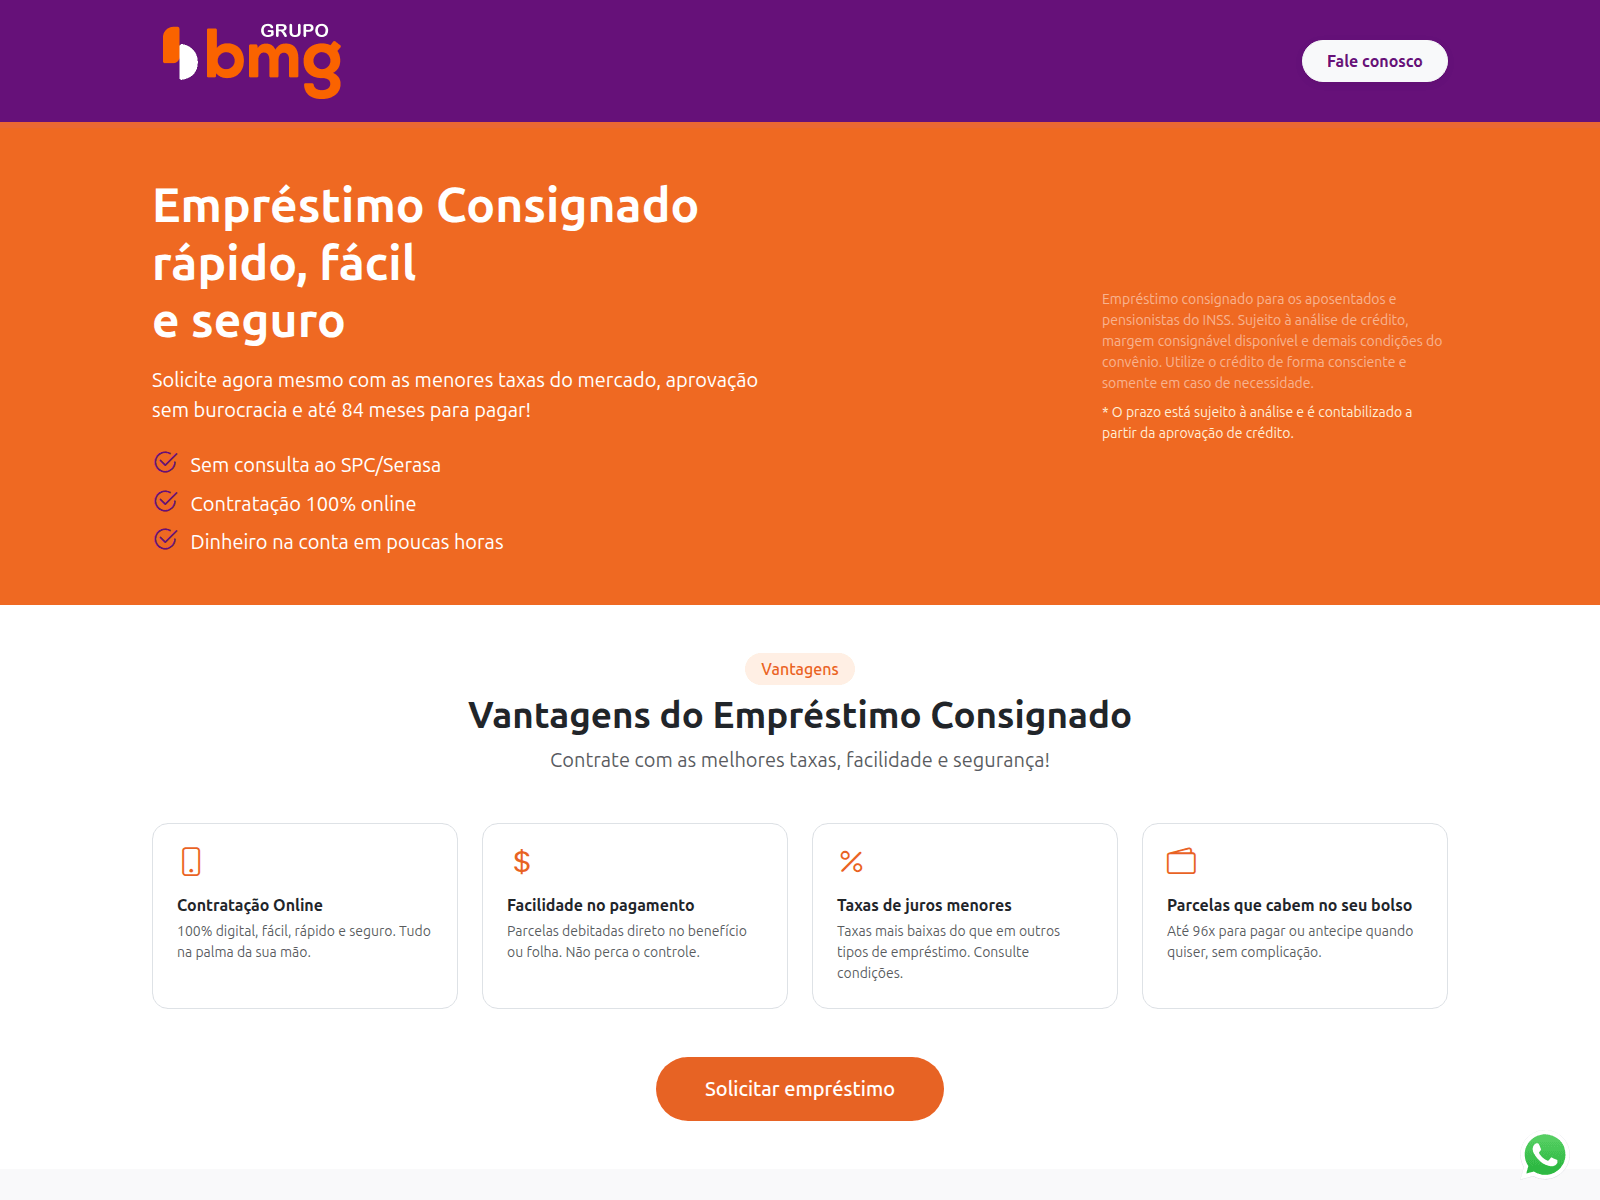 Click the image to view full size
97
Likely scamScam likelihood 97/100
The page uses Grupo BMG branding to solicit INSS payroll loans and directs users to apply or contact via WhatsApp, but it is hosted at popularcredito.site rather than the official bancobmg.com.br domain. This clear brand-domain mismatch strongly indicates impersonation and data harvesting.
ImpersonationAnalyzed by ChatGPT 5.6-sol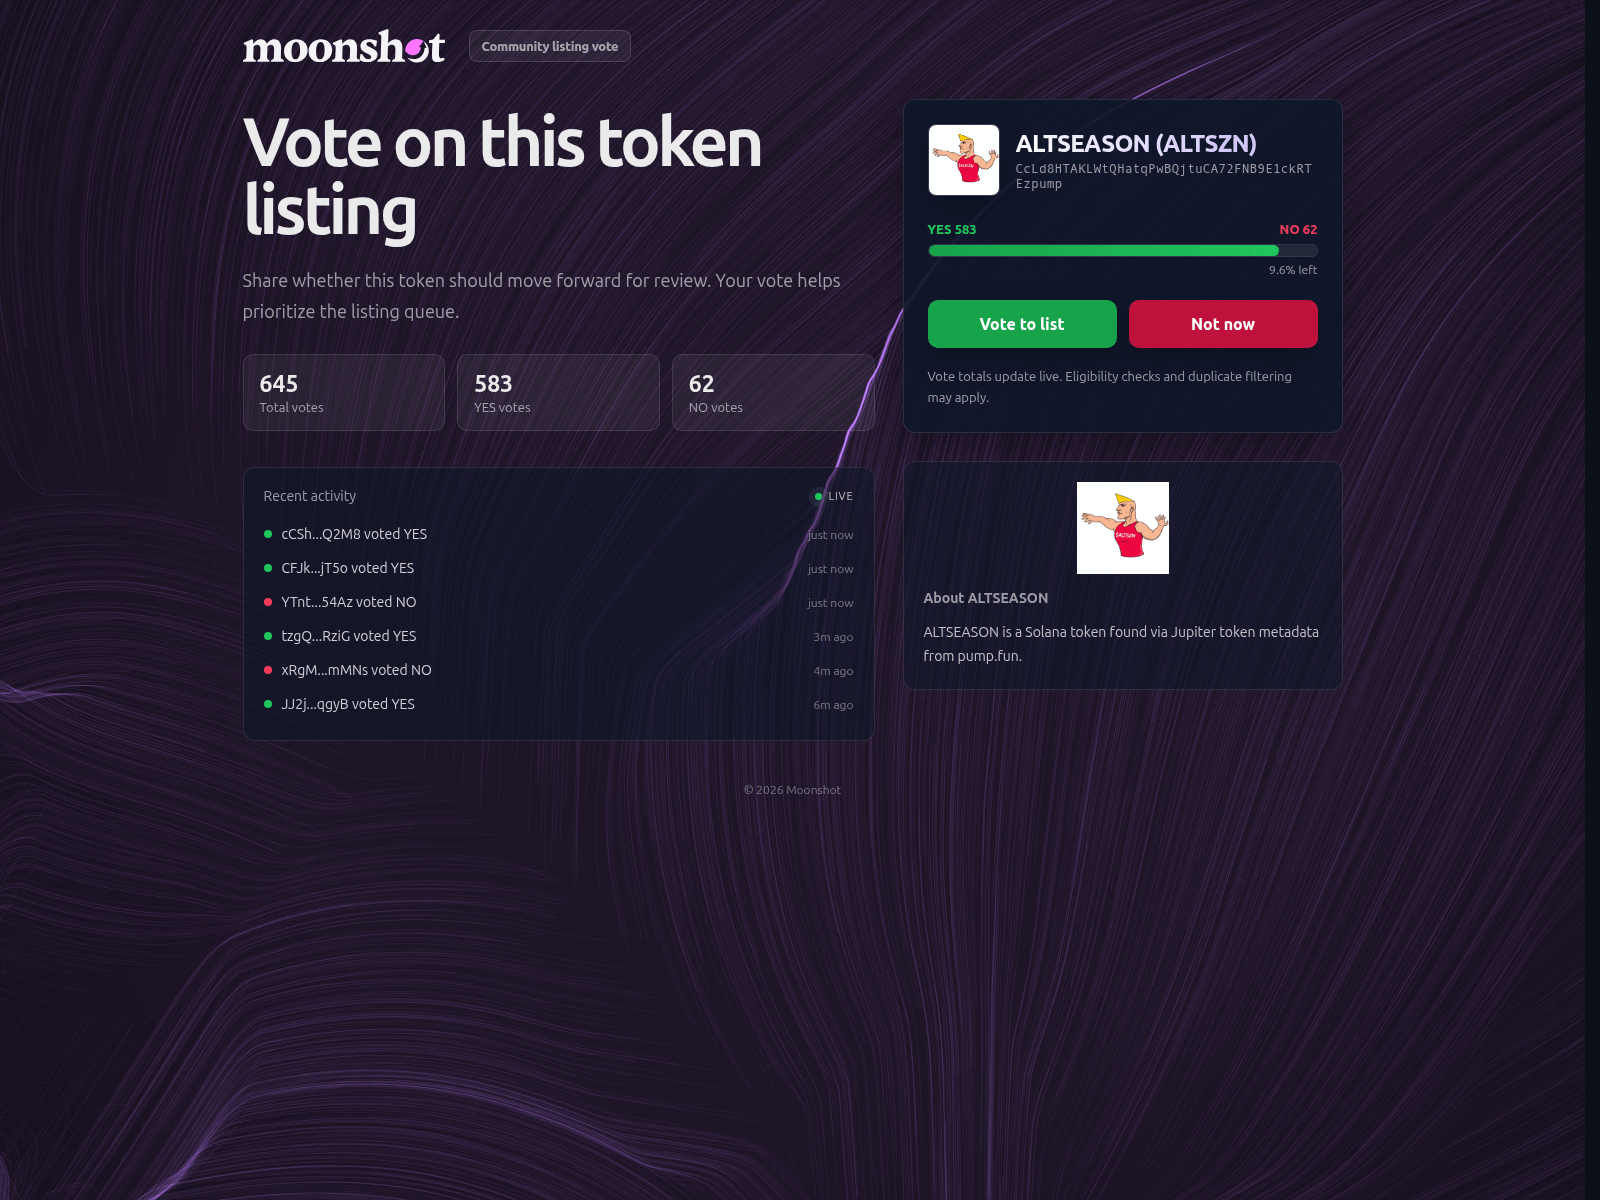 Click the image to view full size
98
Likely scamScam likelihood 98/100
The page uses Moonshot branding and a token-voting prompt, but metadata identifies the unrelated domain vote-id-oodjv6evv.portallogonapp.skin rather than moonshot.cc. This direct brand-domain mismatch strongly indicates a crypto wallet-phishing clone.
ImpersonationAnalyzed by ChatGPT 5.6-sol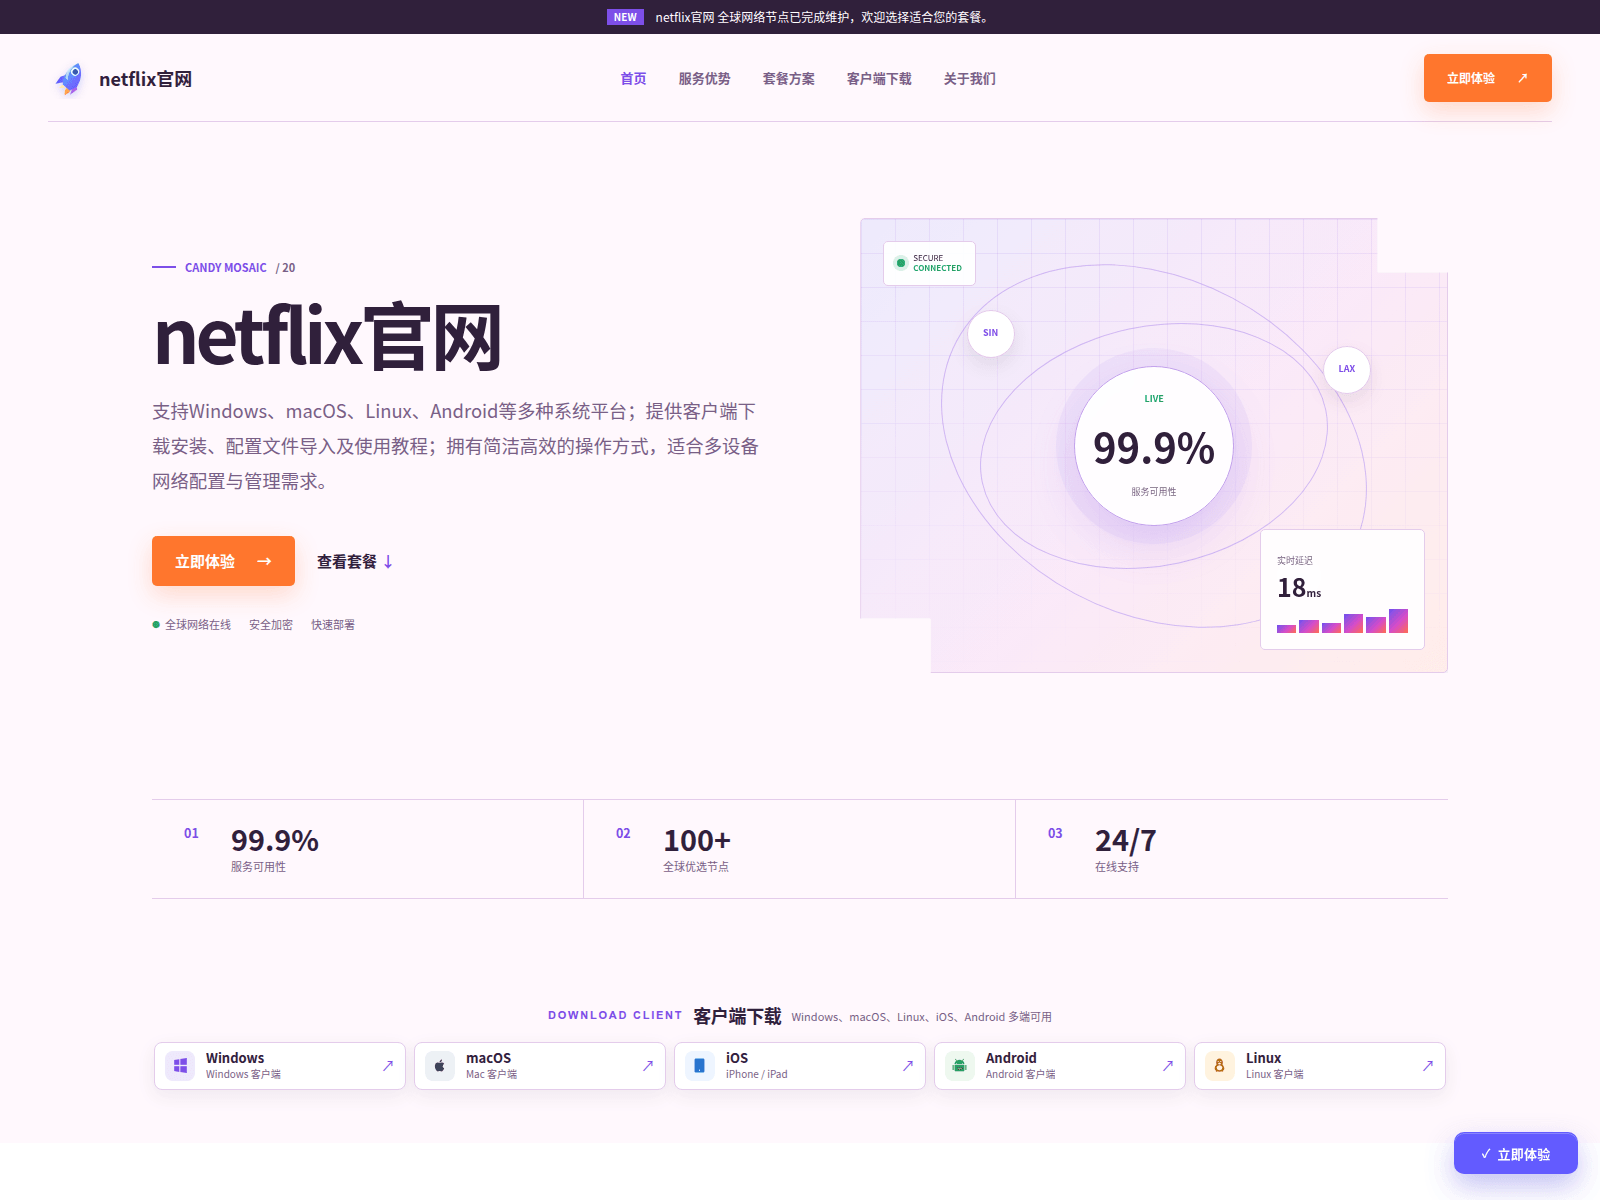 Click the image to view full size
98
Likely scamScam likelihood 98/100
The page labels itself 'netflix官网' and offers VPN client downloads across multiple platforms. The supplied domain netflixvpn.click is unrelated to Netflix's official netflix.com domain, indicating brand impersonation designed to funnel users into potentially malicious software installs.
ImpersonationAnalyzed by ChatGPT 5.6-sol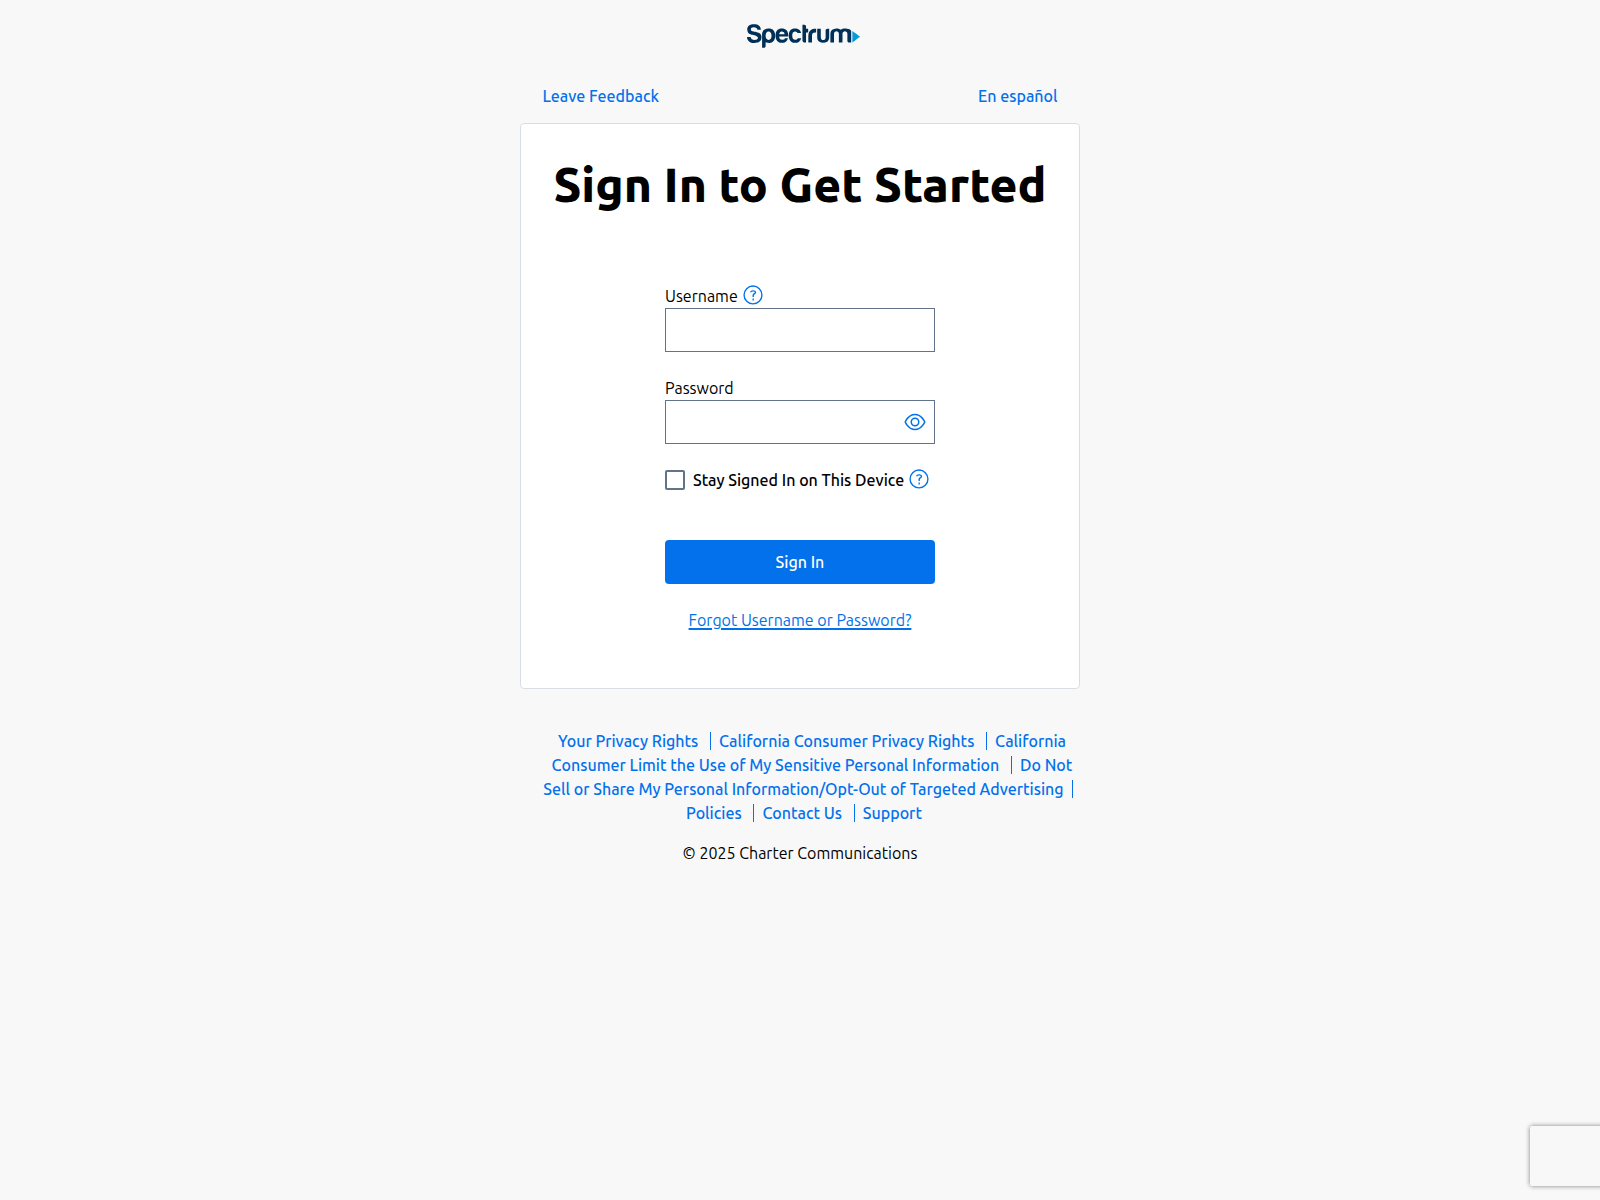 Click the image to view full size
99
Likely scamScam likelihood 99/100
The page uses Spectrum branding and Charter copyright text while requesting a username and password. Metadata identifies the host as stoffinovacion.com rather than Spectrum's official spectrum.net domain, confirming brand impersonation and credential phishing.
ImpersonationAnalyzed by ChatGPT 5.6-sol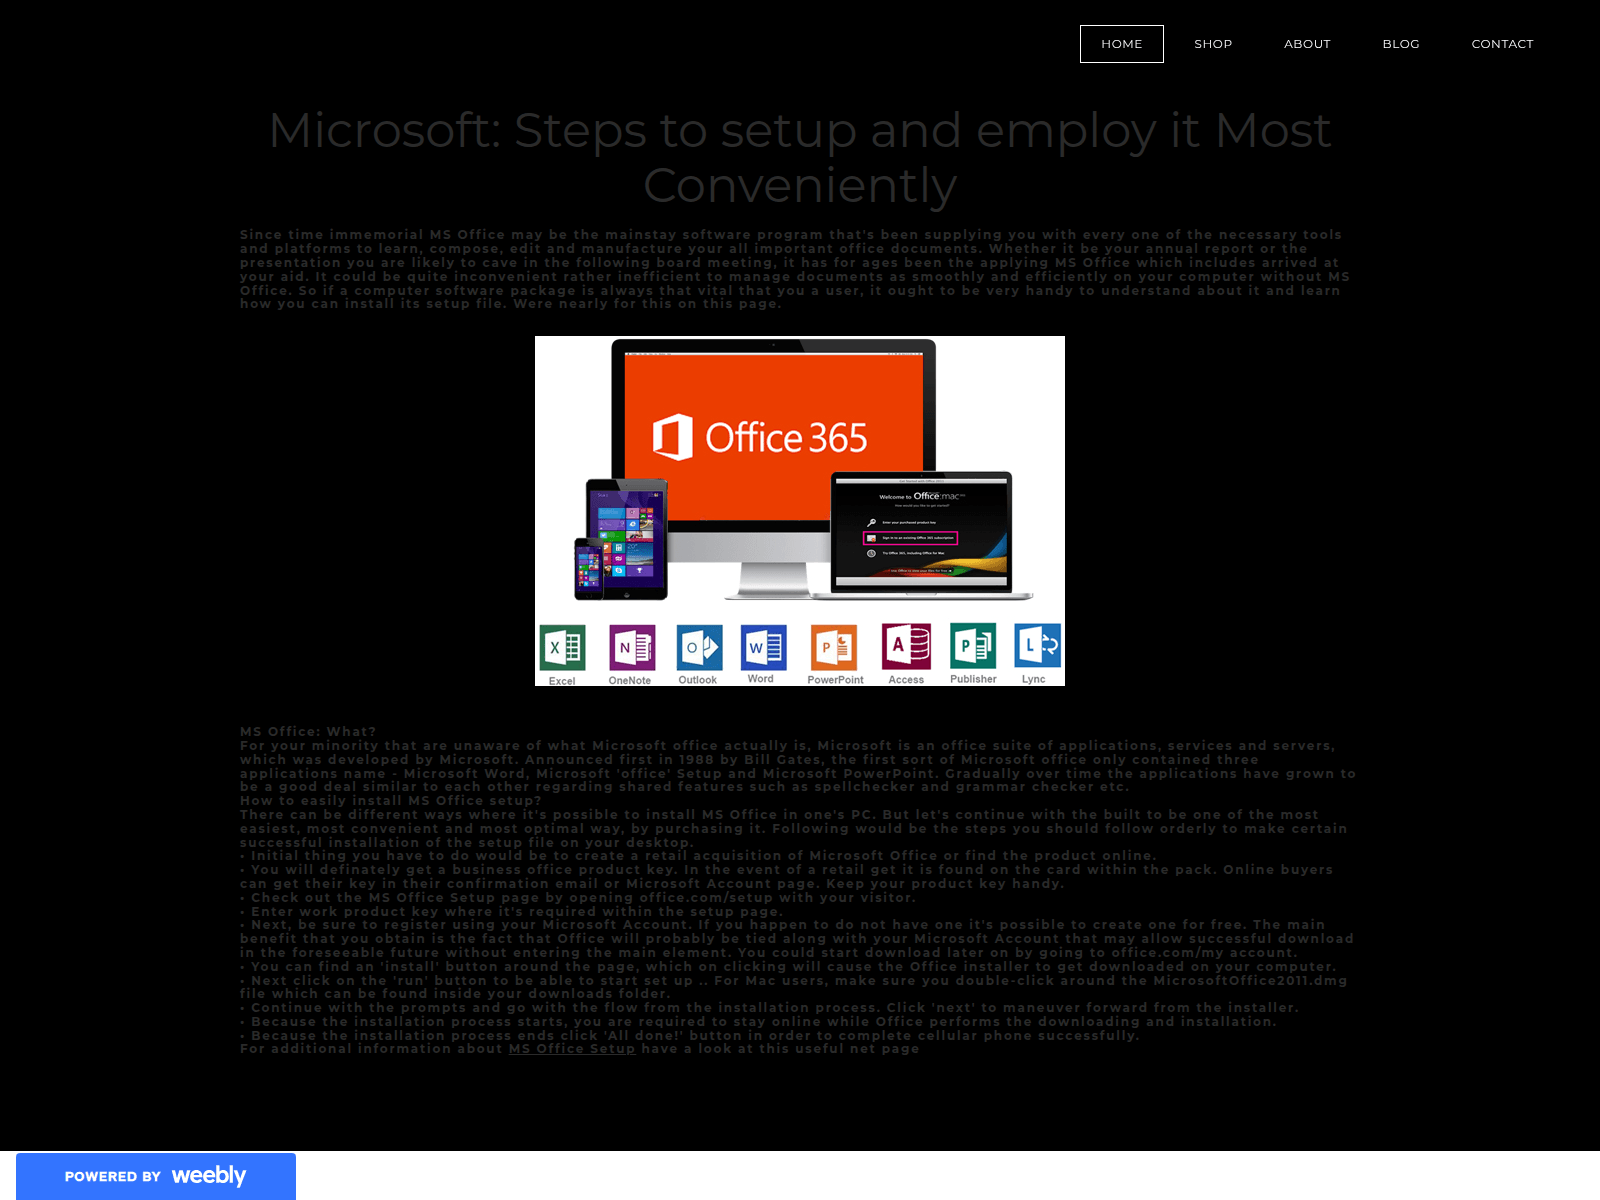 Click the image to view full size
92
Likely scamScam likelihood 92/100
Unofficial levisnoeks.weebly.com page uses Microsoft Office 365 branding and setup instructions to promote an installer. The Weebly domain is unrelated to Microsoft, creating a deceptive software-download lure with substantial malware risk.
ImpersonationAnalyzed by ChatGPT 5.6-sol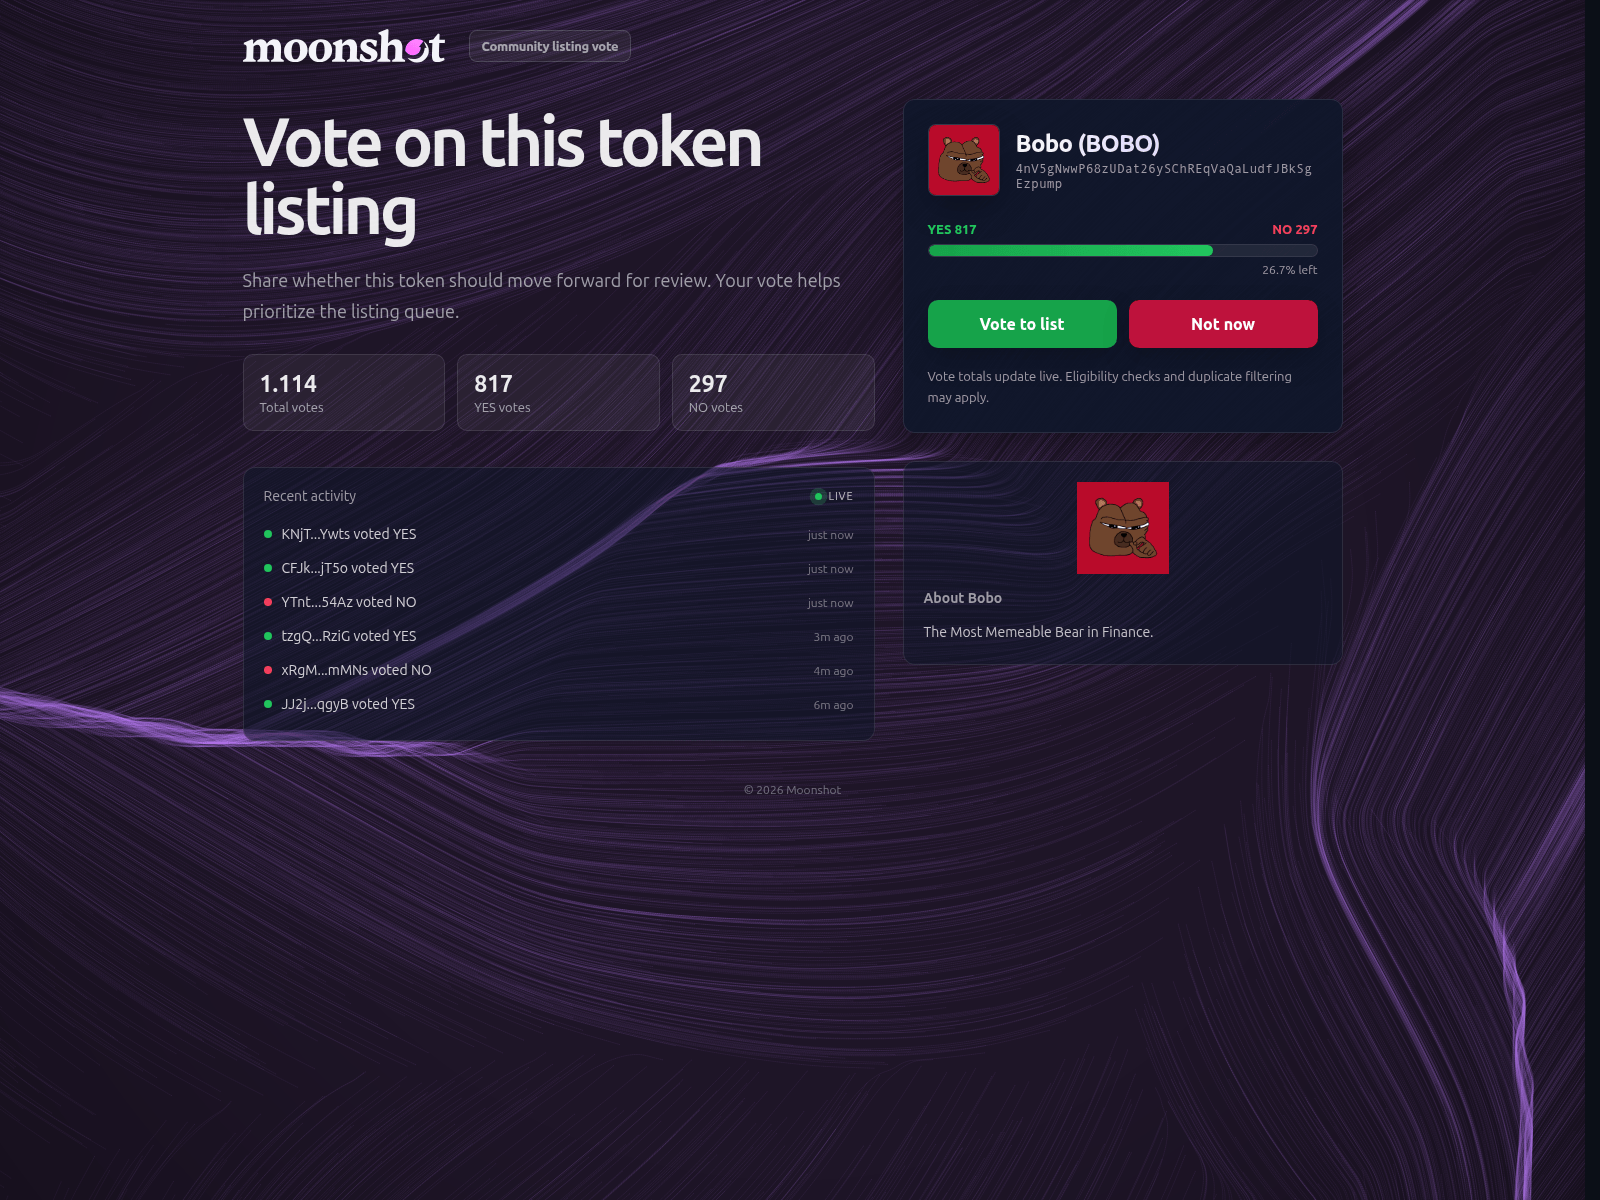 Click the image to view full size
98
Likely scamScam likelihood 98/100
The page uses Moonshot branding and a token-voting interface, but metadata identifies the unrelated portallogonapp.casa domain rather than moonshot.cc. The 'Vote to list' action and simulated live votes support a crypto wallet-phishing clone.
ImpersonationAnalyzed by ChatGPT 5.6-sol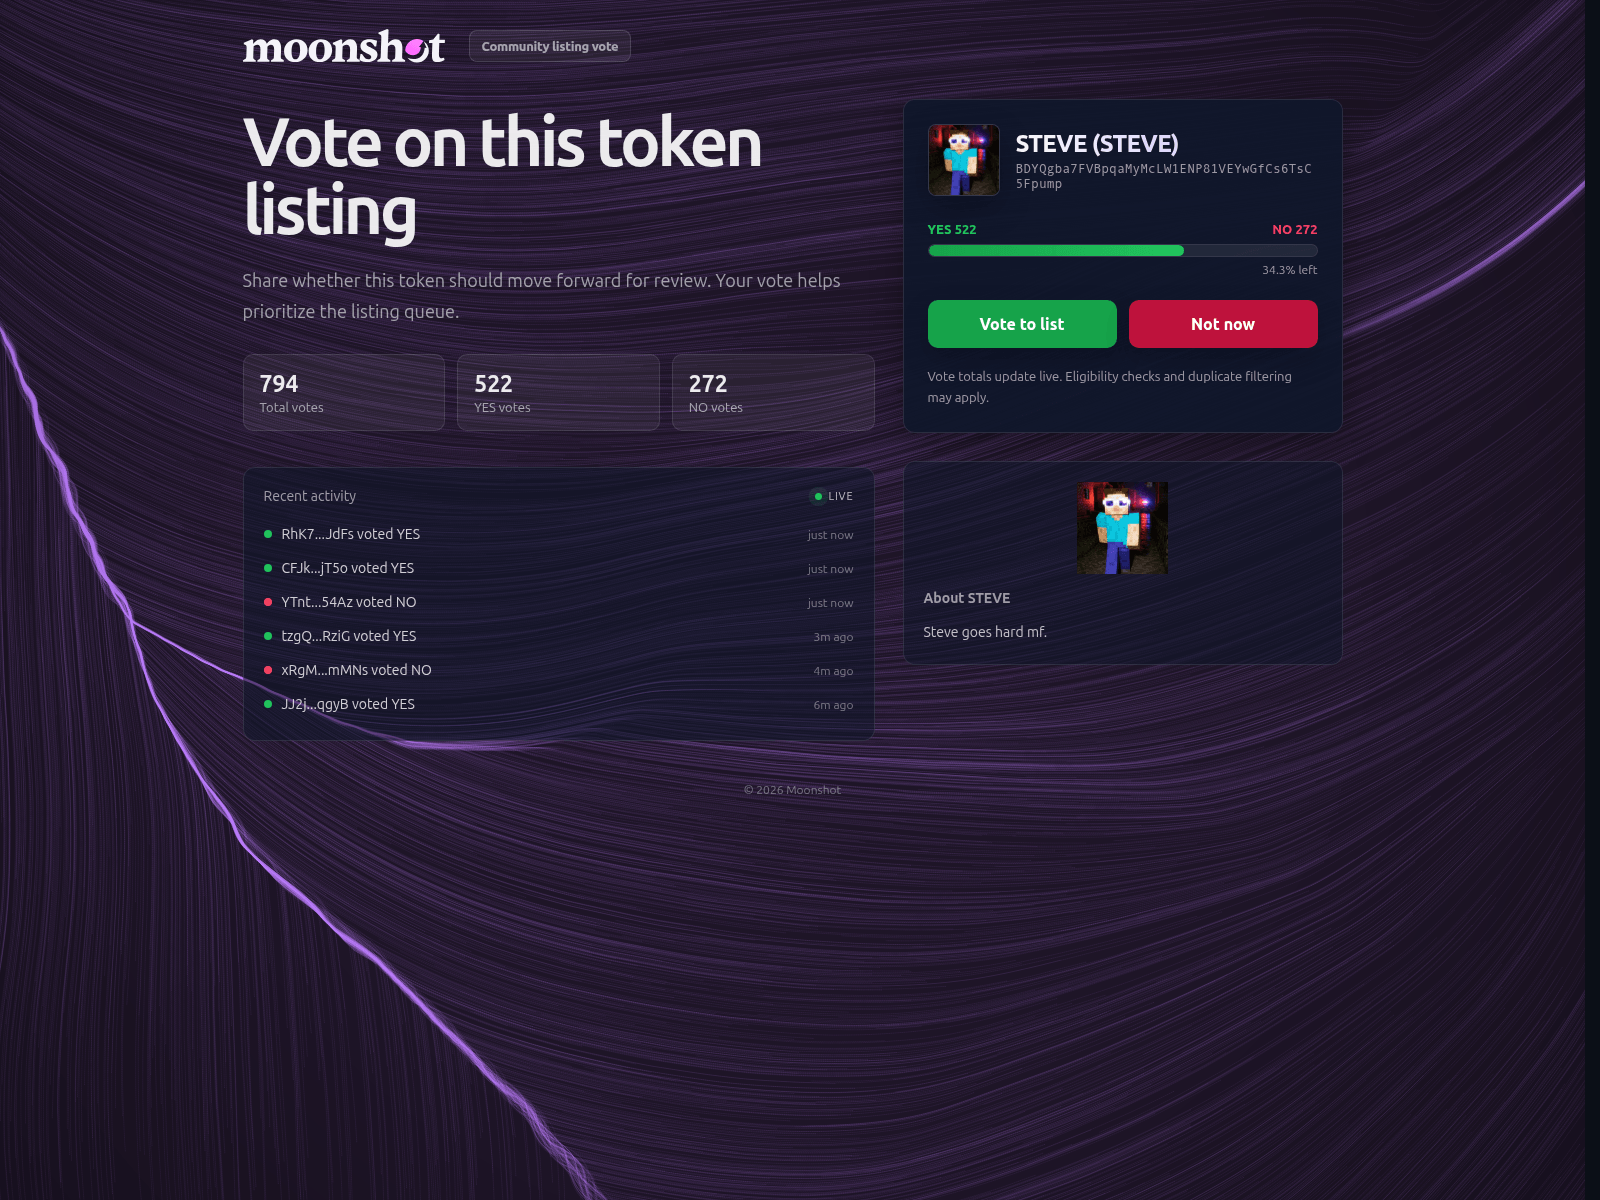 Click the image to view full size
98
Likely scamScam likelihood 98/100
The page copies Moonshot branding and presents a STEVE token listing vote, but it is hosted on vote-id-atq4hwbem.portallogonapp.quest rather than moonshot.cc. This clear brand-domain mismatch strongly indicates a crypto wallet-phishing clone.
ImpersonationAnalyzed by ChatGPT 5.6-sol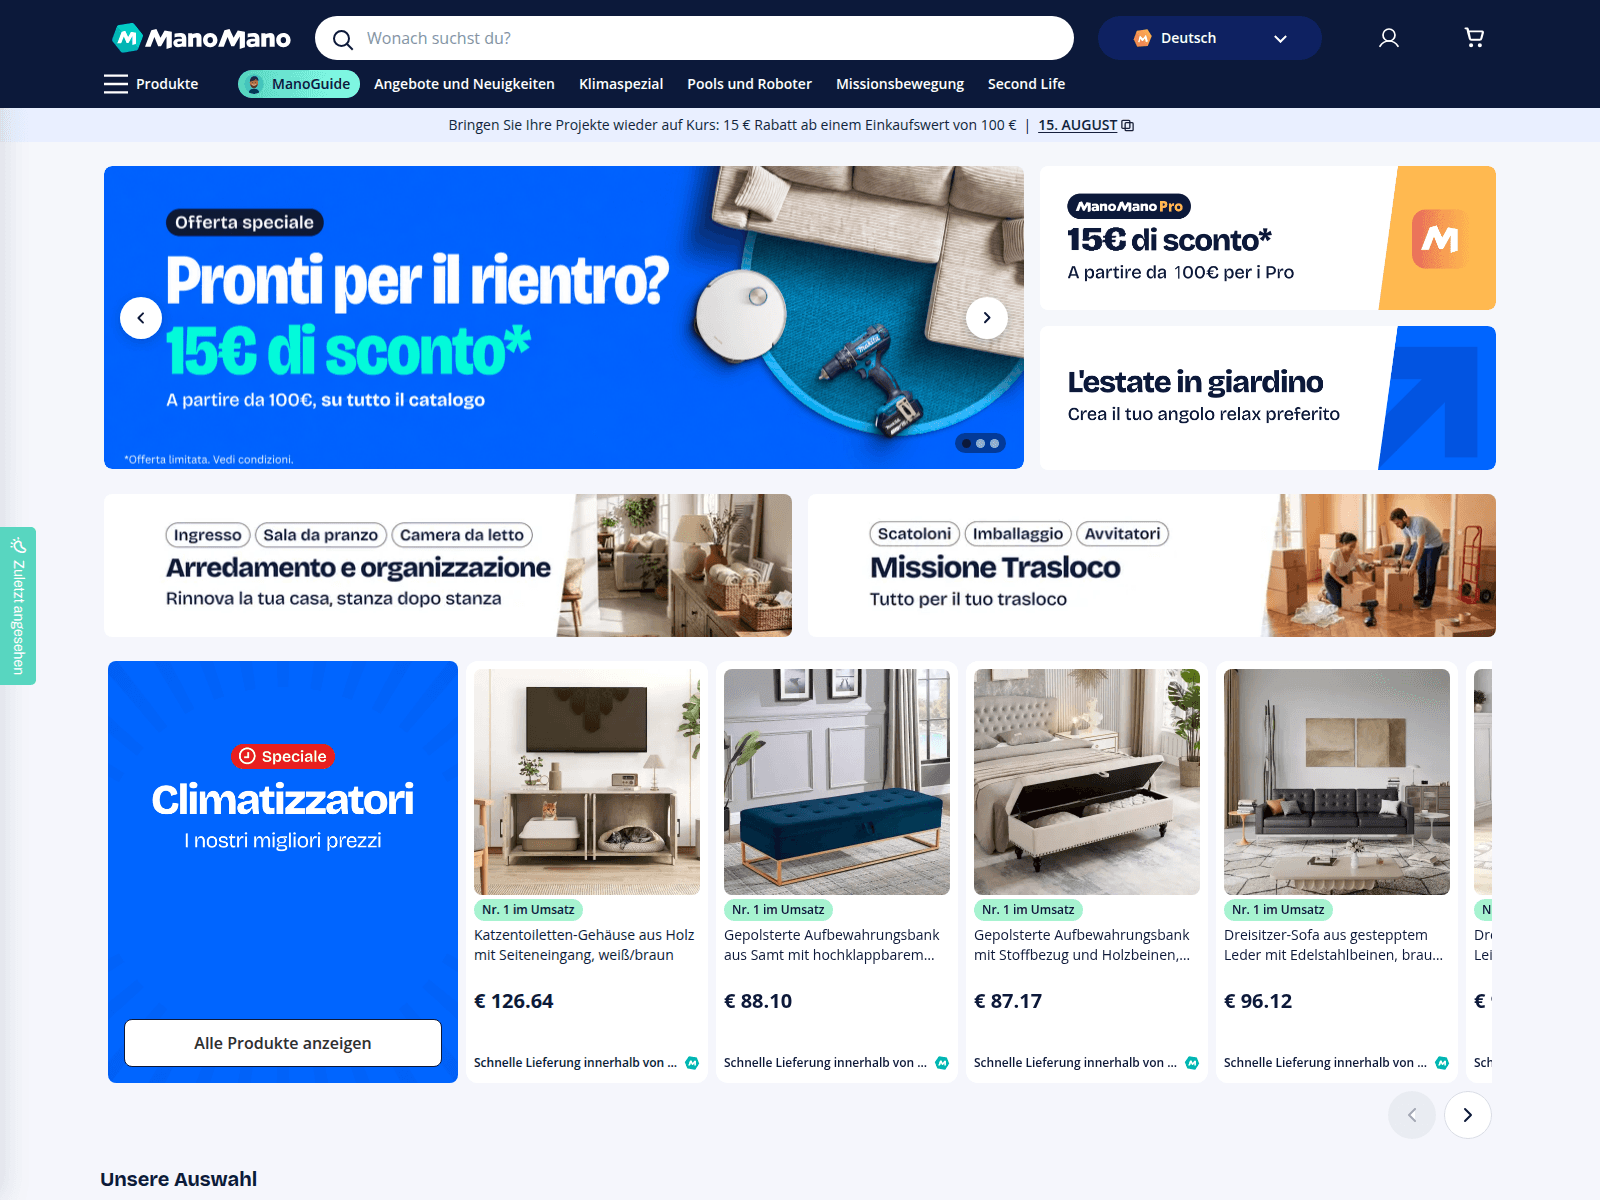 Click the image to view full size
98
Likely scamScam likelihood 98/100
The site uses ManoMano branding, navigation, promotions, product listings, prices and cart functionality on mobilipiacere.com rather than an official ManoMano domain. This clear brand-domain mismatch indicates an impersonating counterfeit storefront.
ImpersonationAnalyzed by ChatGPT 5.6-sol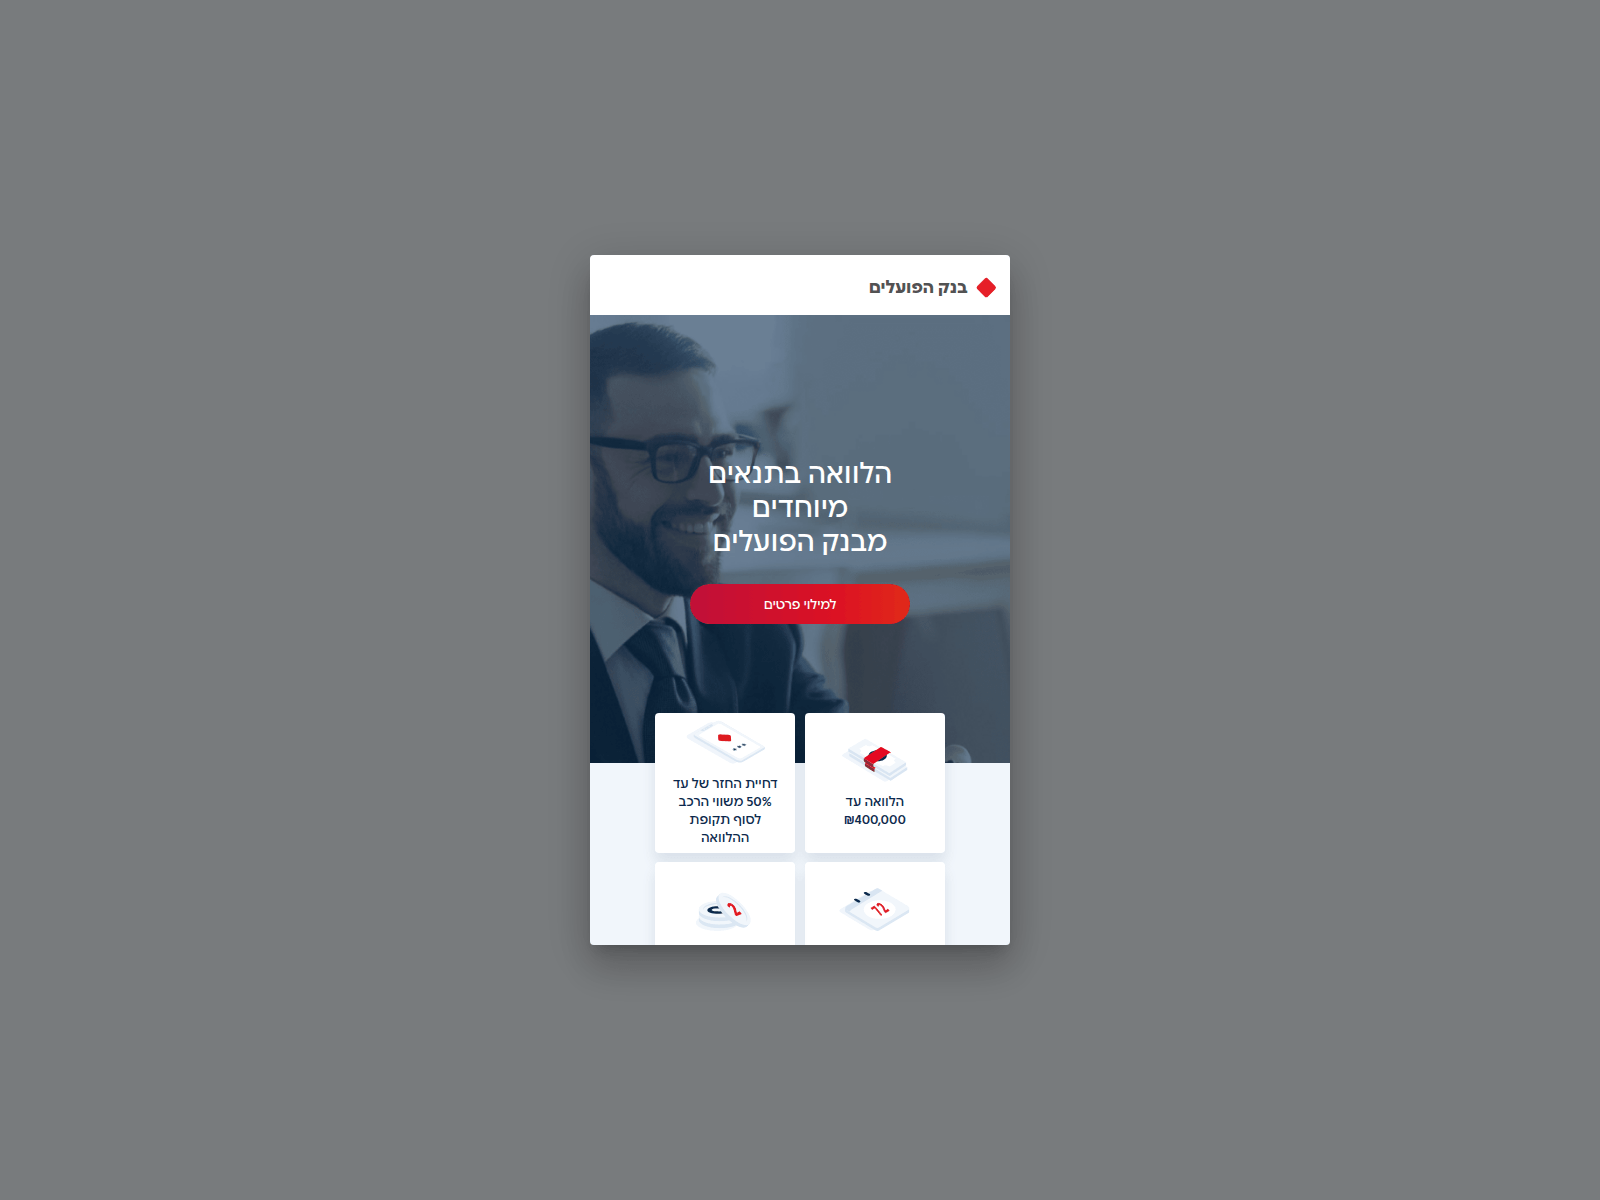 Click the image to view full size
98
Likely scamScam likelihood 98/100
The page uses Bank Hapoalim's Hebrew name and logo to promote loans up to ₪400,000 and solicit details, while the supplied domain bank-hapoalim.open-finance.ai does not match the bank's official domain. This is a clear bank-impersonation phishing lure.
ImpersonationAnalyzed by ChatGPT 5.6-sol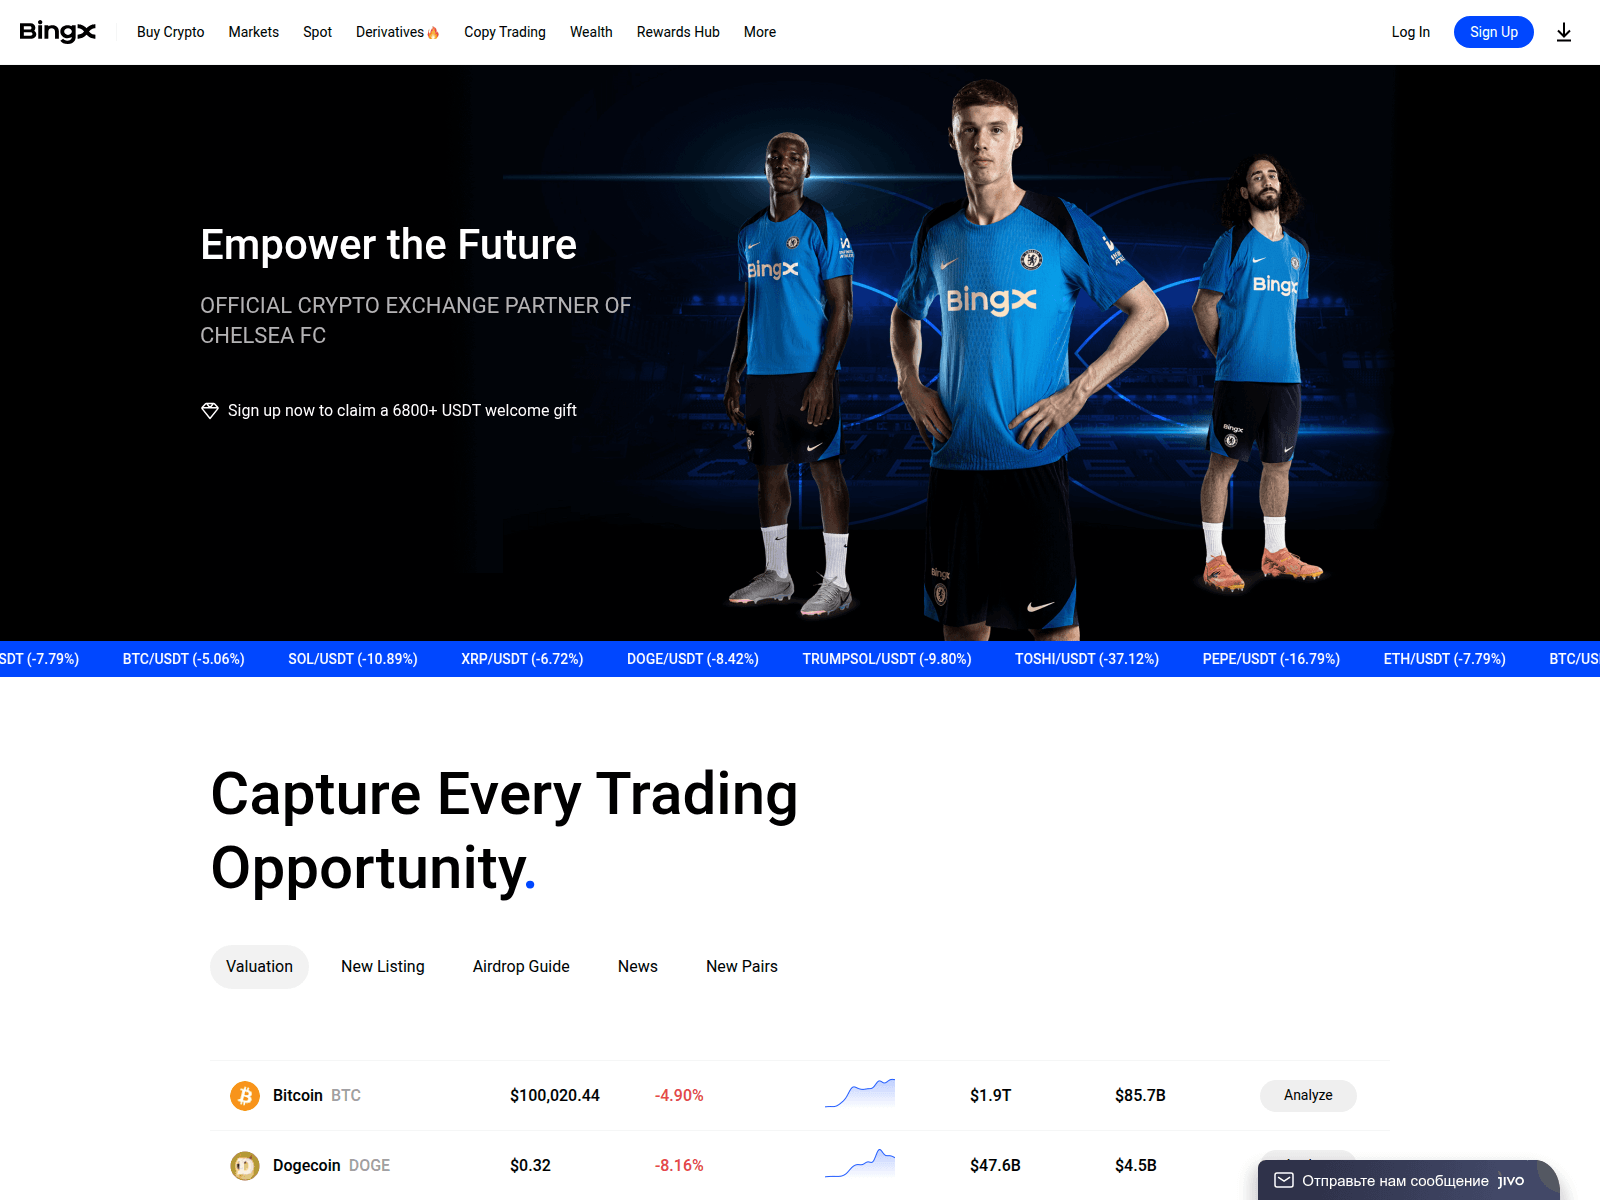 Click the image to view full size
98
Likely scamScam likelihood 98/100
The page impersonates BingX on the unrelated domain bingpersonal-mikhailova.com, promotes a 6800+ USDT sign-up gift, and claims Chelsea FC partnership. The cloned exchange branding and domain mismatch strongly indicate credential and deposit phishing.
ImpersonationAnalyzed by ChatGPT 5.6-sol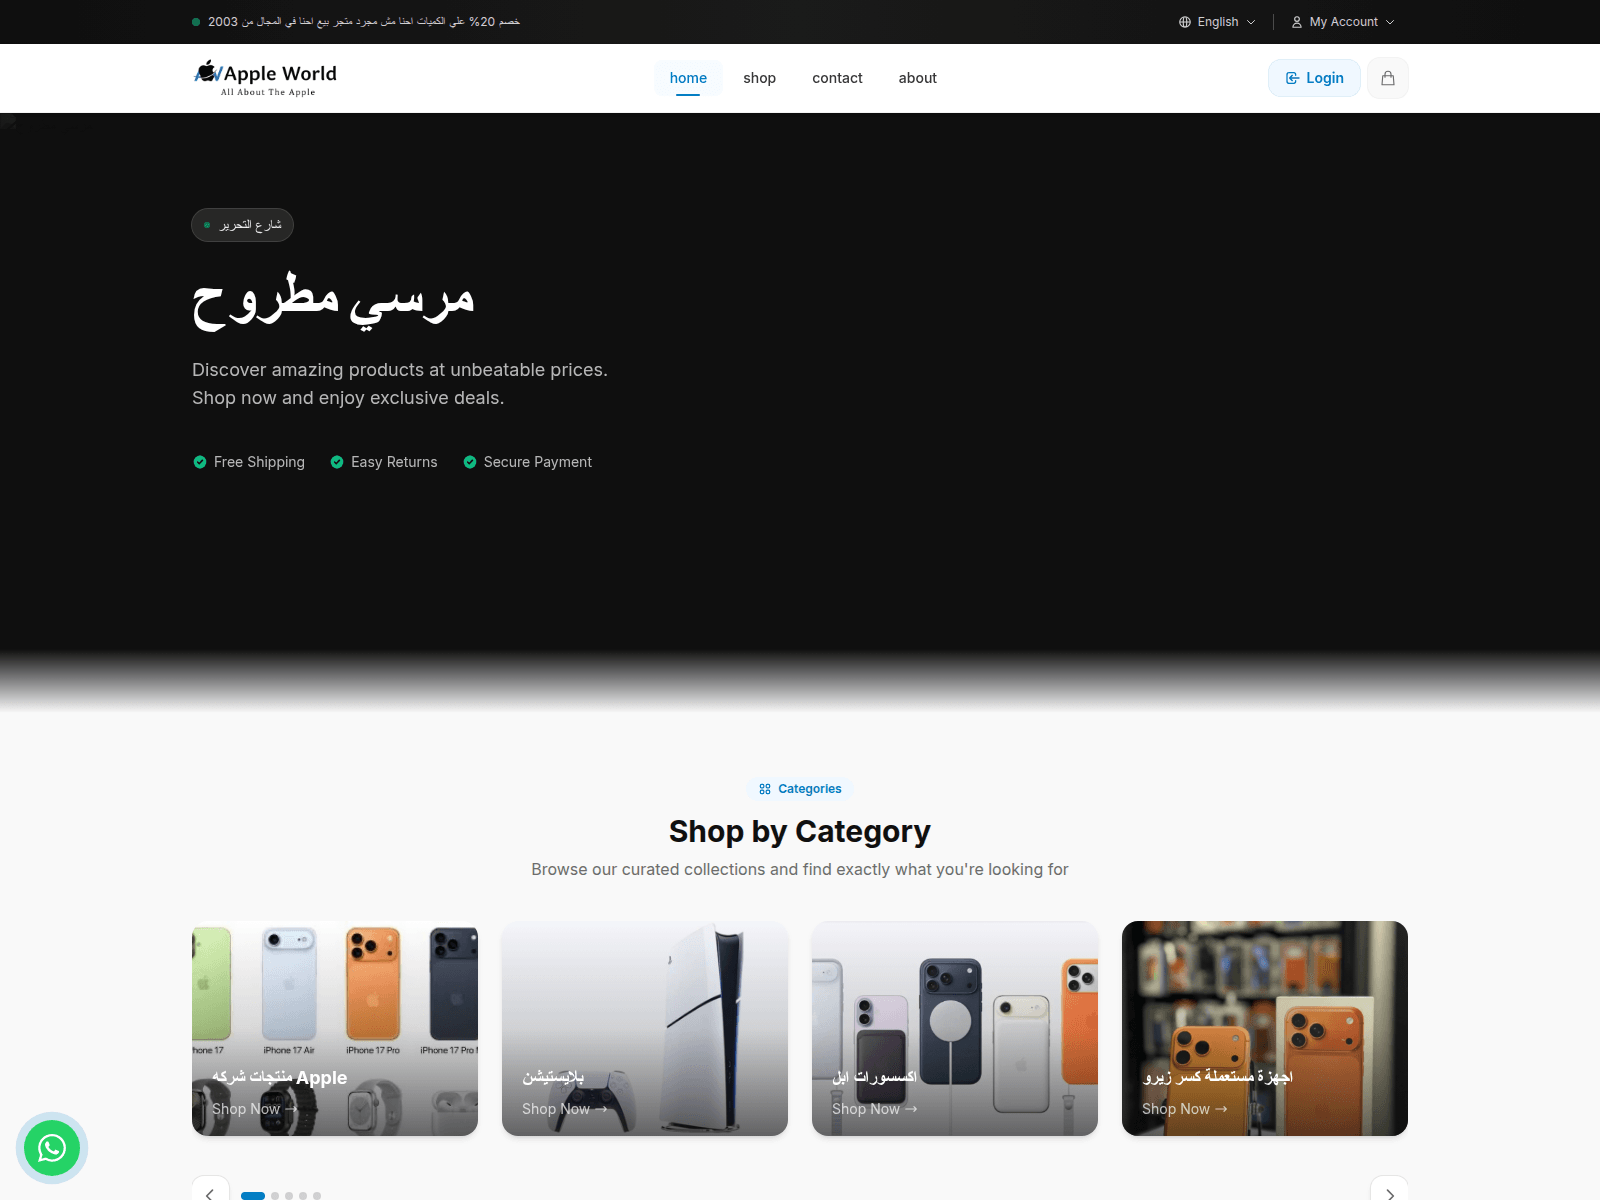 Click the image to view full size
86
Likely scamScam likelihood 86/100
The non-Apple domain appleworldonline.com uses an Apple-like logo, the name 'Apple World,' Apple product imagery, login, cart, and secure-payment claims. This creates a strong risk of brand impersonation and fraudulent or counterfeit sales.
ImpersonationAnalyzed by ChatGPT 5.6-sol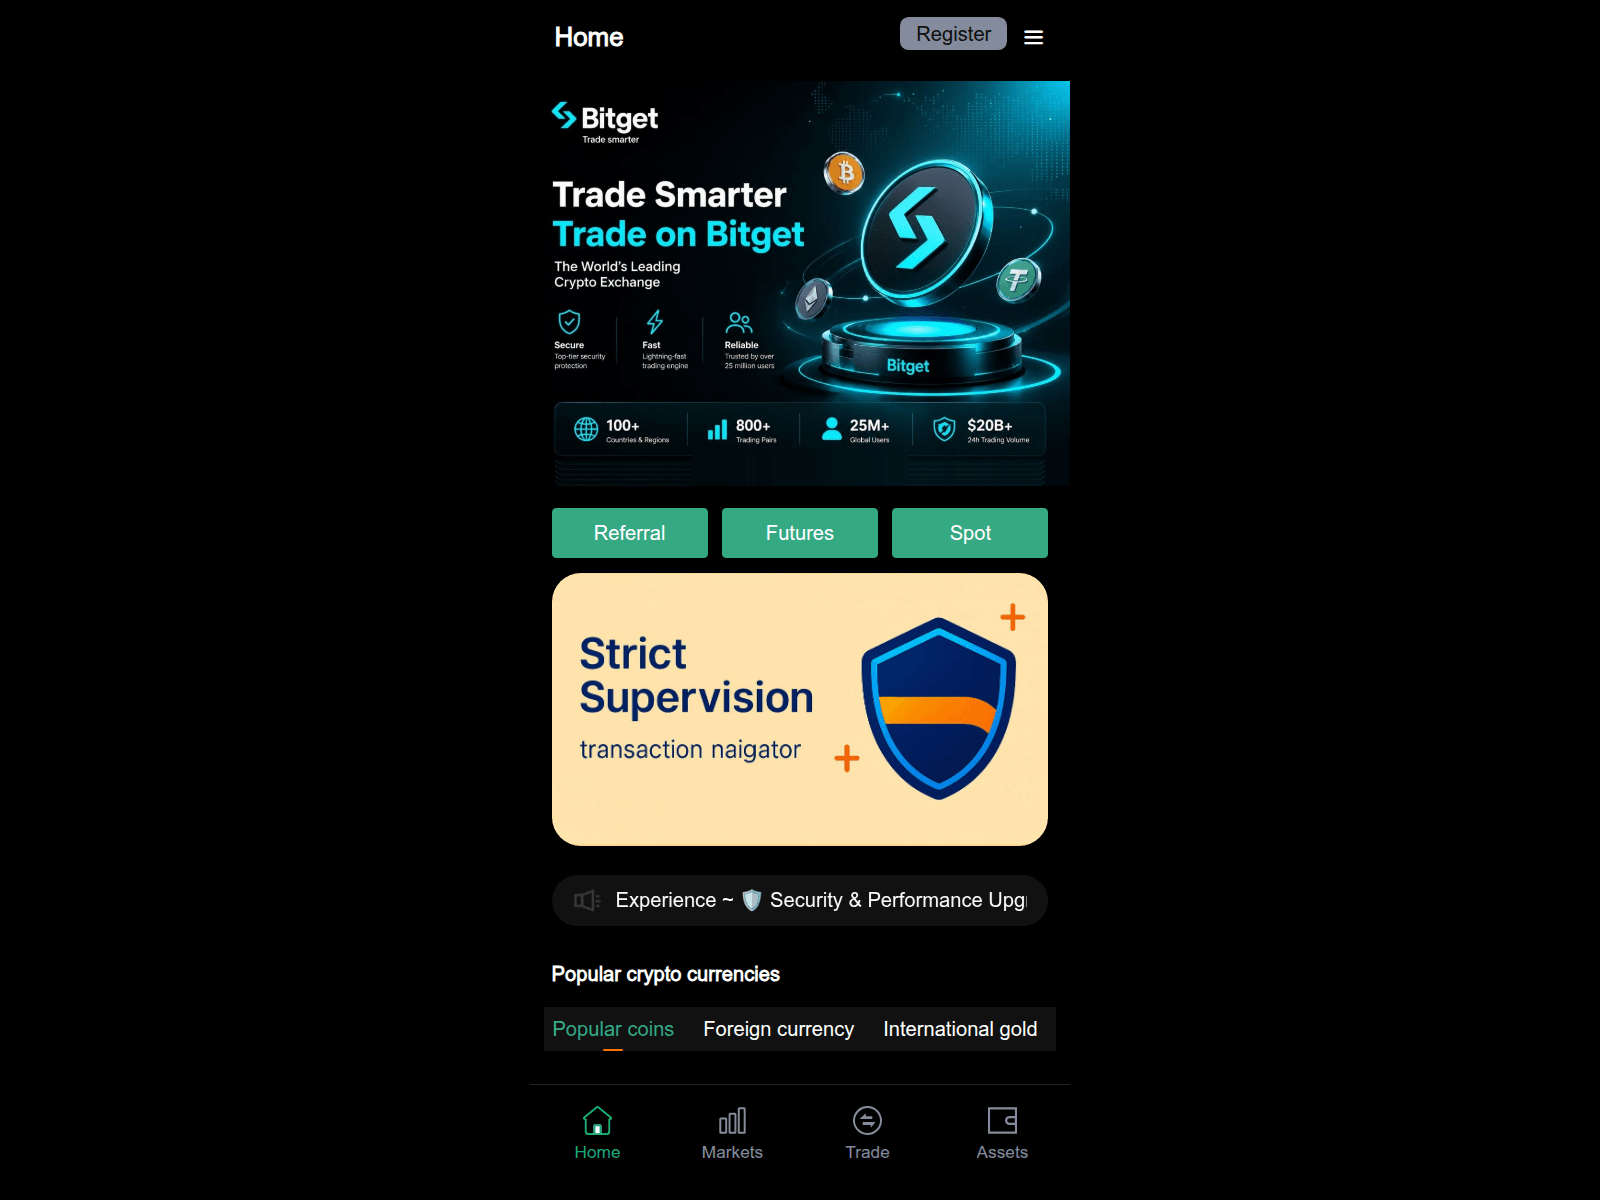 Click the image to view full size
98
Likely scamScam likelihood 98/100
The page copies Bitget branding, logo, exchange claims, and crypto trading interface while operating on niygvxns.top rather than bitget.com. The prominent Register control and Referral, Futures, Spot, Trade, and Assets features indicate a credential or deposit-harvesting clone.
ImpersonationAnalyzed by ChatGPT 5.6-sol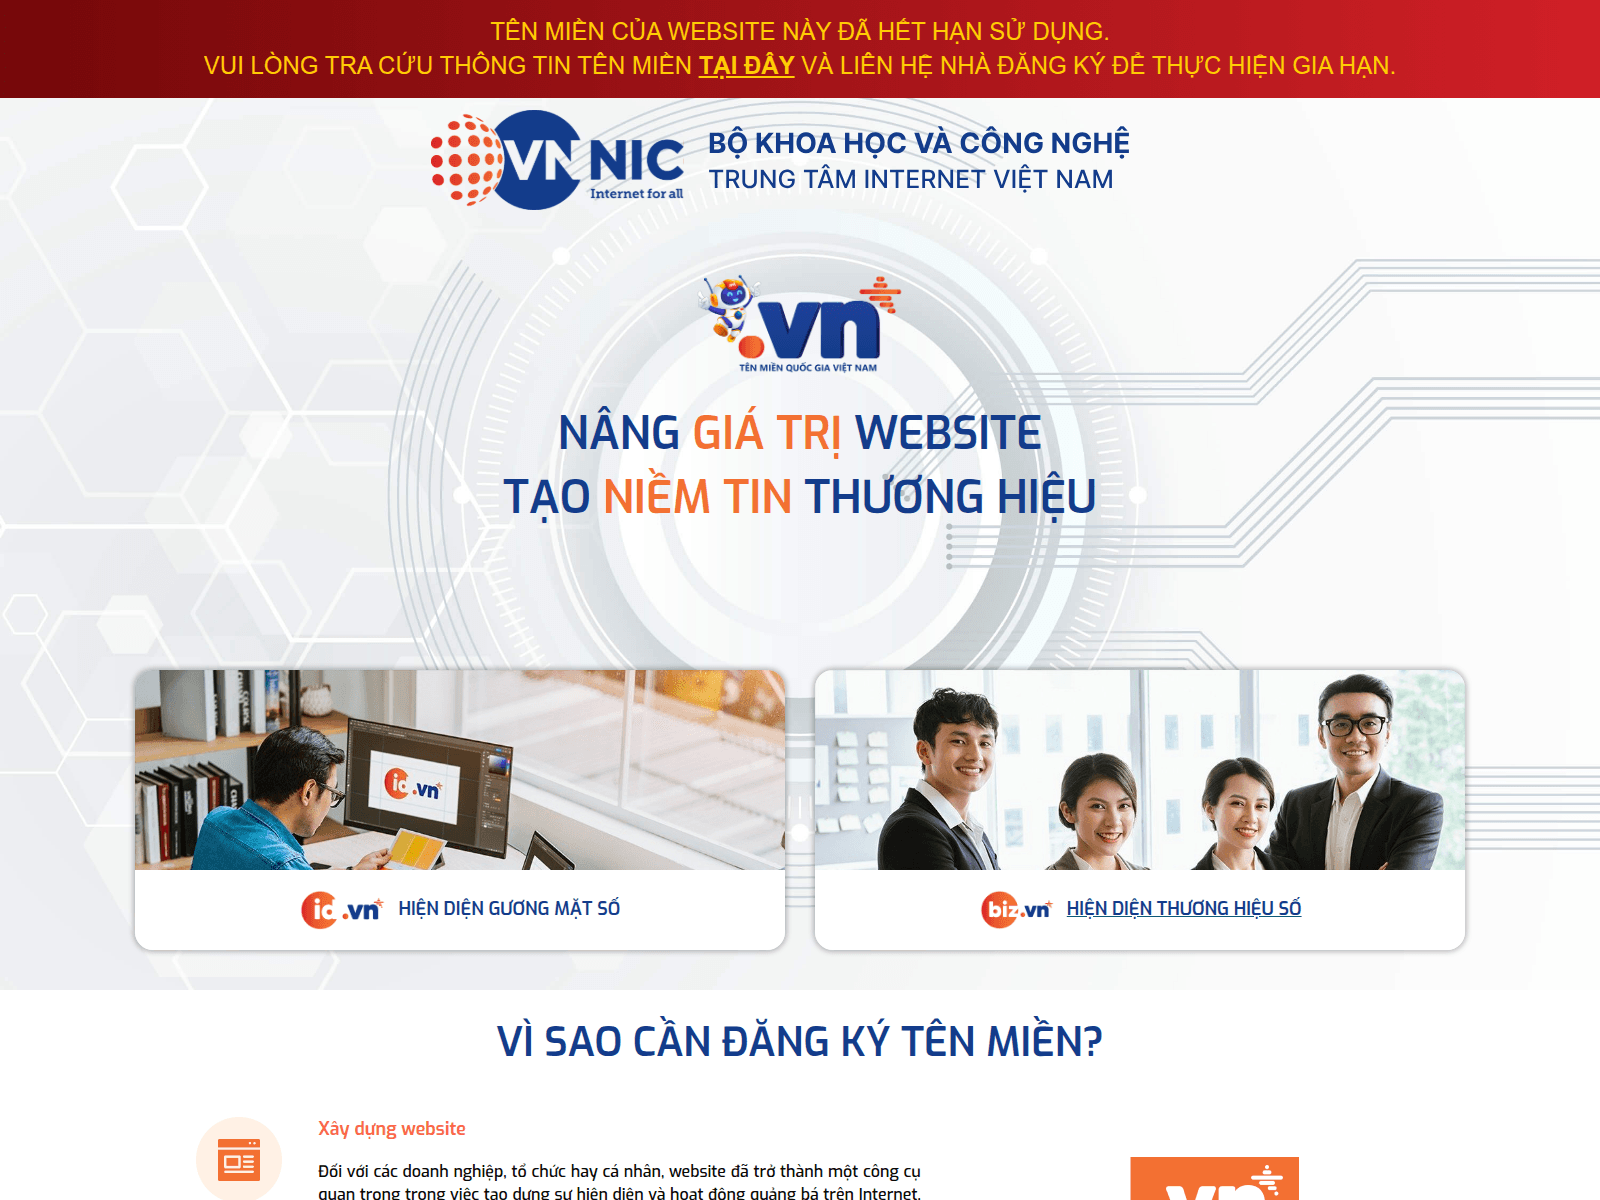 Click the image to view full size
90
Likely scamScam likelihood 90/100
The non-official cpanel.cdt-jadesquare.com.vn page prominently presents VNNIC and Ministry branding, warns that the domain expired, and directs users to click and contact a registrar for renewal. This domain-brand mismatch strongly indicates government impersonation and phishing risk.
ImpersonationAnalyzed by ChatGPT 5.6-sol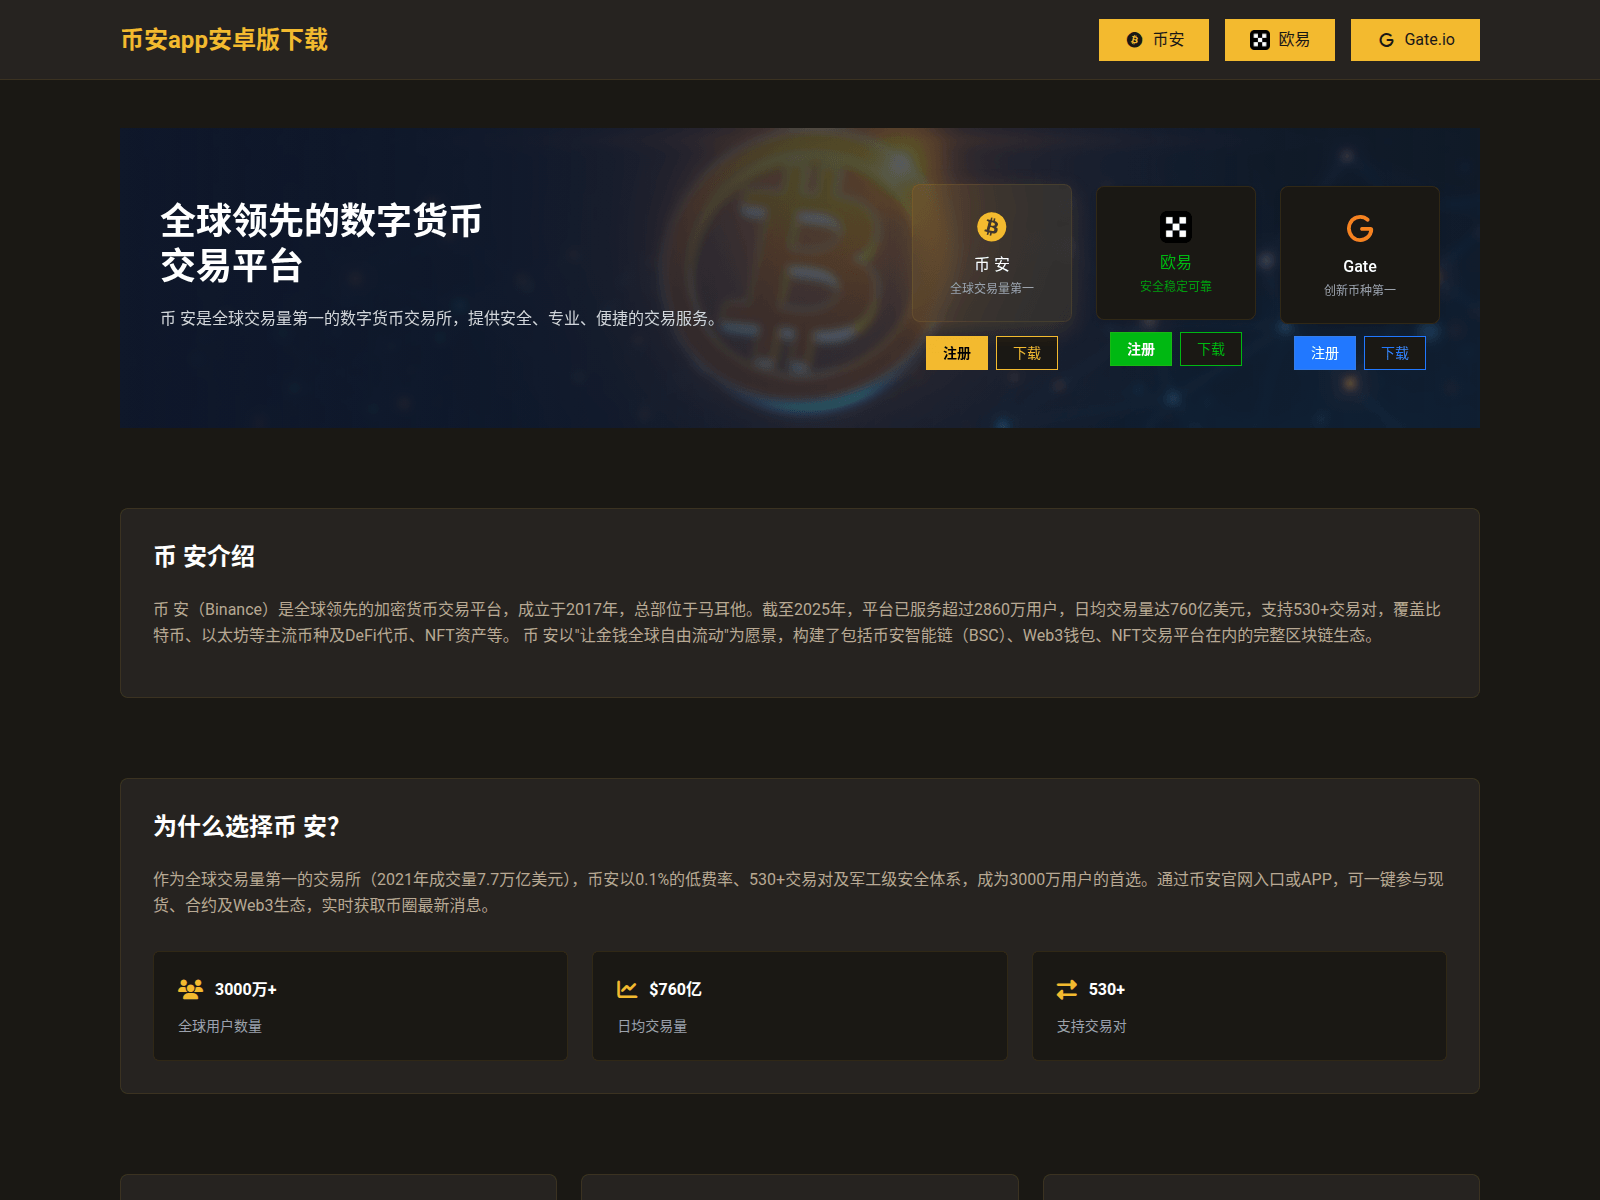 Click the image to view full size
98
Likely scamScam likelihood 98/100
页面冒用币安、欧易及Gate.io品牌,提供注册和下载按钮,并声称币安为全球第一交易平台。域名wei.cbinance.com.cn与币安官方binance.com不符,属于明确的交易所仿冒及高风险应用下载诱导。
ImpersonationAnalyzed by ChatGPT 5.6-sol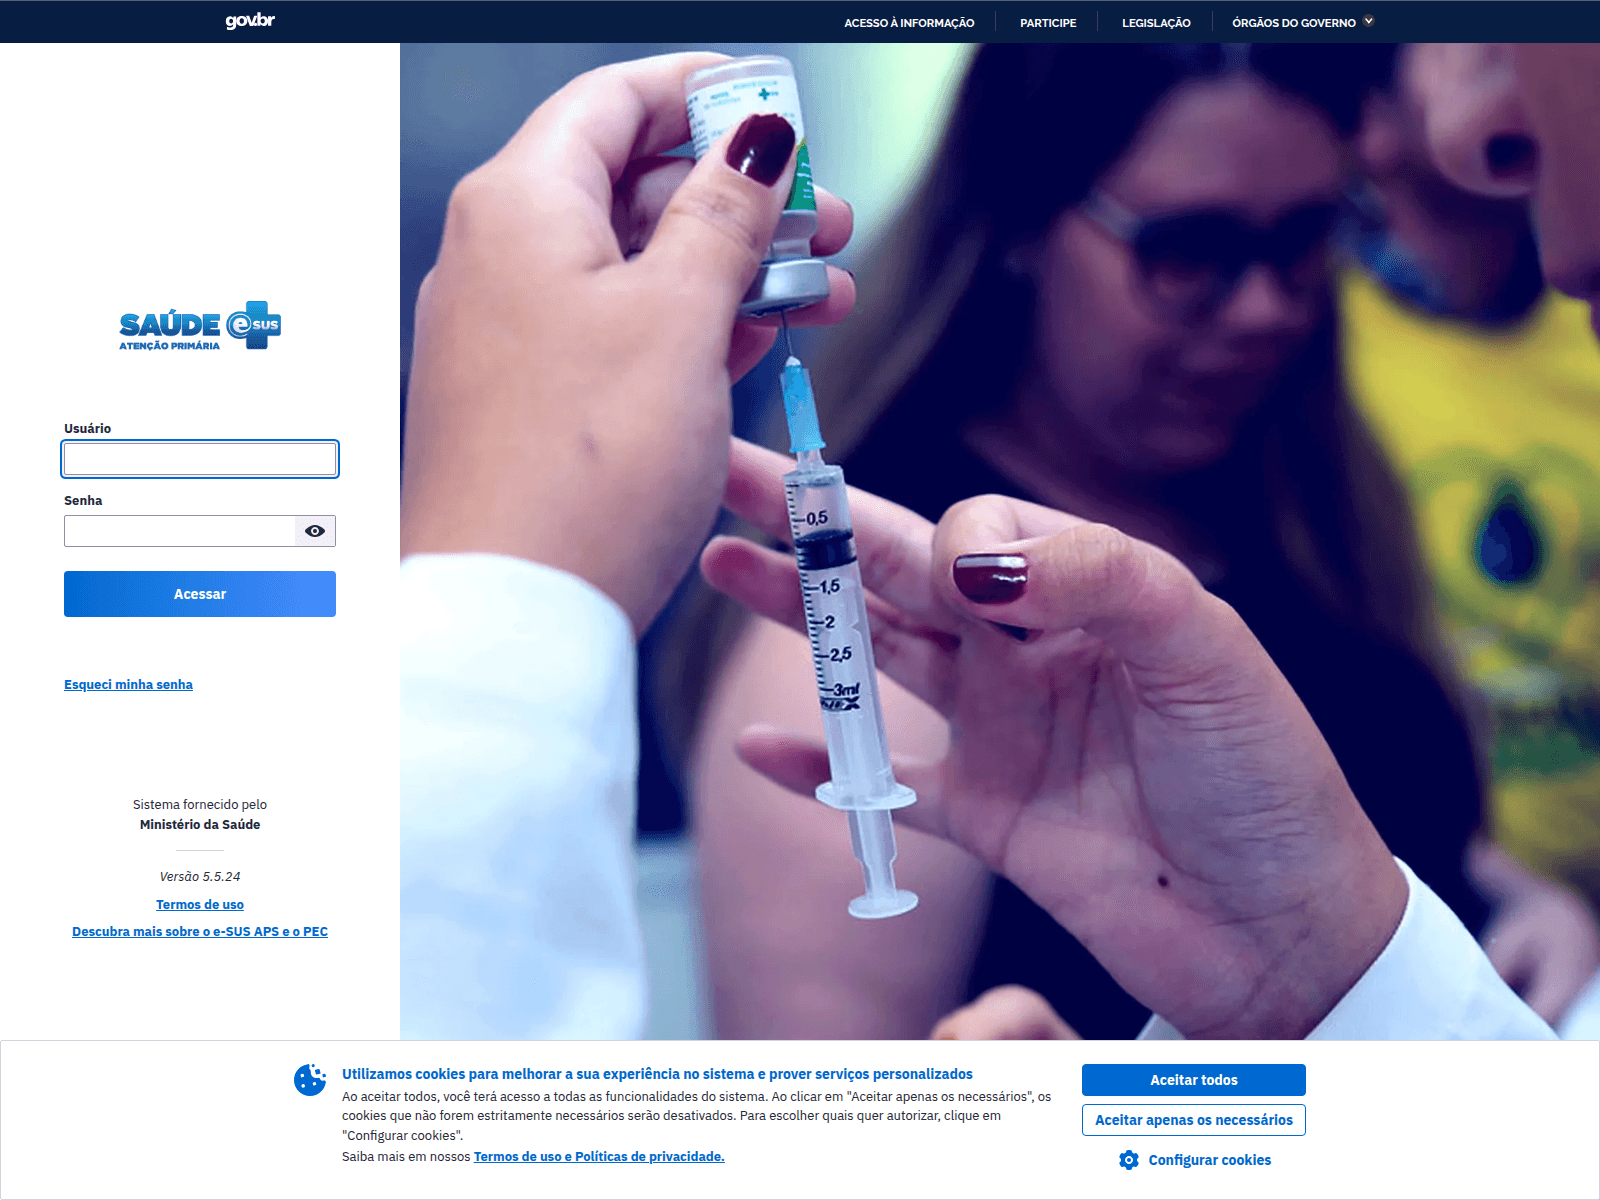 Click the image to view full size
99
Likely scamScam likelihood 99/100
The page uses gov.br, Saúde, e-SUS, and Ministério da Saúde branding while requesting a username and password. Metadata identifies the unrelated domain irara.maisgestor.com.br, a clear government impersonation and credential-phishing mismatch.
ImpersonationAnalyzed by ChatGPT 5.6-sol Click the image to view full size
94
Likely scamScam likelihood 94/100
The unrelated nextelgroup.top domain uses Nextel-style telecom branding for an unaffiliated 'eSIM verified ad network,' pairing unsupported '100% verified' and '1M+' claims with 'Start Earning Now' and account sign-in prompts. This strongly indicates impersonation and fraud.
ImpersonationAnalyzed by ChatGPT 5.6-sol Click the image to view full size
96
Likely scamScam likelihood 96/100
The page claims to offer the official OKX app and uses OKX branding, registration and download buttons, plus a QR-code download. Metadata identifies the host as granolaslaviajera.com rather than okx.com, a clear domain mismatch consistent with credential theft or malicious app distribution.
ImpersonationAnalyzed by ChatGPT 5.6-sol Click the image to view full size
96
Likely scamScam likelihood 96/100
The unrelated domain zagraionline-pl-app.website claims 'Oficjalna aplikacja LOTTO', uses the LOTTO logo, and prompts a direct download. This clear brand impersonation and unofficial distribution channel strongly indicate phishing or a malicious app.
ImpersonationAnalyzed by ChatGPT 5.6-sol Click the image to view full size
98
Likely scamScam likelihood 98/100
The storefront uses Yostar branding, claims to sell 'exclusive official merchandise' for Arknights and Azur Lane, and provides account/cart functions. The supplied domain, yostarhoutpost.shop, is unaffiliated with Yostar, indicating impersonation and payment-harvesting risk.
ImpersonationAnalyzed by ChatGPT 5.6-sol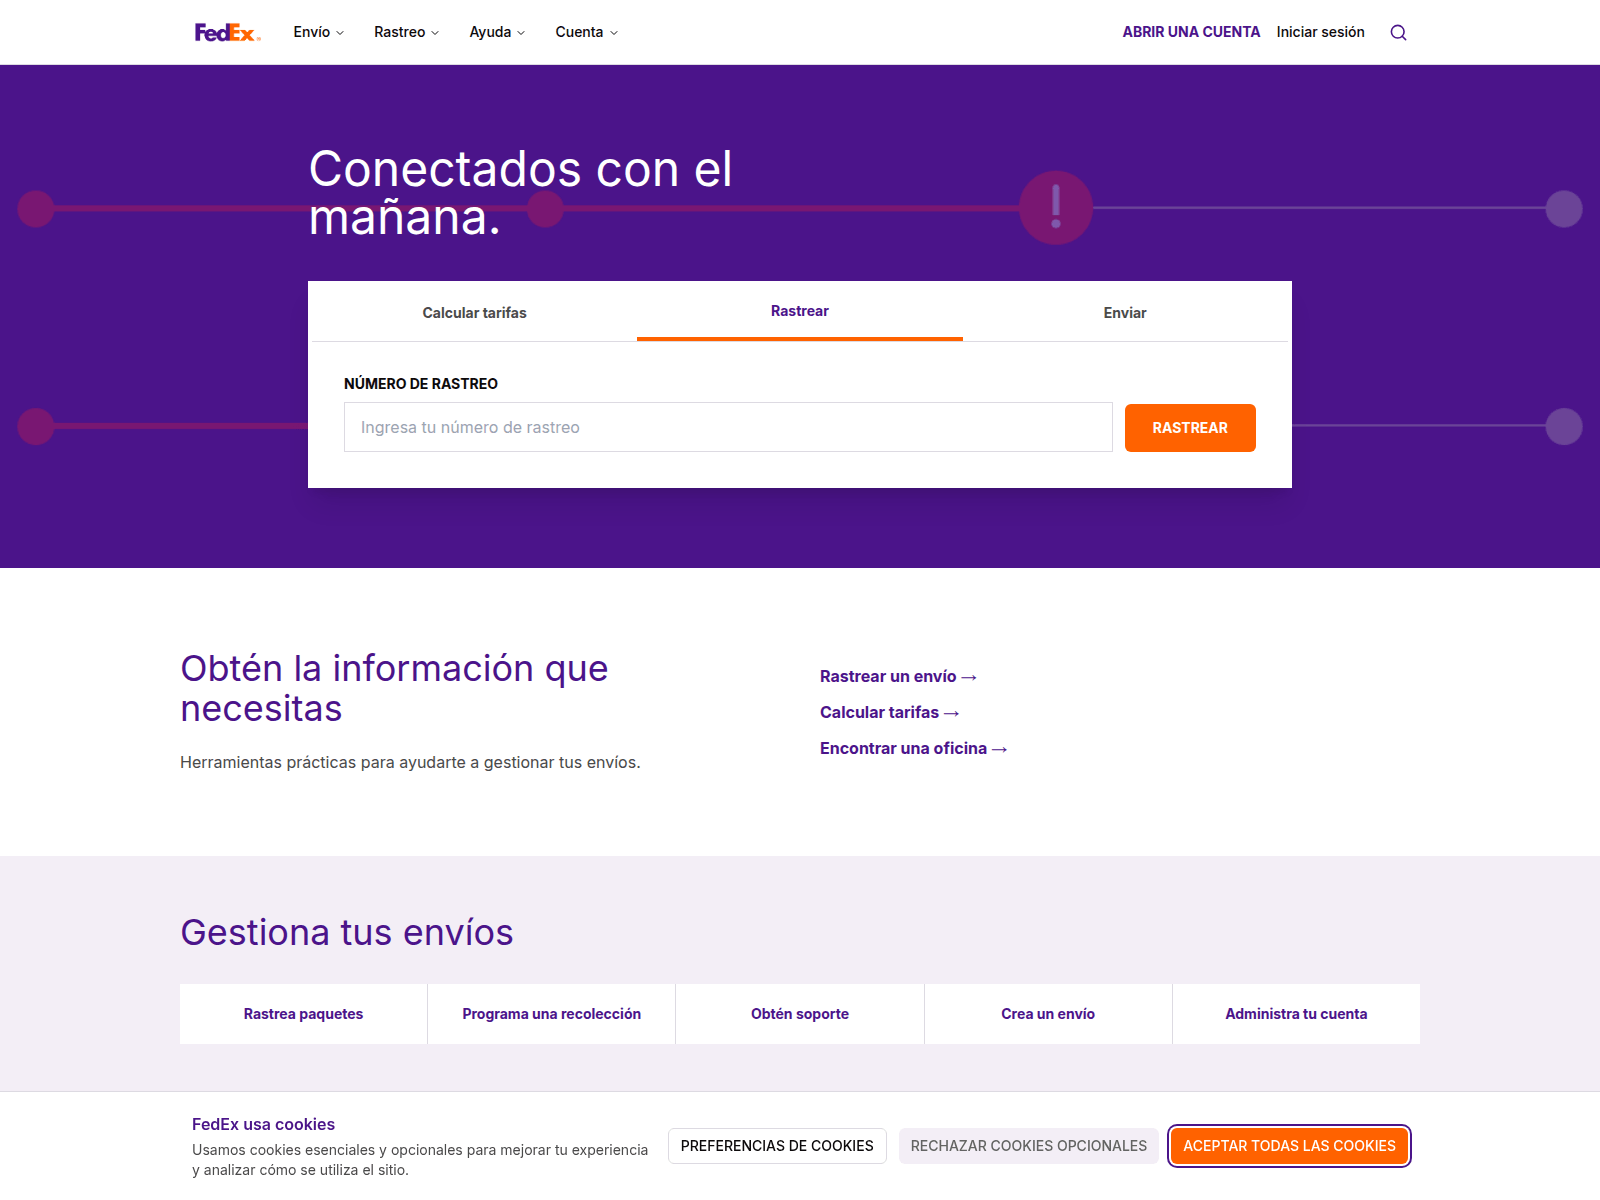 Click the image to view full size
98
Likely scamScam likelihood 98/100
The page copies FedEx branding, tracking tools, and an account sign-in prompt, while metadata identifies the domain as fedex-srl.com rather than the official fedex.com. This clear domain-brand mismatch strongly indicates credential and data harvesting.
ImpersonationAnalyzed by ChatGPT 5.6-sol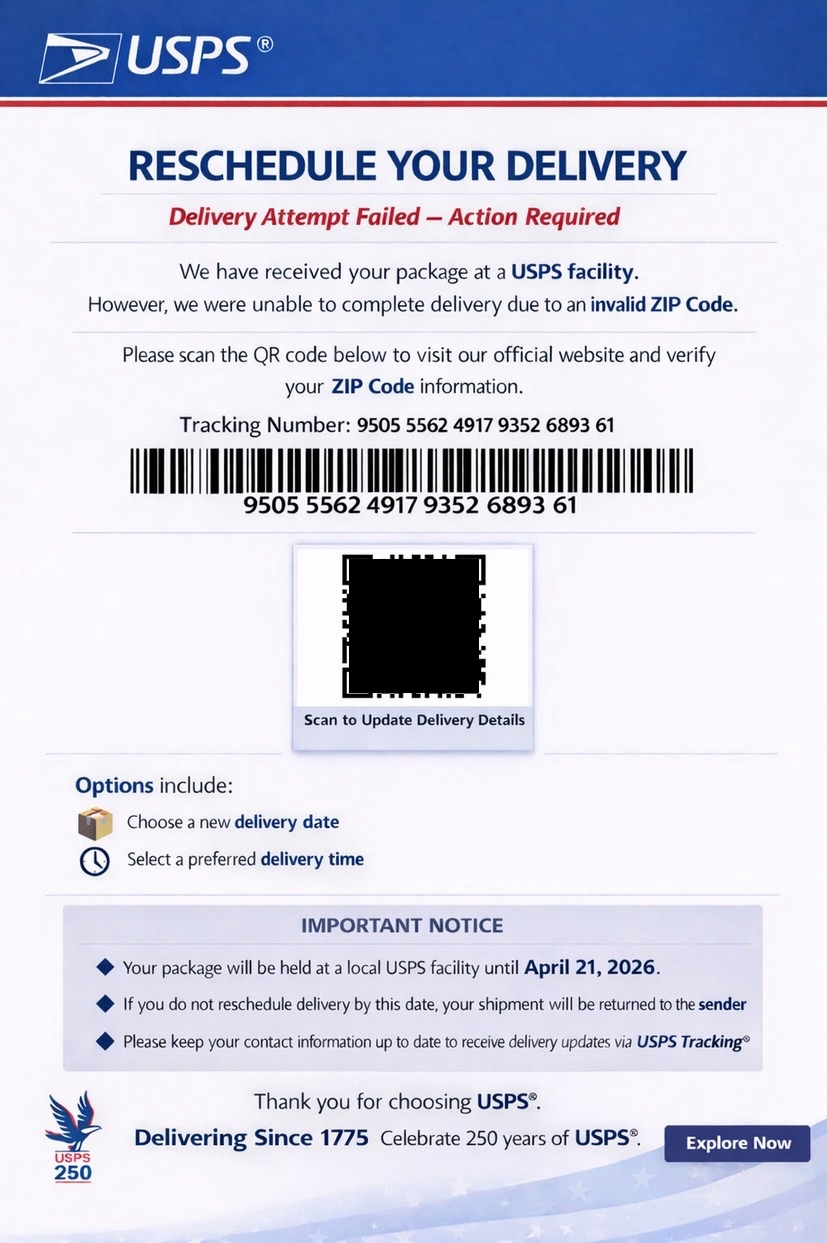 Click the image to view full size
96
Likely scamScam likelihood 96/100
Likely USPS phishing: it impersonates USPS, claims a failed delivery due to an invalid ZIP Code, and directs the recipient to scan a QR code to update details. The stated April 21, 2026 deadline has already passed, further undermining authenticity.
ImpersonationAnalyzed by ChatGPT 5.6-sol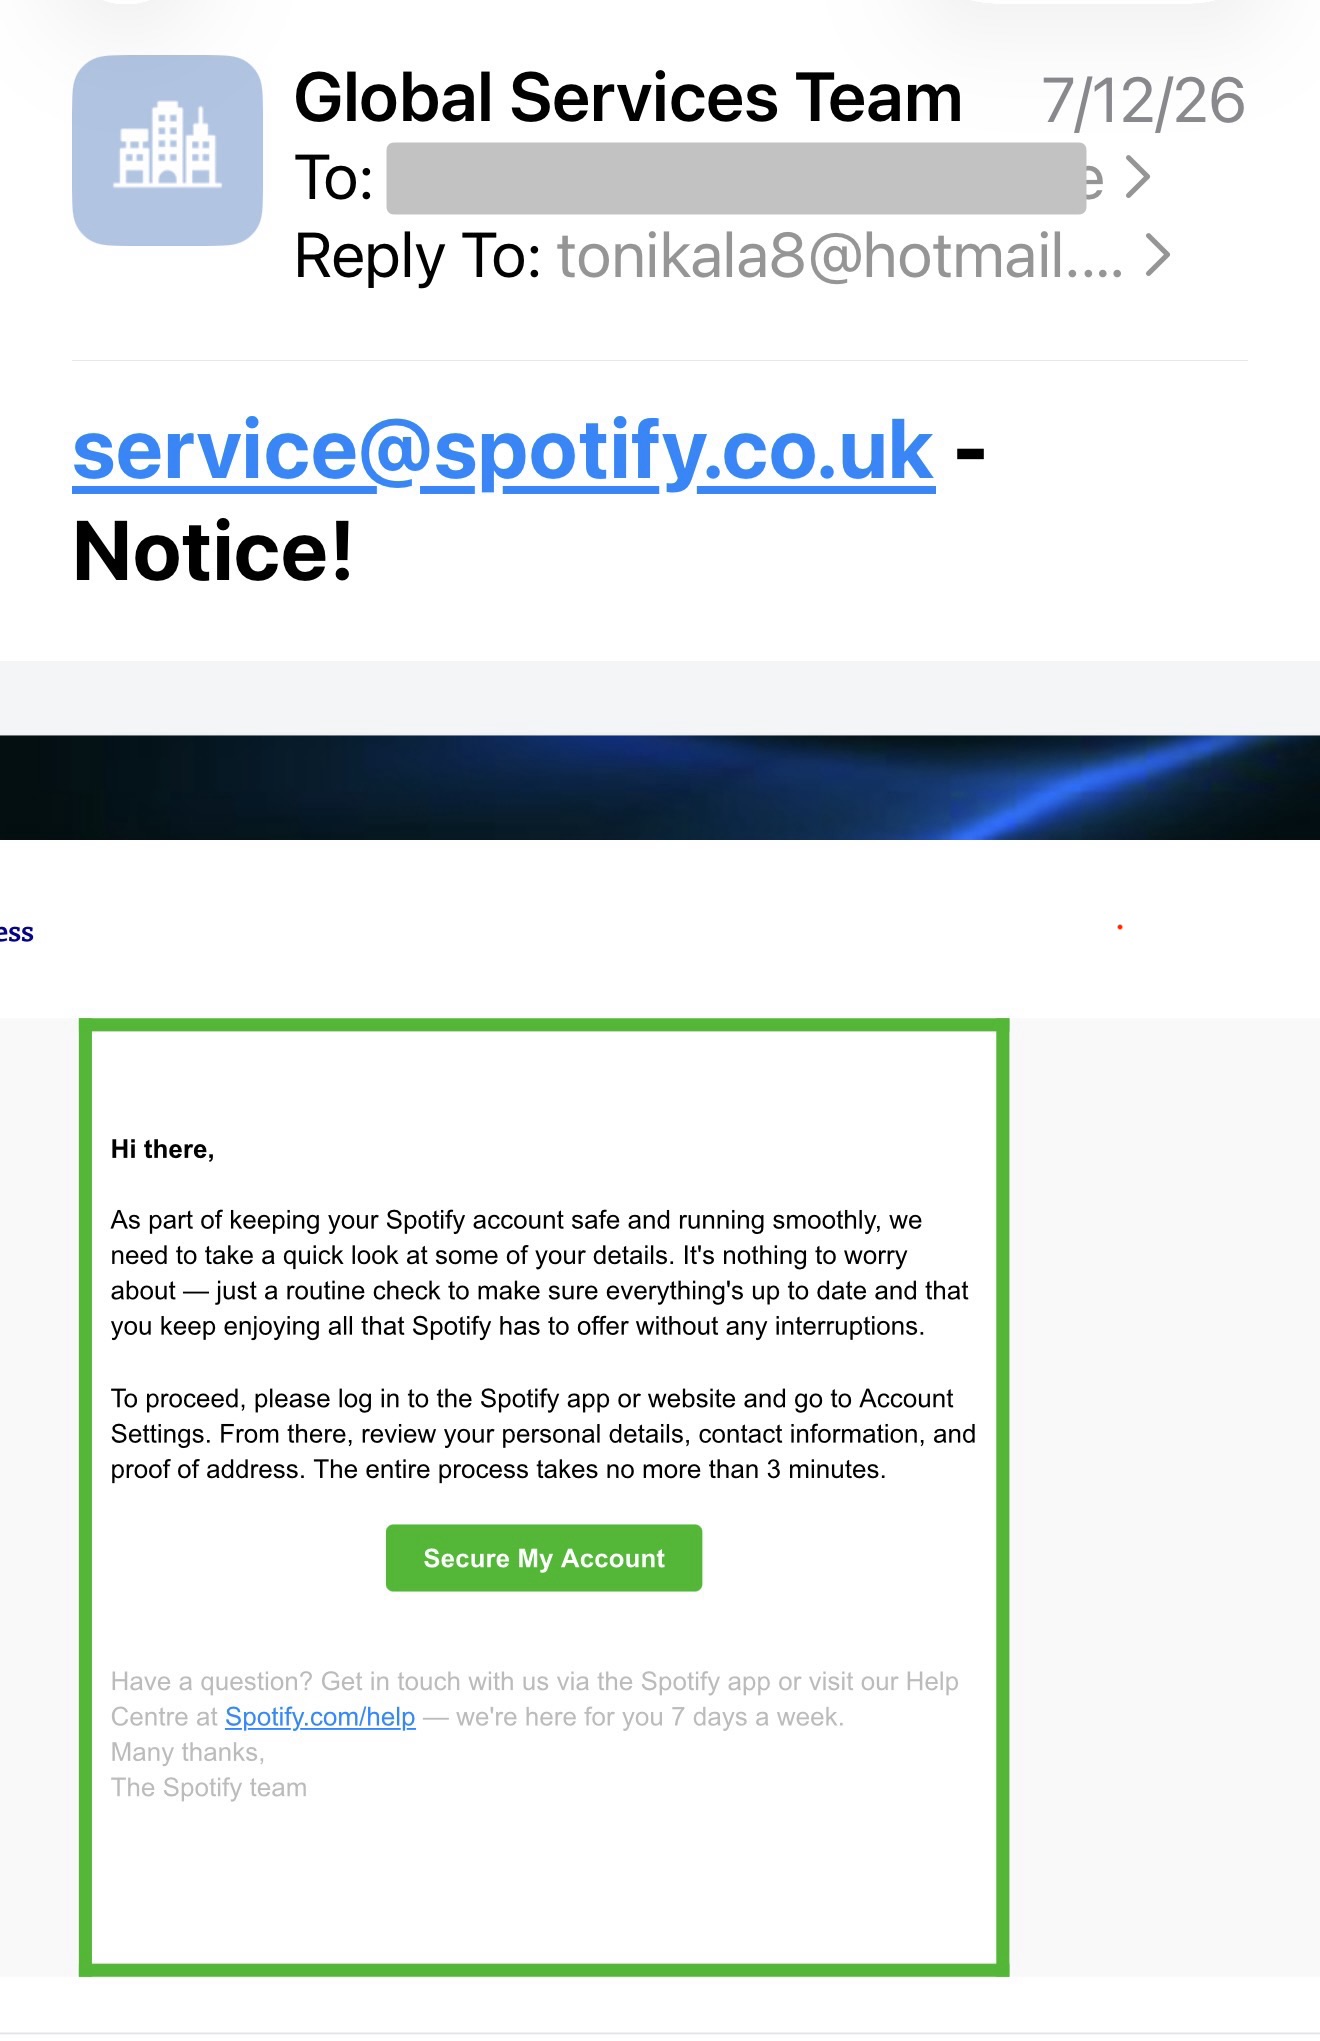 Click the image to view full size
98
Likely scamScam likelihood 98/100
Spotify impersonation and likely credential phishing. The sender is 'Global Services Team', reply-to is a Hotmail address, and the subject oddly displays 'service@spotify.co.uk'. It requests personal details and proof of address through a 'Secure My Account' button.
ImpersonationAnalyzed by ChatGPT 5.6-sol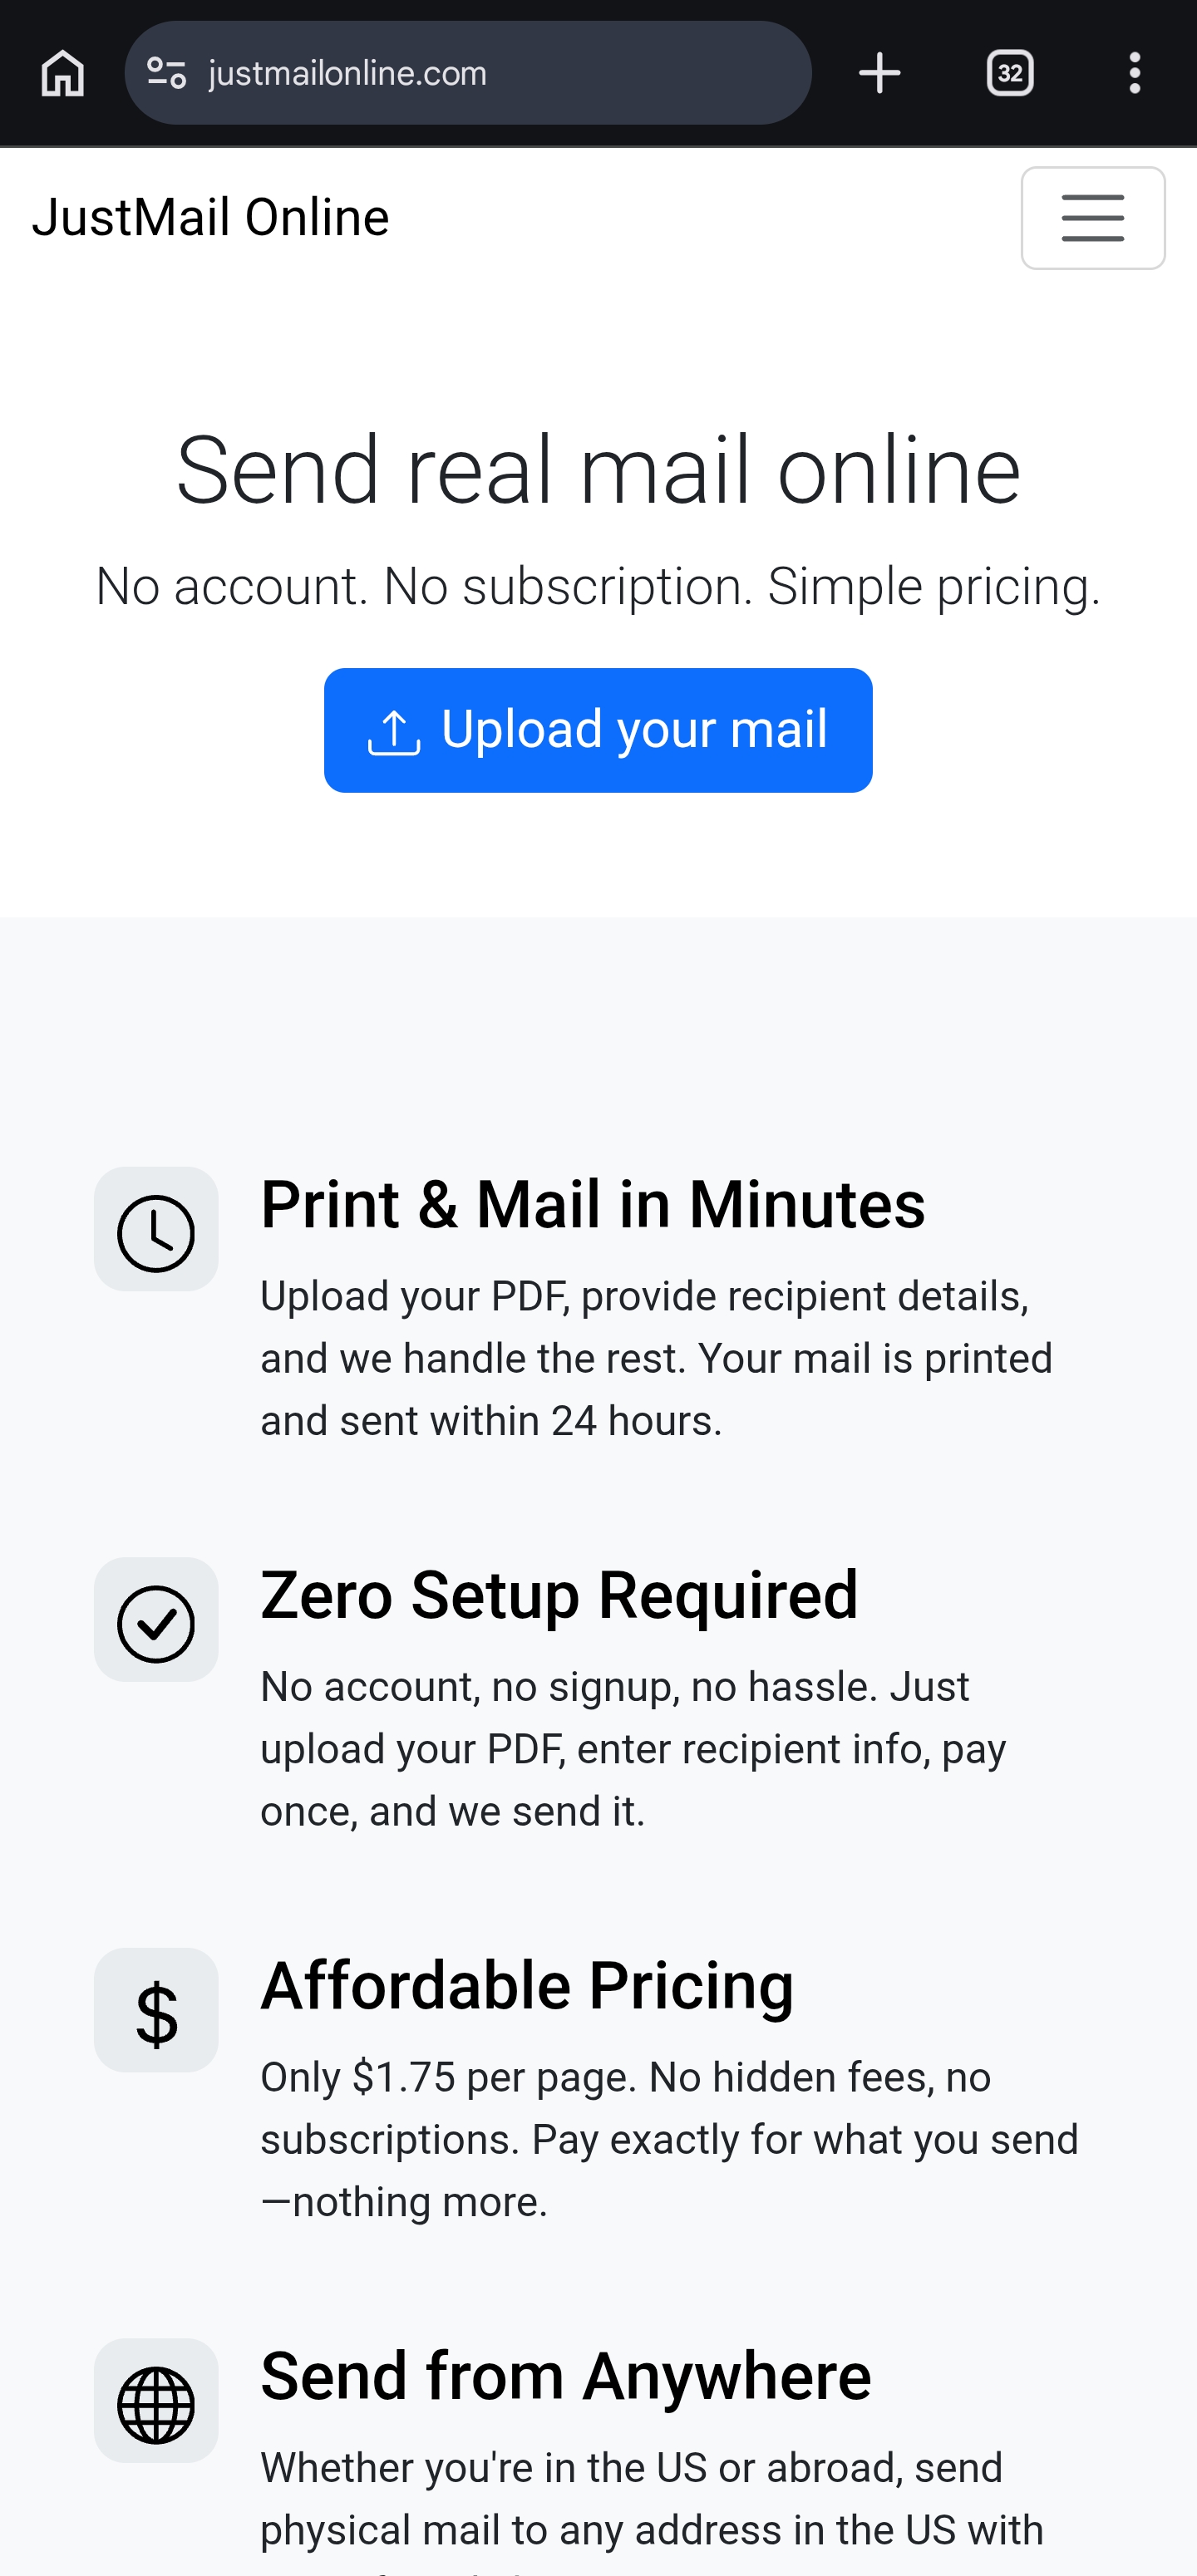 Click the image to view full size
88
Likely scamScam likelihood 88/100
The site solicits payment, uploaded PDFs, and recipient details while promising mail will be printed and sent within 24 hours. The submitter reports that paid mail is never delivered, indicating a fraudulent paid-service scheme and potential data collection risk.
ImpersonationAnalyzed by ChatGPT 5.6-sol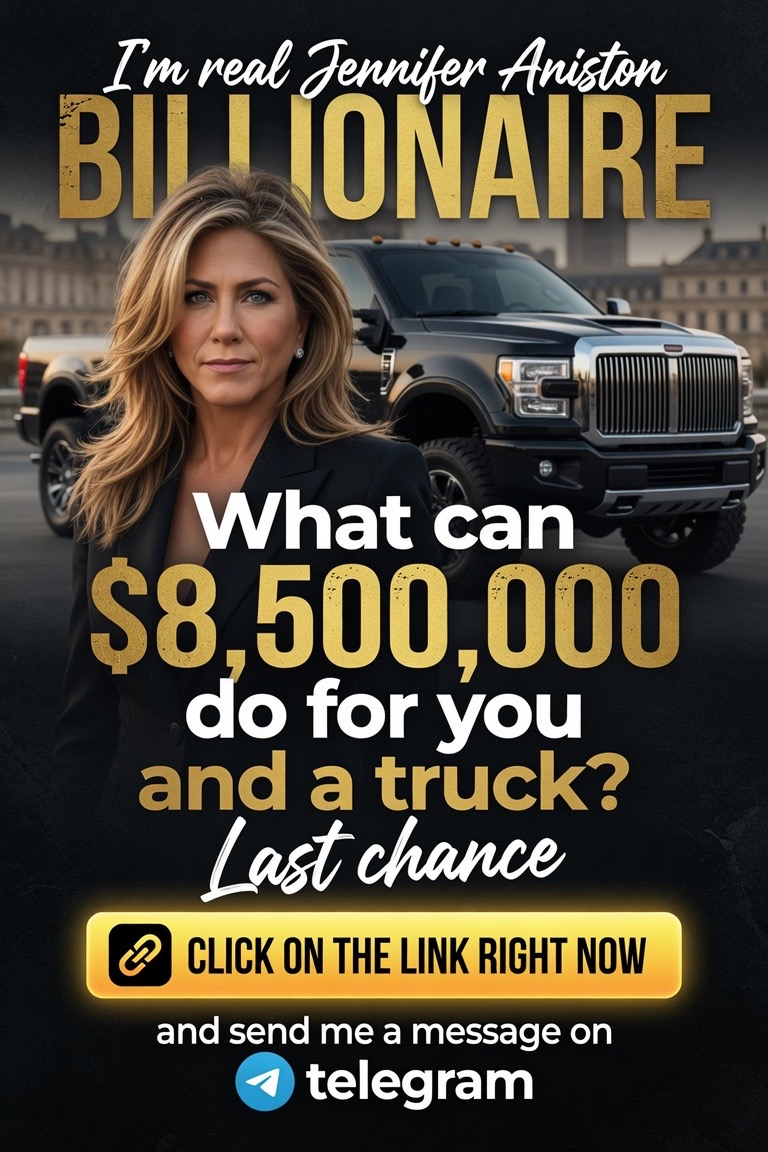 Click the image to view full size
98
Likely scamScam likelihood 98/100
Classic celebrity impersonation giveaway scam: claims to be the 'real Jennifer Aniston' offering $8,500,000 and a truck, with urgency ('Last chance'), a demand to click a link immediately, and redirection to Telegram DM — a hallmark of advance-fee and crypto fraud funnels.
ImpersonationAnalyzed by Claude Opus 5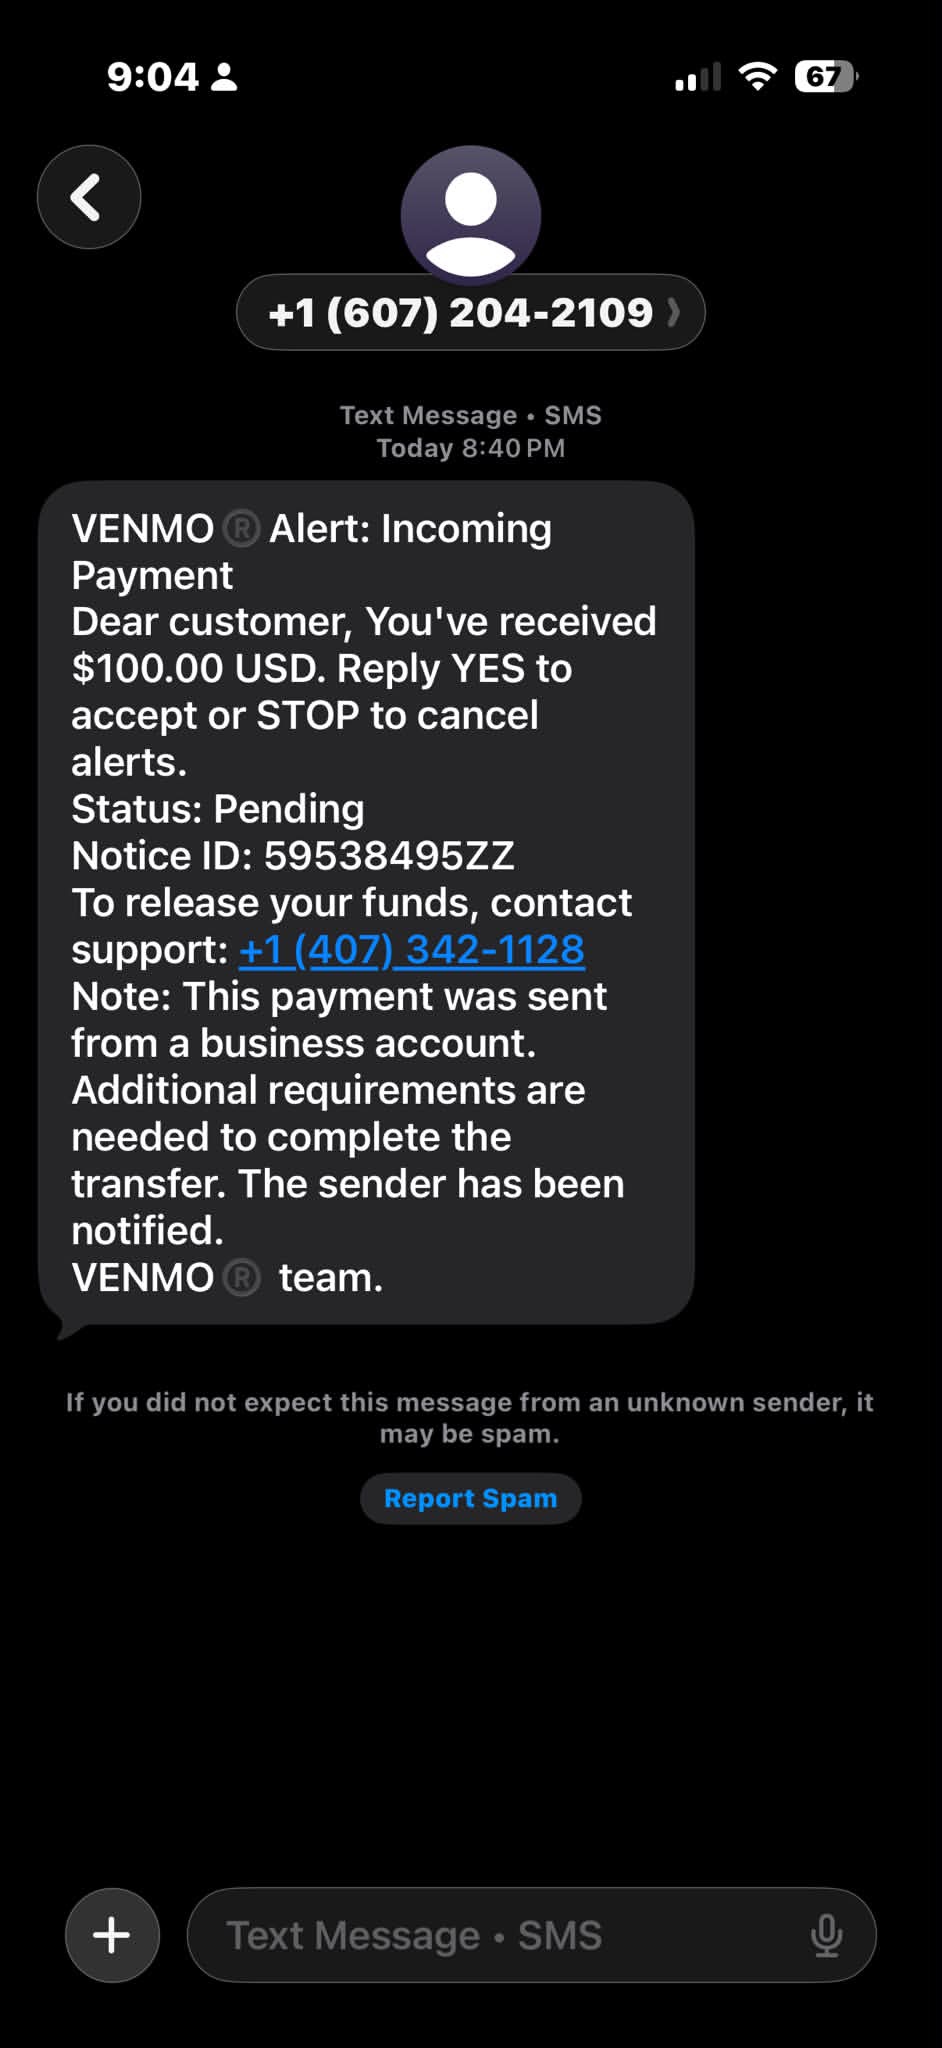 Click the image to view full size
97
Likely scamScam likelihood 97/100
Fraudulent Venmo impersonation from an ordinary phone number. It claims funds are pending due to a business account and directs the seller to an unrelated phone number to release them. These are classic fake-payment and support-impersonation signals.
ImpersonationAnalyzed by ChatGPT 5.6-sol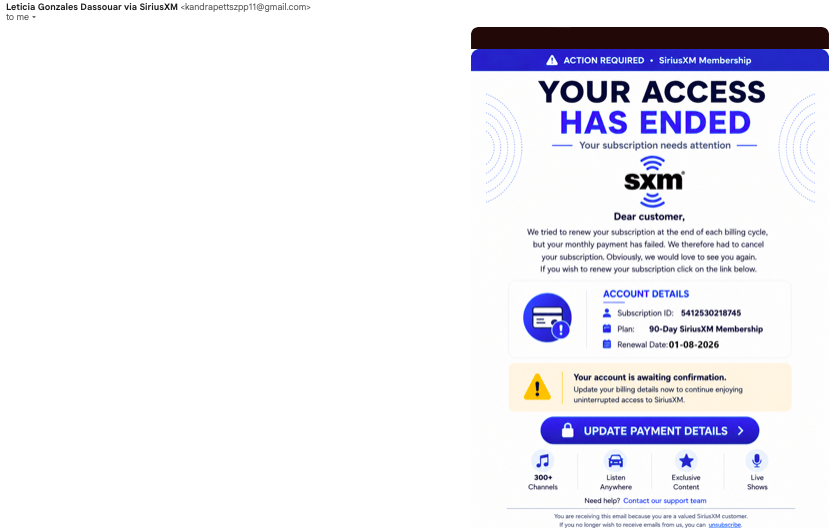 Click the image to view full size
96
Likely scamScam likelihood 96/100
Claims to be SiriusXM membership notice but sender is unrelated Gmail address 'kandrapettzspp11@gmail.com'. Urges 'UPDATE PAYMENT DETAILS' after alleged failed renewal, a clear payment phishing pattern.
ImpersonationAnalyzed by ChatGPT 5.5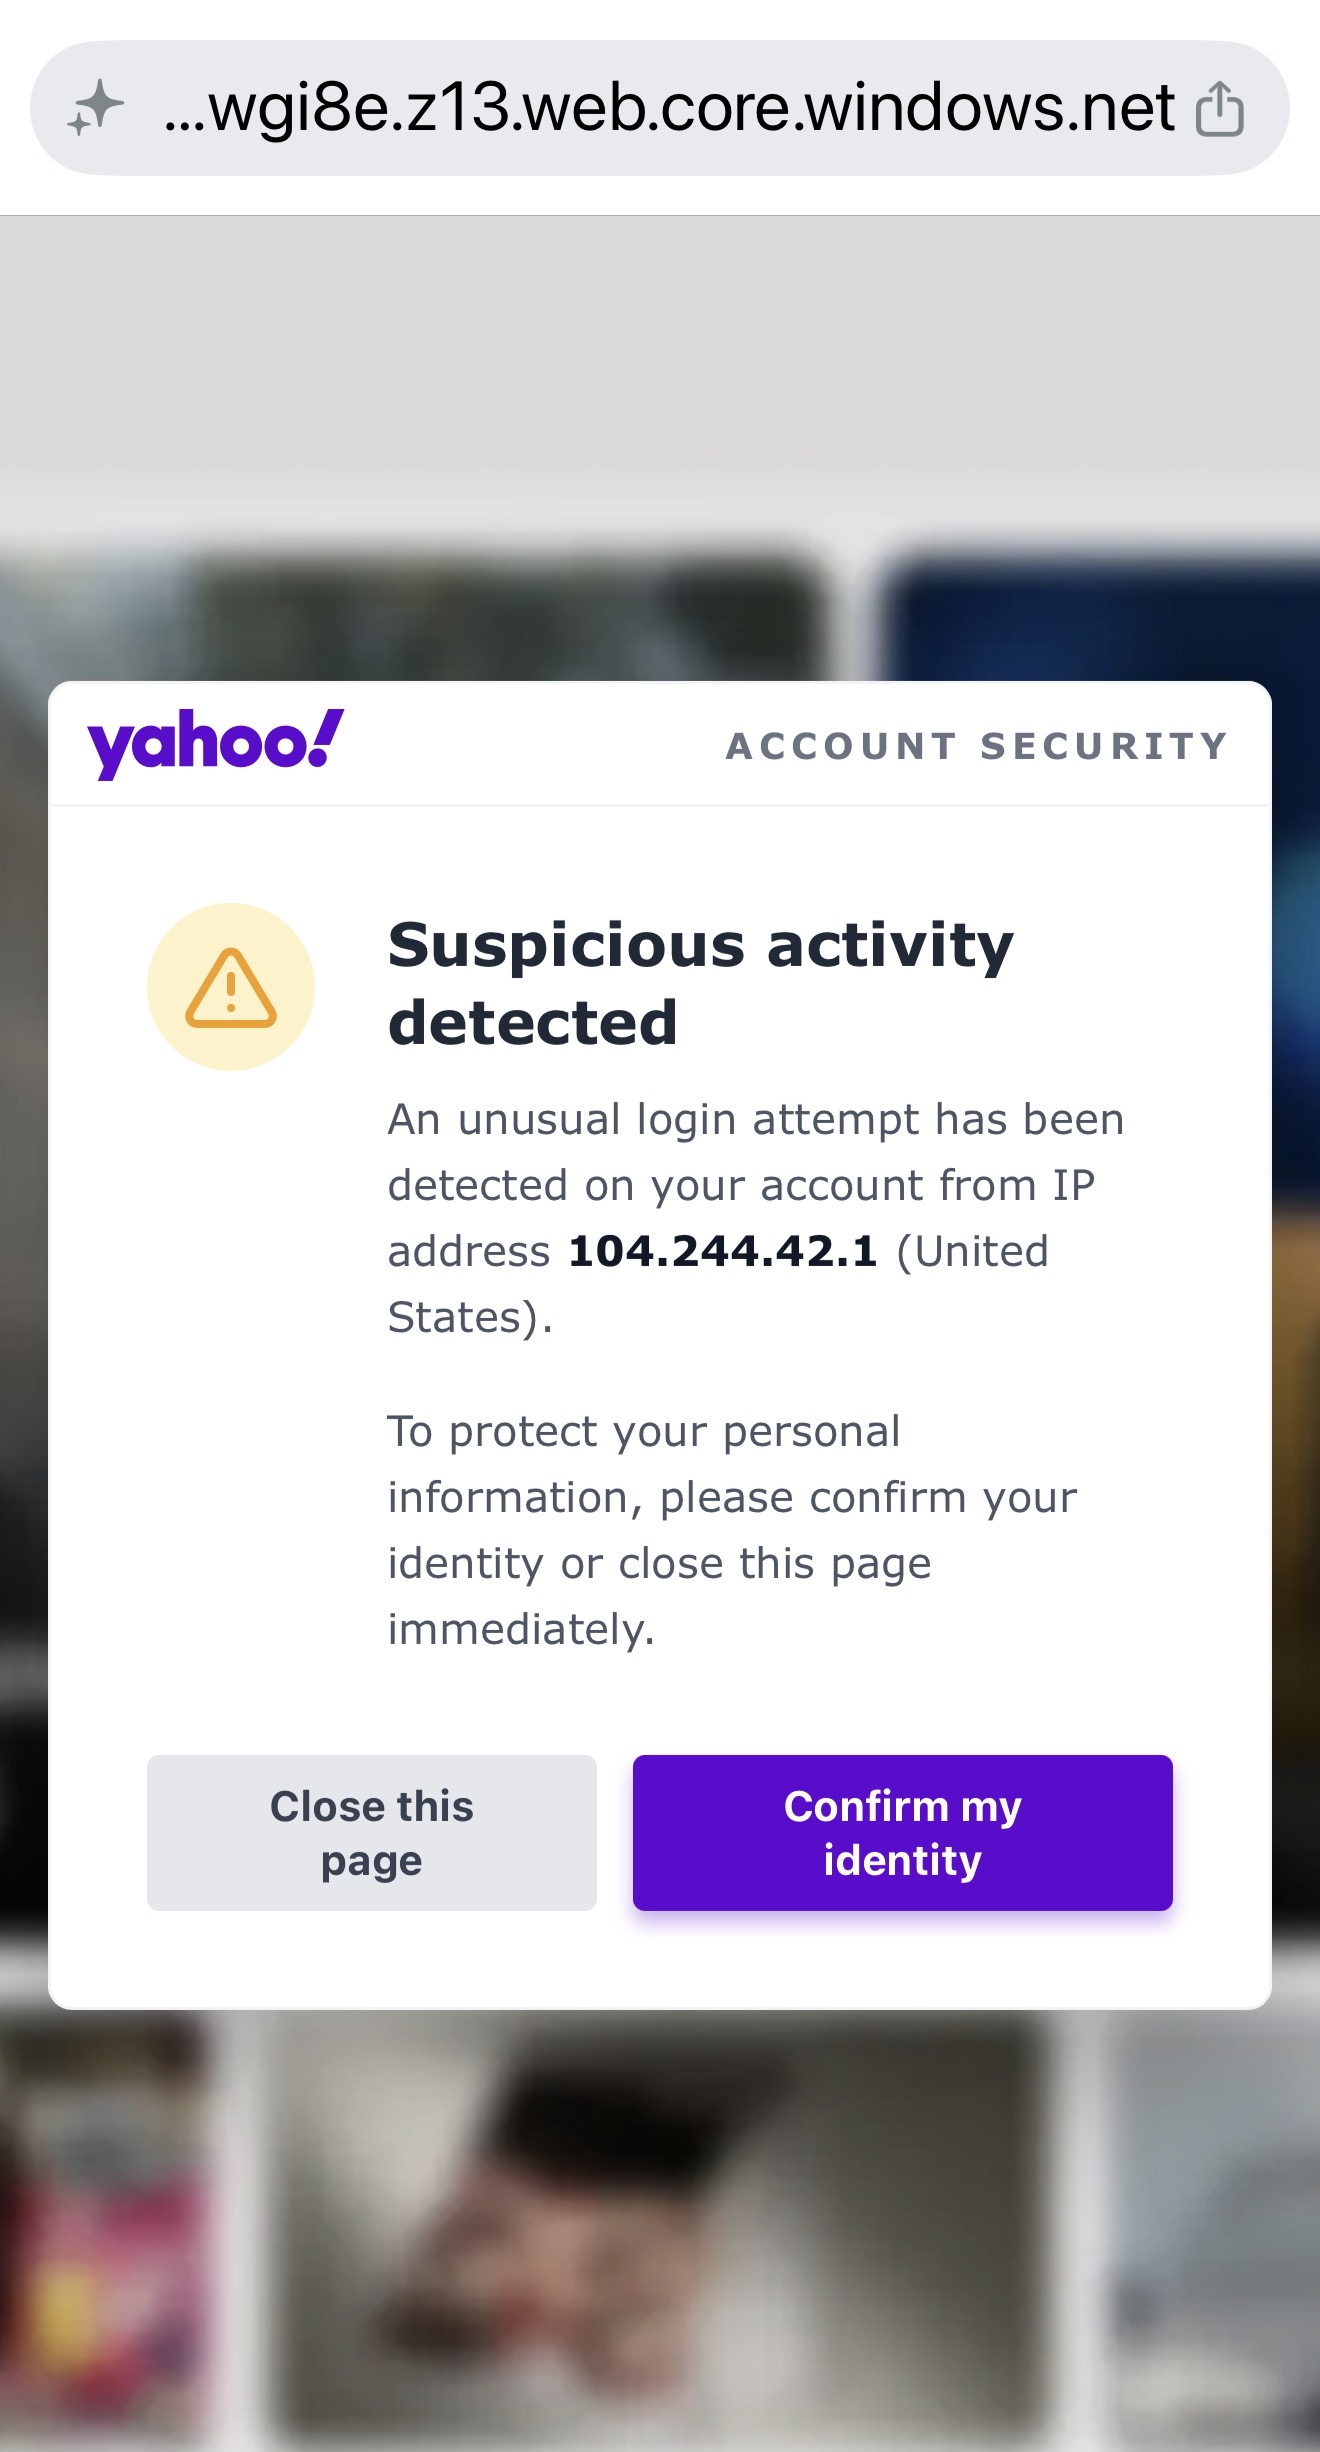 Click the image to view full size
98
Likely scamScam likelihood 98/100
Fake Yahoo/Microsoft security alerts on unrelated 'web.core.windows.net' URL claim suspicious activity, locked session, and urge calling +1 (888)951-7136 immediately, classic tech-support phishing/scam impersonation.
ImpersonationAnalyzed by ChatGPT 5.5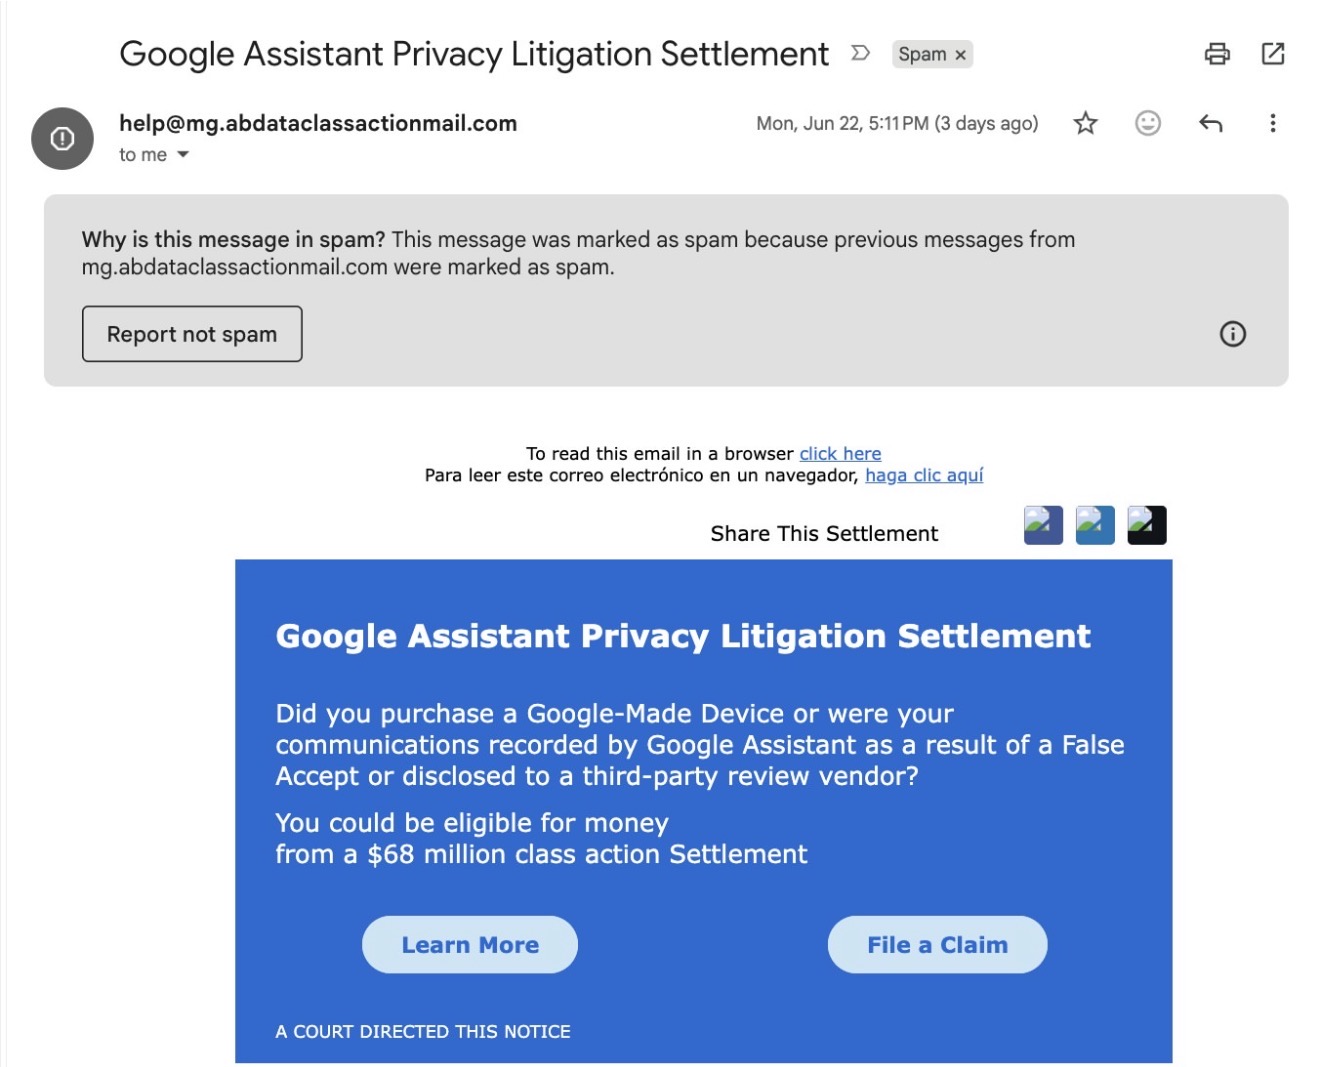 Click the image to view full size
25
Moderate riskScam likelihood 25/100
Appears to be a legitimate class action settlement notice (Google Assistant $68M settlement). Sender domain references AB Data, a known settlement administrator. Marked spam by Gmail, but content matches real court-directed notices. Mild caution due to claim links and spam flag.
ImpersonationAnalyzed by Claude Opus 4.8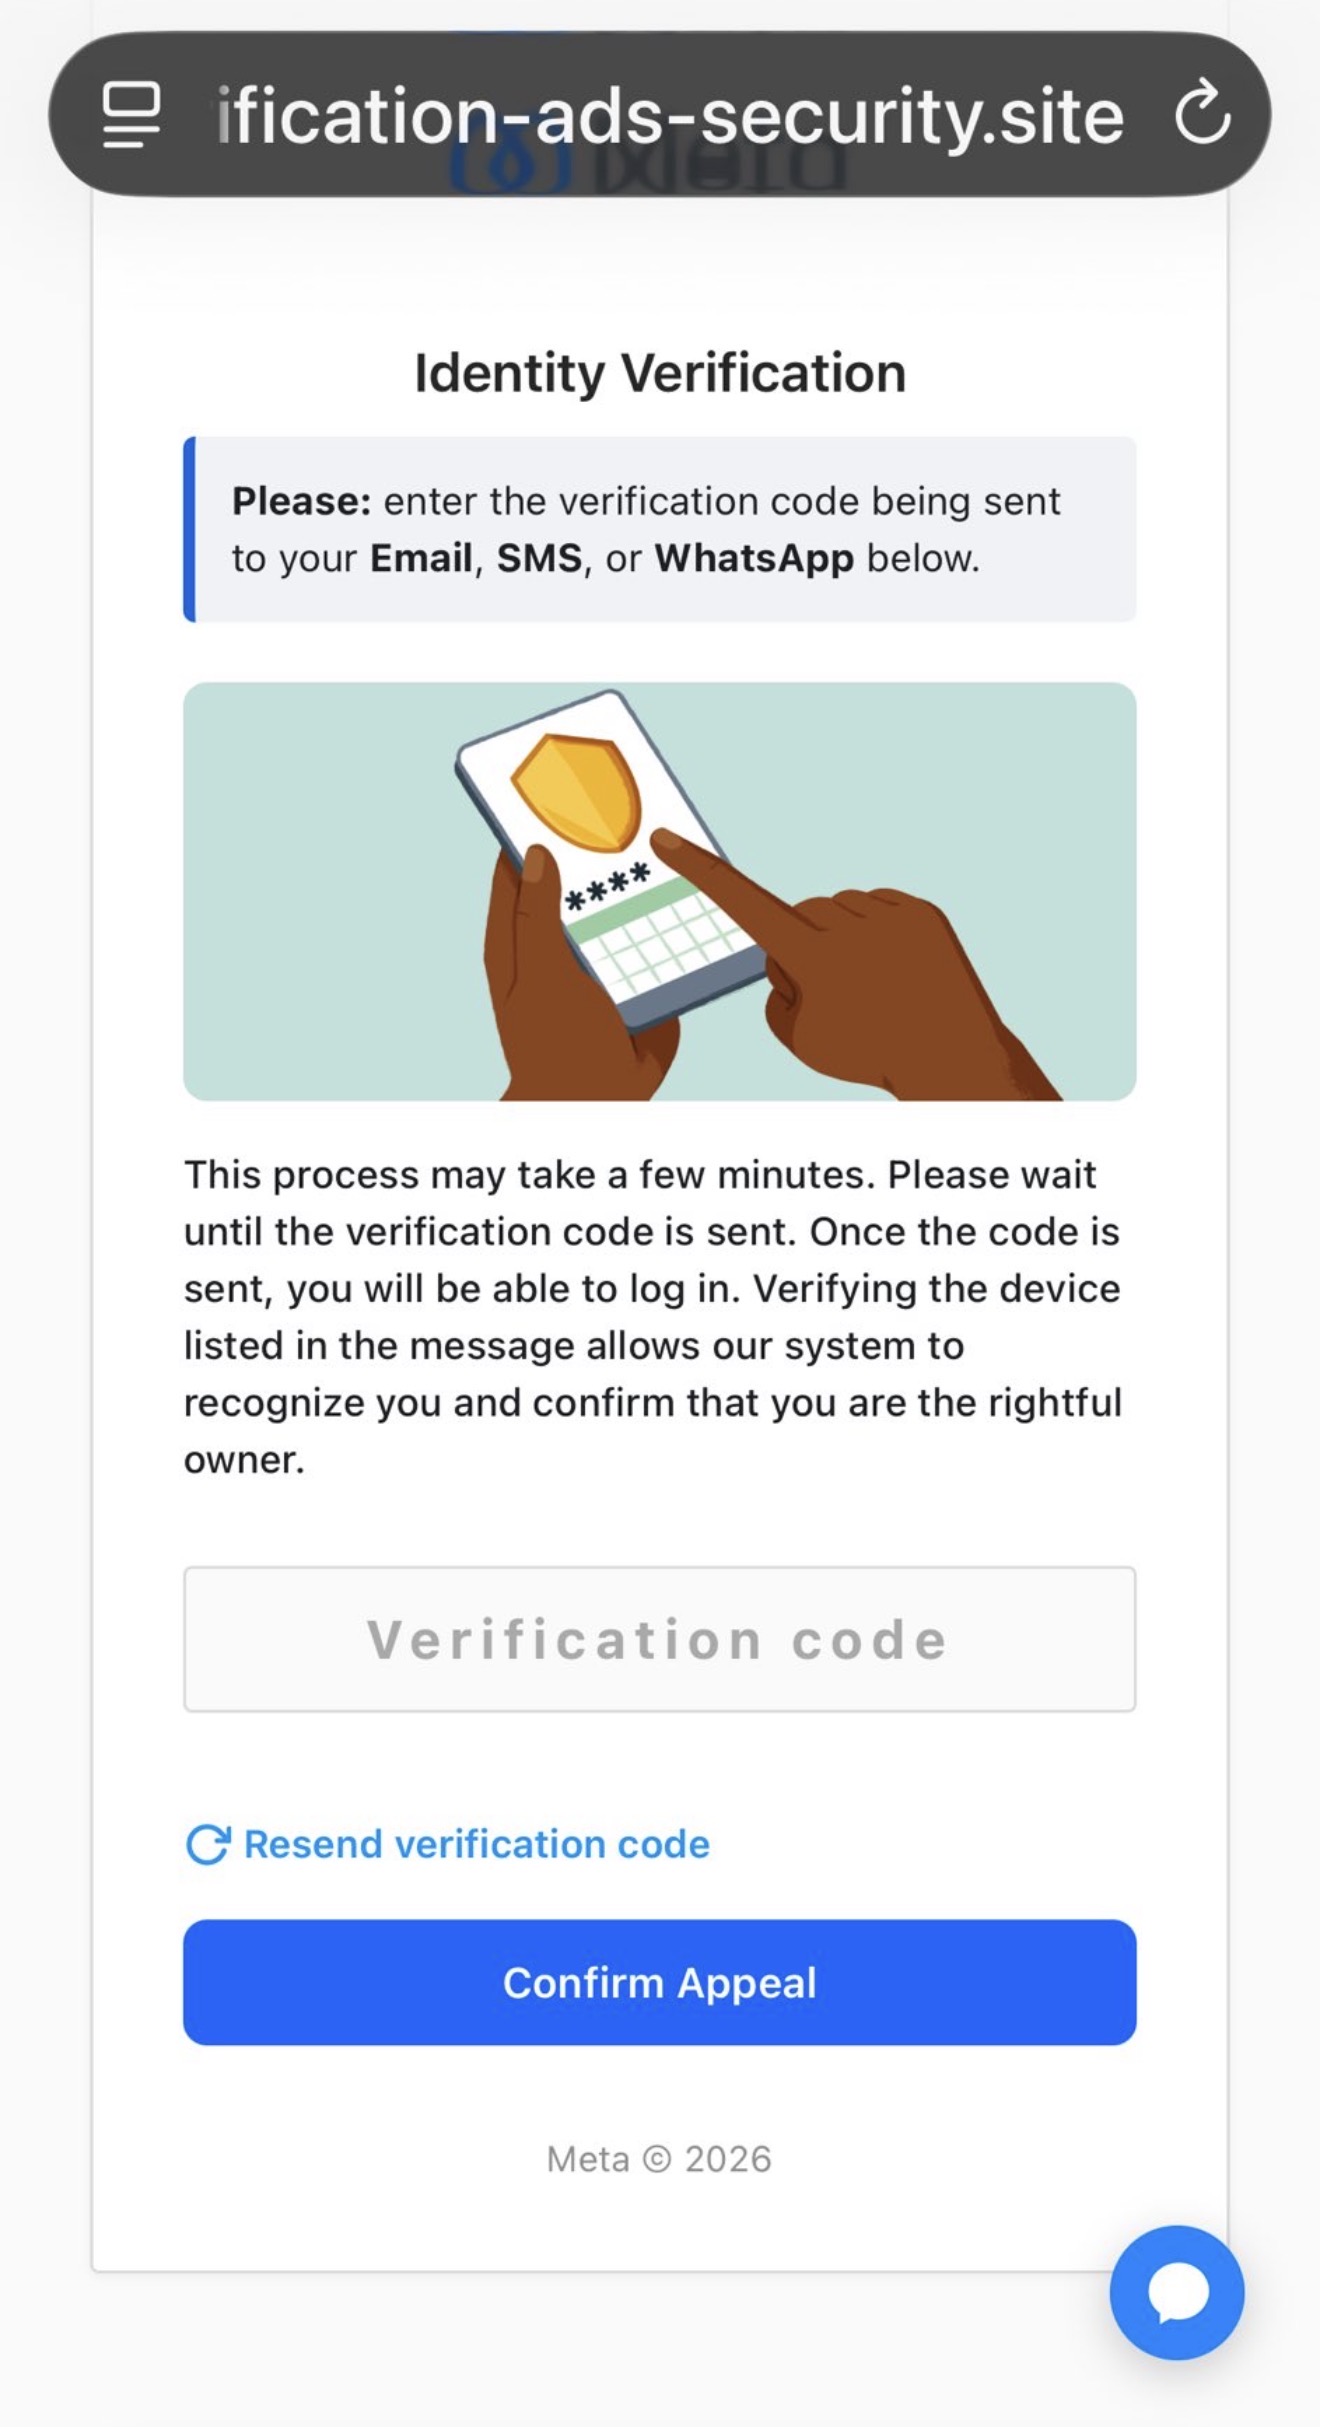 Click the image to view full size
98
Likely scamScam likelihood 98/100
Impersonates Meta/Facebook with non-Meta URL 'ification-ads-security.site', asks user to enter a verification code from Email/SMS/WhatsApp, and uses 'Confirm Appeal' plus 'Meta © 2026'. This is OTP harvesting/phishing.
ImpersonationAnalyzed by ChatGPT 5.5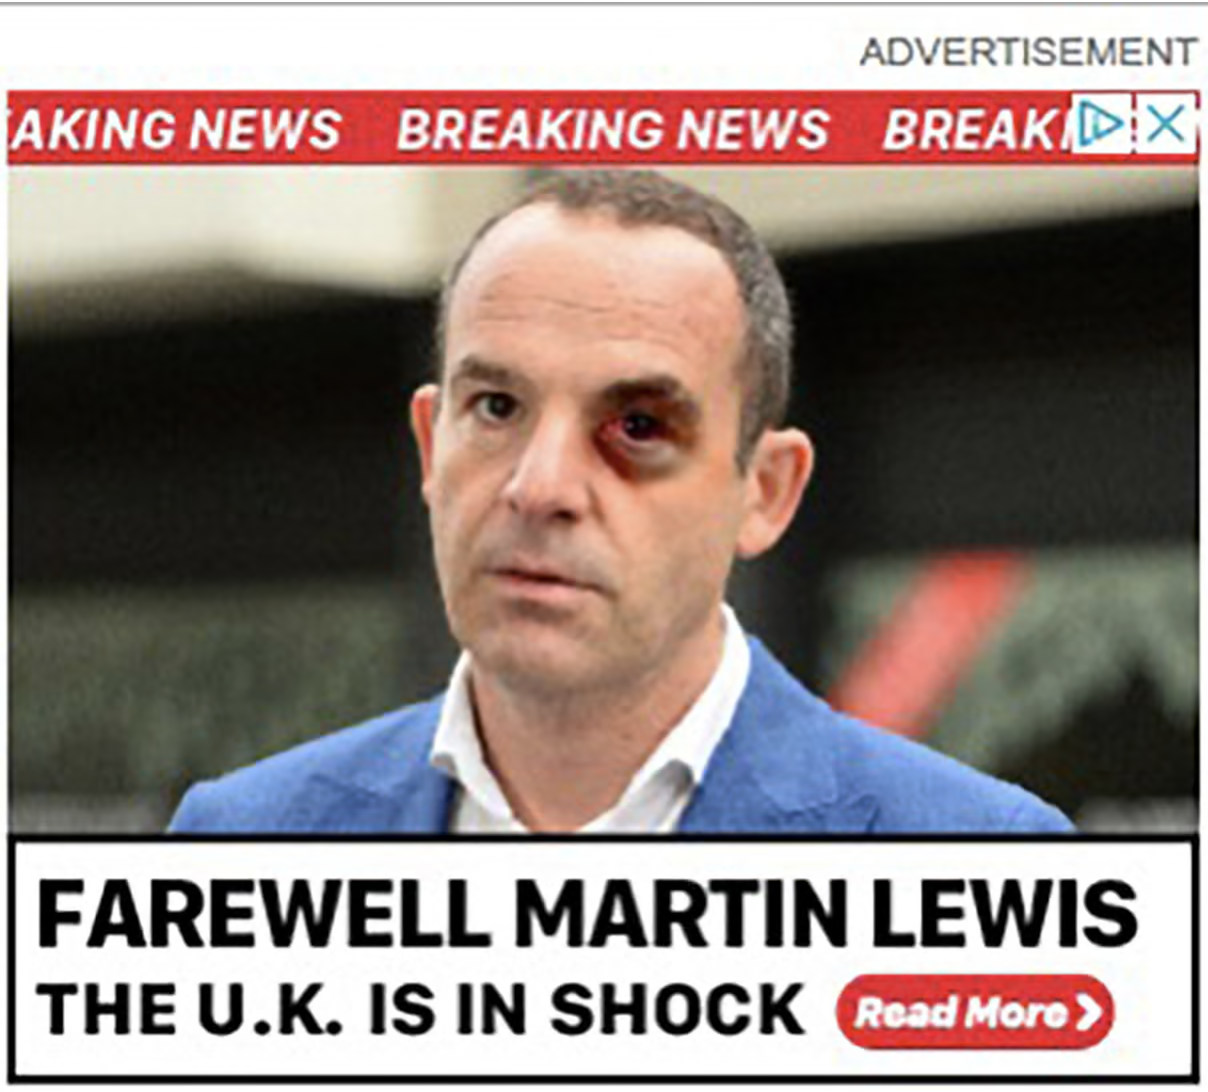 Click the image to view full size
92
Likely scamScam likelihood 92/100
Fake 'Breaking News' advertisement using Martin Lewis image (with fabricated injury) and 'Farewell Martin Lewis, UK in shock' headline. Classic celebrity death/impersonation clickbait used to funnel users into investment or phishing scams via 'Read More'. Misinformation and unauthorized likeness use.
ImpersonationAnalyzed by Claude Opus 4.8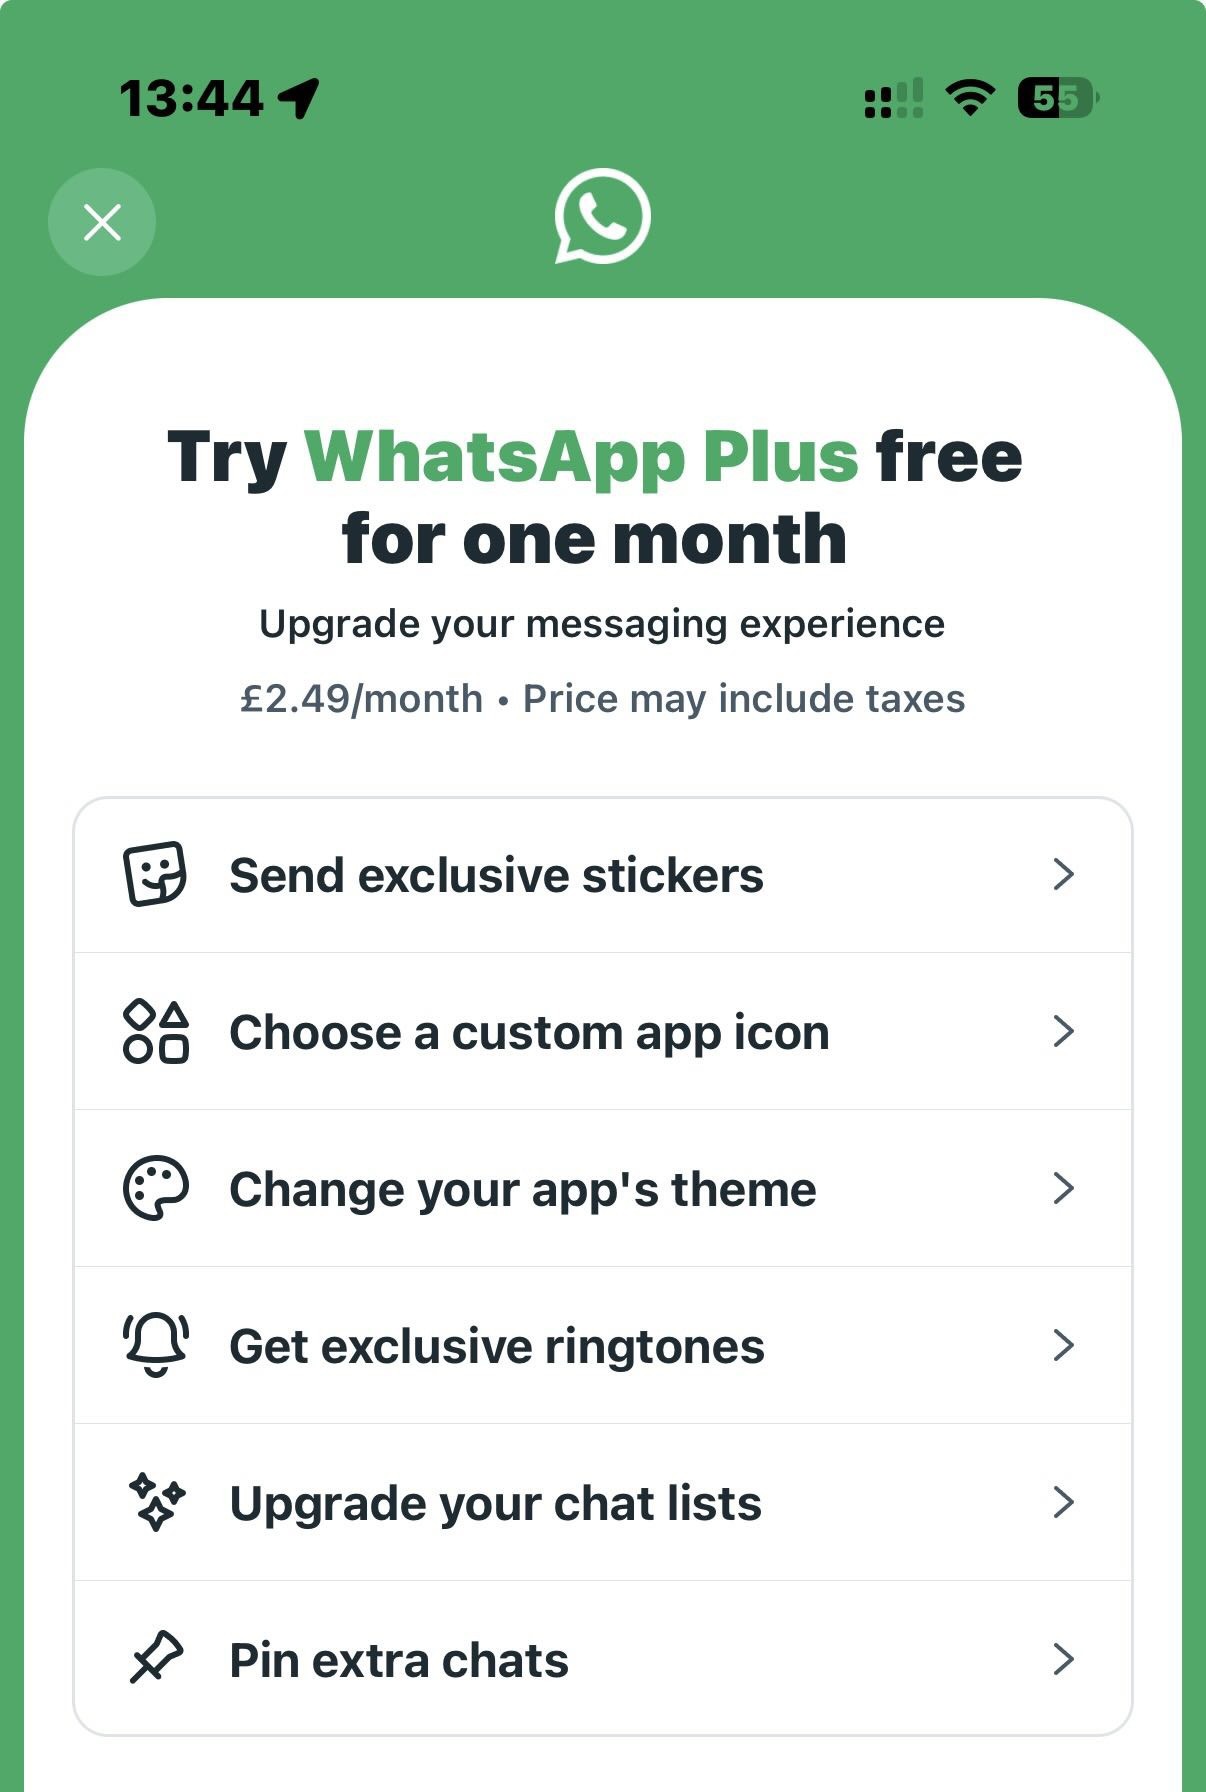 Click the image to view full size
14
Low riskScam likelihood 14/100
Appears to be a genuine in-app WhatsApp Plus subscription screen with native iOS UI, official branding, clear pricing (£2.49/month) and standard feature list. No links, no credential requests, no urgency or impersonation signals.
ImpersonationAnalyzed by Claude Opus 4.8